• Skip to primary navigation
  • Skip to main content
Cleared Cyber Security Jobs | CyberSecJobs.com

Cleared Cyber Security Jobs | CyberSecJobs.com

Cleared Cyber Security Jobs

  • Home
  • Search Cleared Cyber Jobs
  • Job Fairs
  • Career Resources

CyberSecJobs Editorial

CCSP Certification Career Guide for Cleared Cloud Security

CyberSecJobs Editorial · February 14, 2026 ·

The Certified Cloud Security Professional (CCSP) certification, offered by ISC2, is a globally recognized credential for cloud security experts. It’s especially relevant for professionals with security clearances, as it’s officially approved under the U.S. Department of Defense Manual (DoDM) 8140.03 for roles like IAT Level III and IASAE III. With the rise of multi-cloud and hybrid infrastructures in government and defense sectors, the demand for CCSP-certified professionals continues to grow.

Key Highlights:

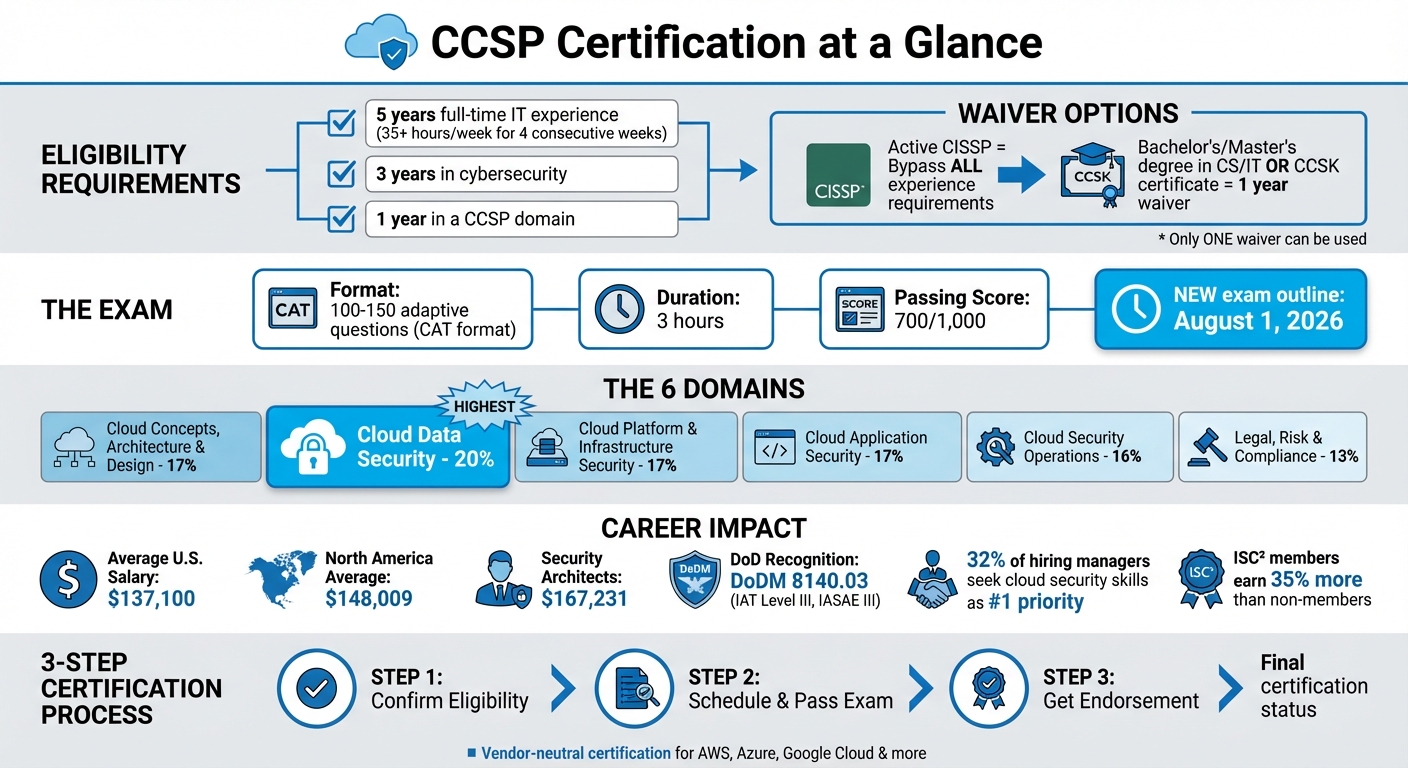
  • Eligibility: Requires five years of IT experience (three in cybersecurity and one in a CCSP domain). CISSP holders can bypass the experience requirement.
  • Exam: 100–150 adaptive questions, three hours, 700/1,000 passing score. A new exam outline takes effect on August 1, 2026.
  • Domains: Six domains, with Cloud Data Security (20%) being the most weighted.
  • Salary: Average U.S. salary of $137,100, with higher earning potential for specific roles like Cloud Architect or Security Engineer.
  • Job Market: High demand in cleared roles such as Cloud Security Analyst and Cloud Engineer, with employers like Lockheed Martin and the U.S. Air Force actively hiring.

The CCSP certification validates expertise across cloud platforms like AWS, Azure, and Google Cloud, focusing on vendor-neutral security practices. It is a critical credential for professionals aiming to secure sensitive government data while advancing their careers in cloud security.
CCSP Certification Requirements and Path to Certification

CCSP Certification Requirements and Path to Certification

What You Need to Know About CCSP Certification

CCSP Certification Overview

The Certified Cloud Security Professional (CCSP) is a globally recognized certification from ISC2. It validates your expertise in designing, managing, and securing cloud environments, including data, applications, and infrastructure. Unlike certifications tied to specific platforms, CCSP applies broadly across all cloud providers, making it especially useful for professionals in sensitive, security-cleared roles.

This certification is accredited by the American National Standards Institute (ANSI) and meets ISO/IEC Standard 17024, ensuring it adheres to international professional standards. It builds on the foundational knowledge from certifications like CISSP (Certified Information Systems Security Professional) and CCSK (Certificate of Cloud Security Knowledge), making it a logical next step for seasoned cybersecurity professionals.

To qualify for the CCSP, you need at least five years of full-time IT experience, including three years in cybersecurity and one year in one of the six CCSP domains. However, if you already hold an active CISSP credential, it waives the entire experience requirement. Additionally, a bachelor’s or master’s degree in computer science or IT, or a CCSK certificate, can substitute for one year of required experience.

The exam includes 100–150 multiple-choice questions administered through Computerized Adaptive Testing (CAT), which adjusts the question difficulty based on your answers. You’ll have three hours to complete the test, and a score of 700 out of 1,000 points is required to pass. Keep in mind that a new exam outline takes effect on August 1, 2026, so plan your preparation accordingly if you’re testing after this date.

The 6 CCSP Knowledge Domains

The CCSP exam is structured around six domains, each focusing on a critical aspect of cloud security. These domains are weighted differently, so understanding their importance will help you allocate your study time effectively.

Domain Weight Focus Area
1. Cloud Concepts, Architecture and Design 17% Cloud roles, reference architectures, security design principles like cryptography and zero trust
2. Cloud Data Security 20% Data lifecycle, encryption, classification, and Information Rights Management (IRM)
3. Cloud Platform & Infrastructure Security 17% Physical/logical infrastructure, secure data center design, and BC/DR strategies
4. Cloud Application Security 17% Secure Software Development Life Cycle (SDLC), Identity and Access Management (IAM), and software assurance
5. Cloud Security Operations 16% Operating and maintaining cloud infrastructure, digital forensics, and security operations
6. Legal, Risk and Compliance 13% Privacy laws, audit processes, and enterprise risk management

Cloud Data Security (Domain 2) carries the most weight at 20%, emphasizing the importance of protecting sensitive information in the cloud. This domain is particularly relevant for professionals handling classified government data, as it covers encryption standards and data classification.

Legal, Risk and Compliance (Domain 6) focuses on navigating privacy laws, international regulations, and compliance standards like Common Criteria (CC) and FIPS 140-2. These are essential for managing data across borders or within government and defense systems.

These domains highlight the specific skills CCSP-certified professionals need to secure cloud environments, especially in multi-cloud setups often used in government and defense roles.

How CCSP Applies to Cleared Positions

The CCSP certification is especially valuable for professionals in government and defense sectors. It’s officially recognized under U.S. Department of Defense Manual (DoDM) 8140.03, qualifying it for various roles like Cloud Architect, Cloud Engineer, Cloud Security Analyst, and Cloud Computing Auditor. This approval ensures it meets the mandatory certification requirements for information workforce positions.

One of CCSP’s key advantages is its vendor-neutral approach. Whether your agency uses AWS, Azure, Google Cloud, or a combination of platforms, you can apply the same security principles and policies across all environments. This adaptability is one reason why CCSP is the fastest-growing ISC2 certification and a top credential professionals aim to earn in 2024.

In multi-cloud environments, which are increasingly common in government agencies, the CCSP’s focus on tenant partitioning and logical design (Domain 3) ensures secure separation of classified and unclassified data. Meanwhile, Domain 5 addresses the operational skills needed for monitoring cloud infrastructure, performing digital forensics, and responding to security incidents – tasks that are critical in cleared roles.

If you pass the exam but don’t yet meet the experience requirements, you can earn the title of Associate of ISC2. This status gives you six years to gain the necessary experience while still showcasing your expertise in cloud security – a valuable distinction even before full certification.

sbb-itb-bf7aa6b

CCSP Eligibility Requirements and Qualification Paths

Experience and Education Requirements

To qualify for the CCSP certification, you’ll need five years of full-time IT experience. Within those five years, three must be in cybersecurity, and at least one year must involve one of the six CCSP domains. To count a month of experience, you must work at least 35 hours a week for four consecutive weeks [8][10].

If you already hold an active CISSP certification, you can bypass the experience requirement entirely and proceed directly to the exam [8][10]. This is the quickest route for professionals who have already earned their CISSP. Additionally, a bachelor’s or master’s degree in computer science, IT, or a related field – or the Cloud Security Alliance‘s CCSK certificate – can replace one year of the required experience [8][10]. However, you can only use one waiver; combining the degree and CCSK substitution is not allowed.

If you pass the exam but lack the full experience, you’ll earn an Associate status, which gives you up to six years to meet the remaining requirements [8][4].

The next step is to ensure you meet the security and ethical standards tied to this certification.

Security Clearance and Ethics Requirements

While security clearance isn’t mandatory for CCSP eligibility, the ISC2 background qualification process aligns with many of the standards required for cleared professionals. You’ll need to disclose any prior disciplinary actions from government agencies or professional organizations, as well as any involvement in criminal or computer-related offenses [11]. The background check also reviews military court-martials and government disciplinary records, which cleared professionals are typically already familiar with [11].

All candidates must agree to follow the ISC2 Code of Ethics to qualify for certification [8]. If you have any concerns about your eligibility – such as past disciplinary issues – reach out to legal@isc2.org before scheduling your exam. Keep in mind that exam fees are non-refundable if you’re later deemed ineligible [11].

For those with non-traditional work arrangements, part-time roles and internships can also help you meet the experience requirements.

How Part-Time Work and Internships Count

If you’ve worked part-time or completed internships, these experiences can also count toward your CCSP eligibility. Part-time work is eligible if you’ve worked between 20 and 34 hours per week. ISC2 calculates 1,040 hours as equivalent to six months of full-time experience, and 2,080 hours as equivalent to a year [8][10]. This is particularly useful for professionals who may have started with part-time roles in government or contractor positions.

Both paid and unpaid internships qualify, provided you can verify them. For internships, you’ll need documentation on official letterhead (or registrar’s stationery for school-based internships) during the endorsement process. If your career began with internships through government agencies or defense contractors, gathering this documentation early can streamline your certification process [8][10].

Introduction | 40-Hour Free CCSP Exam Preparation Tutorial | ISC2 CCSP 2025 Full Course
ISC2

How to Earn Your CCSP Certification

Earning the CCSP certification involves a straightforward process with specific steps to help professionals navigate the requirements effectively.

Step 1: Confirm Your Eligibility

Before diving in, make sure you meet the necessary experience criteria. You’ll need five years of full-time IT experience (at least 35 hours per week for four consecutive weeks), including three years in cybersecurity and one year in a CCSP domain. If you already hold an active CISSP, a qualifying degree, or a CCSK certificate, you can waive one year of this requirement. If you don’t yet meet the full experience requirements, you can still earn Associate status, giving you up to six years to fulfill the remaining criteria [4][8].

Step 2: Schedule and Take the Exam

Once you’ve confirmed your eligibility, the next step is scheduling your exam. Log in to your ISC2 account, select the CCSP exam, pay the fees, and book your test appointment through Pearson VUE [12]. Double-check that your registration details match your government-issued ID exactly – any discrepancies could cause issues on test day, and exam fees are non-refundable [12].

The exam uses Computerized Adaptive Testing (CAT) and includes 100 to 150 multiple-choice and advanced questions. You’ll have three hours to complete it, and you’ll need a score of at least 700 out of 1,000 points to pass [4][9]. Testing centers enforce strict security measures, such as infrared and metal detection wands, to ensure exam integrity [12]. Keep in mind that a new exam outline will take effect on August 1, 2026 [4][1].

Step 3: Get Your Endorsement

After passing the exam, the final step is securing an endorsement. This involves having an ISC2-certified professional verify your qualifications and work experience [4][8]. The endorsement confirms that you meet the required IT experience, including cybersecurity and domain-specific expertise.

If you already hold an active CISSP, this process becomes simpler. For professionals with security clearance, it’s a good idea to identify an ISC2-certified colleague or supervisor beforehand to streamline this step. While security clearance doesn’t replace the endorsement, the CCSP’s recognition under U.S. DoDM 8140.03 makes it a highly respected credential for government and defense positions [1][5].

Cleared Jobs That Require or Prefer CCSP Certification

Common Cleared Cloud Security Positions

The CCSP certification opens doors to a variety of cleared cloud security roles. For instance, Cloud Security Analysts focus on identifying vulnerabilities and ensuring smooth cloud operations, often requiring active security clearance. Meanwhile, Cloud Architects and Cloud Engineers are responsible for designing and implementing secure cloud infrastructures, which frequently support intricate government systems.

Other roles, such as Enterprise Architects and Security Engineers, also often list the CCSP as a preferred or required credential. In January 2026, companies like Akumen Inc. and Resource Management Concepts Inc. advertised onsite Cloud Security Engineer positions in Washington, D.C., and Crane, Indiana, respectively [13]. These postings highlight how CCSP-certified professionals influence salary trends and the broader job market, which are explored next.

Salary Expectations and Job Market Outlook

In North America, CCSP-certified professionals command impressive salaries. On average, they earn $148,009 per year. Specific roles demonstrate even higher earning potential: Security Architects average $167,231 annually, Information Security Managers make around $129,063, and Information Security Analysts start at approximately $89,502 [14][15].

Demand for cloud security expertise in the cleared market remains strong. A notable 32% of cybersecurity hiring managers rank cloud computing security as the most sought-after skill in potential hires [6]. Additionally, ISC² members report earning salaries that are 35% higher than their non-member counterparts [13]. Prominent employers like Lockheed Martin Aeronautics Company, Microsoft Corp, and the U.S. Air Force actively recruit CCSP-certified professionals [15]. This consistent demand highlights the certification’s importance in government and defense sectors.

CCSP Value in Government and Defense Work

The CCSP certification holds particular significance in government and defense roles. It is officially recognized under U.S. DoDM 8140.03 [5][7], making it a key qualification for military and government contractors. Its vendor-neutral design allows professionals to work seamlessly across various cloud platforms, a critical advantage for agencies managing multi-cloud or diverse environments.

The certification’s emphasis on Legal, Risk, and Compliance aligns with stringent defense regulatory standards. As government agencies increasingly migrate critical assets to the cloud, many now require CCSP certification as a hiring prerequisite. Additionally, the certification’s rigorous approval process and adherence to the ISC² Code of Ethics ensure that CCSP holders are well-equipped to handle sensitive government data [13]. This makes the CCSP an essential credential for professionals working in the cleared cybersecurity space.

Study Resources and Exam Preparation Tips

ISC2 Official Study Materials

Once you’ve met the certification requirements and scheduled your exam, it’s time to focus on preparing effectively. The ISC2 Official Study Guide (3rd Edition) is an excellent starting point, as it covers all the exam objectives and includes practice tests. Pair it with the Official (ISC)2 CCSP CBK Reference (3rd Edition) for a deeper dive into the six domains, offering vendor-neutral insights that complement your study sessions.

Practicing exam questions is a must. The ISC2 official practice tests feature over 1,000 questions, helping you build stamina and pinpoint areas needing improvement [17][20]. For on-the-go learning, the Pocket Prep app is a handy tool, offering quick quizzes and earning a stellar 4.8/5 rating on the App Store [18]. If you’re an auditory learner, consider video training from ITPro.tv with Adam Gordon – it’s perfect for listening during your commute [17].

Support Networks for Cleared Professionals

Don’t underestimate the value of community support when preparing for the CCSP exam. Platforms like Reddit’s r/CCSP and various Discord channels provide access to real-time advice, pinned study notes, and shared experiences from others on the same journey [17]. These communities are especially useful for professionals who need to maintain operational security while seeking guidance.

Another helpful resource is the Cloud Security Alliance (CSA) Guidance v4.0, which includes the Cloud Controls Matrix (CCM). This reference is particularly useful for understanding concepts that frequently appear on the exam [17][19]. While not an official ISC2 resource, it’s highly relevant for those working with government cloud implementations, as it aligns closely with federal compliance standards.

Balancing Study Time with Work Demands

Selecting the right resources is just one part of the equation – managing your study time effectively is just as important. Most candidates dedicate 3 to 6 months to focused preparation, spending 10 to 20 hours per week studying [16][17]. With fewer than 10,000 CCSP holders worldwide compared to over 150,000 CISSP holders [17], it’s clear this certification requires a strategic approach.

"The CCSP tests more than just your technical knowledge – it evaluates your understanding of cloud security from a vendor-neutral perspective, your grasp of risk management principles, and your ability to think strategically." – John Berti, Co-founder, Destination Certification [16]

Start by taking a baseline practice test to identify your strengths and weaknesses. Then, apply the 60/30/10 rule: devote 60% of your study time to weaker areas, 30% to moderate ones, and 10% to reviewing what you’re already confident in [16]. Use tools like the Pocket Prep app to make the most of idle moments [17][18]. Aim to consistently score around 80% on practice tests before scheduling your exam. This ensures you’re ready and helps avoid "study drift" [17]. For professionals working in environments like AWS GovCloud or Azure Government, it’s crucial to shift focus from platform-specific knowledge to broader, vendor-neutral security principles [16].

Advancing Your Career with CCSP Certification

Finding CCSP Jobs on Cleared Cyber Security Jobs
Cleared Cyber Security Jobs

Once you’ve earned your CCSP, it’s time to connect with employers who recognize the value of your expertise. Cleared Cyber Security Jobs is a specialized platform designed to link security-cleared professionals with government agencies and defense contractors actively hiring for cloud security roles. By using the platform’s search filters, you can zero in on positions like Cloud Security Engineer, Cloud Architect, or Cloud Security Analyst – roles where a CCSP certification is often highly regarded.

To stand out, upload your resume with your CCSP credential and security clearance details. This can help you meet requirements such as DoD 8140.03 IAT Level III and IASAE III. Setting up job alerts with keywords like “CCSP” or “Cloud Security” can also help you stay ahead in a competitive market. Considering that 64% of organizations have identified cloud security as a top priority for 2025 [2], this proactive approach can give you a significant edge. But remember, landing the job is just the beginning – maintaining your certification is just as important.

Keeping Your CCSP Certification Current

Getting your CCSP is just the first step; keeping it current is essential. To maintain your certification, you’ll need to recertify every three years by earning Continuing Professional Education (CPE) credits and paying an Annual Maintenance Fee of $125. Staying up to date not only fulfills certification requirements but also ensures you’re prepared to address new challenges in cloud security. This is especially critical as threats like Ransomware-as-a-Service and shifting cloud architectures continue to evolve.

For busy professionals, ISC² Express Courses and Certificates offer a convenient way to earn CPE credits while managing a demanding schedule. Additionally, keep in mind that the CCSP exam outline will be updated on August 1, 2026 [5]. Staying informed about these changes will help you maintain your edge in the industry.

Career Success Stories from CCSP-Certified Professionals

Maintaining your CCSP certification can open doors to impressive career opportunities and financial rewards. On average, CCSP-certified professionals in North America earn $148,009 annually [2]. But it’s not just about the paycheck – this certification also paves the way for leadership roles. With a CCSP, cleared professionals are well-positioned for advanced roles like Cloud Architect, Auditor of Cloud Computing Services, or Security Consultant. These roles often involve working with high-profile organizations, from government agencies and defense contractors to major enterprises like JPMorganChase and Swiss Re.

One of the standout features of CCSP certification is its vendor-neutral approach. This equips you with the skills to secure multicloud environments across platforms like AWS, Azure, and Google Cloud [3]. Whether you’re protecting a single cloud or managing complex multicloud systems, the CCSP ensures you’re ready to tackle the challenges ahead.

Conclusion

The CCSP certification is a smart career choice for professionals with security clearances looking to specialize in cloud security. With its recognition by the Department of Defense under DoDM 8140.03, its vendor-neutral approach to multicloud environments, and its focus on six critical knowledge areas, the CCSP can open doors to roles like Cloud Architect, Cloud Security Analyst, and Cloud Consultant. In the U.S., professionals holding this certification earn an average salary of $137,100, placing it among the top 15 highest-paying credentials [3].

As the demand for cloud security experts grows and the cybersecurity skills gap persists, having a CCSP certification gives you a distinct edge in the hiring process [21]. Whether you’re tasked with securing government systems, protecting defense contractor networks, or managing complex multicloud setups, the CCSP demonstrates your expertise in designing, managing, and safeguarding critical assets using globally recognized best practices [1].

These credentials can directly translate into career growth. Platforms like Cleared Cyber Security Jobs connect security-cleared professionals with government agencies and defense contractors seeking cloud security specialists. By uploading your resume with your CCSP certification and clearance details, and setting up targeted job alerts, you can position yourself for opportunities tailored to your unique qualifications.

Take the step to earn your CCSP, stay current with professional development, and connect with employers who value your security clearance and cloud security skills. With the CCSP exam outline set to update on August 1, 2026, this is the perfect time to advance your certification journey [5].

FAQs

Is CCSP worth it if I already have a security clearance?

Earning the CCSP certification holds strong value, even if you already have a security clearance. It showcases advanced knowledge in cloud security, which is increasingly critical as more organizations shift to cloud environments. This certification not only opens doors to better career opportunities but also aligns with the rising demand for professionals with both cloud security expertise and clearance. It’s a great way to distinguish yourself in the cybersecurity field and prove your dedication to staying current with technical skills.

What cleared roles does CCSP help me qualify for under DoD 8140.03?

The CCSP certification prepares professionals for a variety of roles within cloud security, aligning with the DoD 8140 framework. These roles include responsibilities in cloud security architecture, design, operations, and service orchestration. Certified individuals may work on managing and securing cloud environments, overseeing cloud operations, or handling procurement and cloud service management tasks.

Should I take the CCSP exam before or after the August 1, 2026 update?

It’s a good idea to take the CCSP exam before August 1, 2026, since a new exam outline will be implemented after that date. Preparing for the current version could be easier, as new outlines typically bring changes to the content and areas of emphasis.
Related Blog Posts

  • Classified Cloud Security Jobs – AWS GovCloud and Azure Government Specialization
  • GSEC Certification Career Guide for Cleared Security Essentials
  • Security Plus Certification Career Guide for Cleared Entry Level
  • CySA Plus Certification Career Guide for Cleared SOC Analysts

Related Guides

  • GCP Security Certification for Cleared Cloud Architects
  • Azure Security Engineer Certification for Cleared Professionals
  • AWS Security Specialty Certification for Cleared Cloud Engineers
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

PenTest Plus Certification Career Guide for Cleared Pen Testers

CyberSecJobs Editorial · February 13, 2026 ·

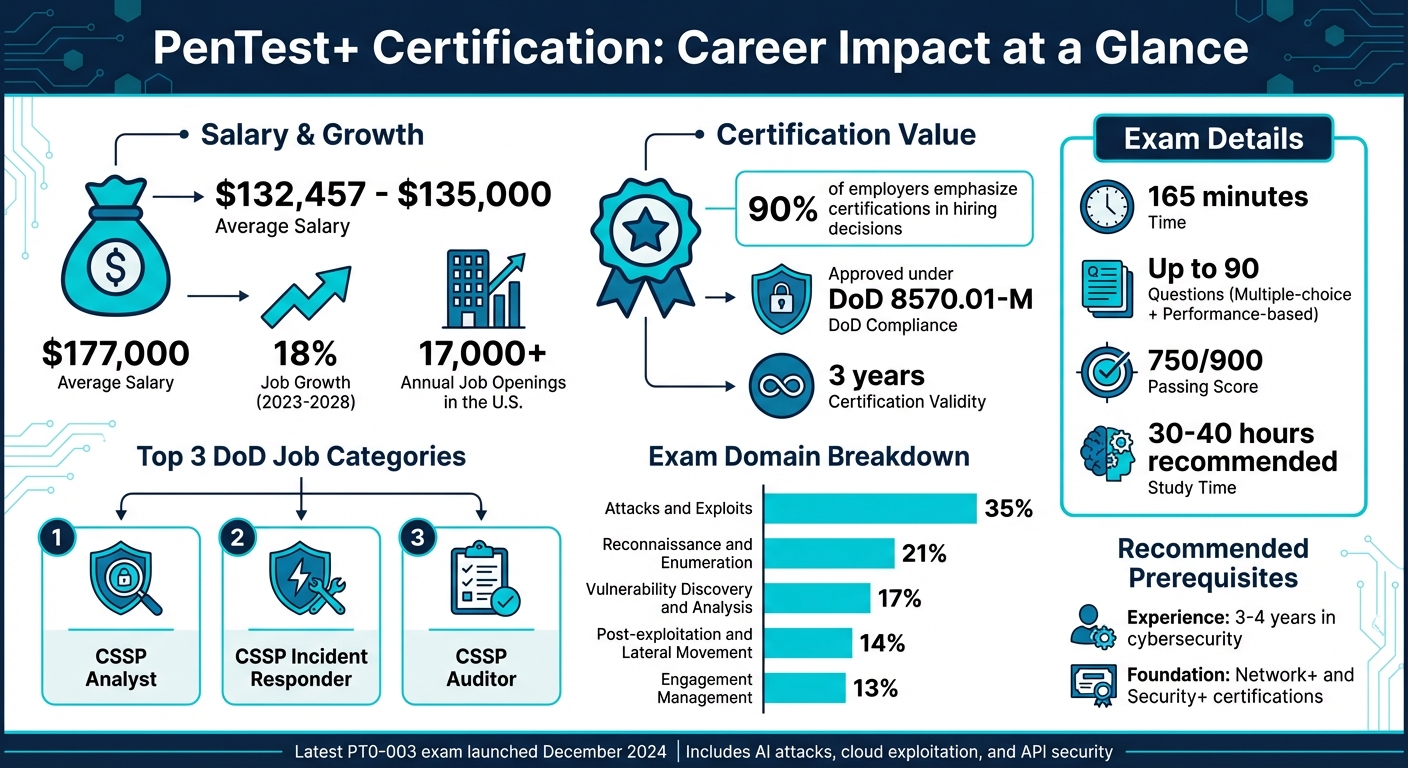
If you’re aiming for offensive cybersecurity roles within government or defense sectors, the CompTIA PenTest+ certification is a must-have. Approved under DoD 8570.01-M, it qualifies you for critical job categories like CSSP Analyst, CSSP Incident Responder, and CSSP Auditor. With an average salary of $132,457 and projected job growth of 18% (2023–2028), penetration testing is a lucrative and growing field.

This intermediate-level certification tests skills in penetration testing, vulnerability assessments, and compliance – key for cleared environments. The latest PT0-003 exam, launched in December 2024, includes modern topics like AI attacks, cloud exploitation, and API security. It’s performance-focused, requiring hands-on expertise in tools like Nmap, Nessus, and Metasploit.

For preparation:

  • Experience: 3–4 years in cybersecurity roles recommended.
  • Resources: Use CompTIA Labs, CertMaster Practice, and official study guides.
  • Exam Details: 90 questions (multiple-choice and performance-based), 165 minutes, passing score of 750/900.

Top employers like Northrop Grumman and Johns Hopkins APL actively seek PenTest+ holders for roles in penetration testing, vulnerability assessments, and red team operations. With over 17,000 job openings annually, this certification boosts your eligibility for high-demand cleared positions.

Ready to advance your career? Focus on building hands-on skills, meeting DoD compliance, and leveraging job platforms tailored to cleared professionals.

PenTest+ Certification Career Statistics and Salary Guide 2024

PenTest+ Certification Career Statistics and Salary Guide 2024

What is CompTIA PenTest+ Certification?

CompTIA

PenTest+ Certification Overview

CompTIA PenTest+ is an intermediate-level certification in offensive cybersecurity, tailored for professionals with hands-on experience. Unlike certifications that focus only on finding vulnerabilities, PenTest+ evaluates your ability to handle the entire penetration testing process – from planning and scoping to managing vulnerabilities, conducting post-exploitation tasks, and delivering detailed reports [2][12].

This certification is ANSI accredited, adheres to ISO 17024 standards, and aligns with the NICE Cybersecurity Workforce Framework, making it essential for roles outlined in DoD 8140 [9][3]. Its alignment with these frameworks underscores its importance in government and defense settings.

What sets PenTest+ apart is its use of performance-based assessments. These tests go beyond theory, requiring you to demonstrate practical, job-ready skills that reflect the demands of real-world penetration testing roles [3].

Now, let’s dive into the exam domains, which mirror the workflow of a professional penetration tester.

Exam Domains and Skills Covered

The PT0-003 exam includes up to 90 questions, combining multiple-choice and performance-based formats. You’ll have 165 minutes to complete the test, and a passing score is 750 on a scale of 100–900 [11]. The exam focuses on five key domains that reflect the real-world tasks of a penetration tester:

Exam Domain Weight Key Skills
Attacks and Exploits 35% Network, host-based, web app, cloud, and AI attacks; authentication attacks
Reconnaissance and Enumeration 21% Active/passive recon, OSINT, DNS enumeration, script modification (Python, PowerShell, Bash)
Vulnerability Discovery and Analysis 17% Authenticated/unauthenticated scans, SAST/DAST, result validation
Post-exploitation and Lateral Movement 14% Persistence, lateral movement, cleanup, attack narratives
Engagement Management 13% Planning, scoping, legal/ethical compliance, reporting

The latest version (PT0-003), introduced on December 17, 2024, includes AI-specific attacks such as prompt injection and model manipulation [11]. It also emphasizes the ability to modify scripts (Python, PowerShell, Bash) to address modern environments like cloud platforms and IoT devices [11].

These domains clearly illustrate why PenTest+ is indispensable for professionals working in sensitive environments.

Why PenTest+ Matters for Cleared Roles

PenTest+ is officially recognized under DoD 8570.01-M, qualifying holders for three crucial job categories: CSSP Analyst, CSSP Incident Responder, and CSSP Auditor [3][1]. According to CompTIA, "military personnel and defense contractors who work with sensitive information can take CompTIA PenTest+ to satisfy specific job requirements" [3]. Without this certification, many cleared positions may not be accessible.

The certification’s focus on legal and ethical compliance is especially important when working with sensitive government and defense systems [3][11]. It equips you with the skills to plan and execute penetration tests within regulatory guidelines, document findings accurately, and present results effectively to stakeholders – essential capabilities for cleared environments. Additionally, PenTest+ aligns with the NICE Framework, ensuring a smooth transition to the DoD 8140 manual [3].

Beyond penetration testing roles, PenTest+ prepares you for positions like vulnerability assessment analyst, application security vulnerability specialist, and network security operations roles [3][9]. It serves as a stepping stone between foundational certifications like Security+ and advanced credentials such as SecurityX (formerly CASP+), particularly for those pursuing offensive cybersecurity roles on the "red team" side of the field [3].

sbb-itb-bf7aa6b

How to Prepare for the PenTest+ Certification

Prerequisites and Experience Requirements

You don’t need any specific certifications or degrees to take the PenTest+ exam – there are no mandatory prerequisites [5][15]. That said, CompTIA suggests having 3–4 years of hands-on experience in penetration testing or related areas of information security before attempting this certification [11][13].

It’s also helpful to build a solid foundation with CompTIA Network+ and Security+ certifications before diving into PenTest+ [11][14]. Since this certification focuses on offensive security and practical technical skills, it’s designed as a natural step after Security+. For those in cleared roles, PenTest+ holds additional value as it’s approved for DoD 8570.01-M compliance, qualifying you for positions like CSSP Analyst, CSSP Incident Responder, and CSSP Auditor [3].

Study Materials and Training Resources

Once your foundational knowledge and experience are in place, the next step is gathering and using the right study tools. Start by downloading the official PT0-003 exam objectives. This will help you pinpoint areas where your skills or knowledge might need improvement [5][14]. CompTIA recommends setting aside 30 to 40 hours for focused study before taking the exam [14].

Practical, hands-on practice is key. Use CompTIA Labs to work with tools like Nmap, Wireshark, and Nessus, which are essential for tackling the performance-based questions on the exam [11][3]. These labs are especially useful for learning how to test devices in environments like the cloud and mobile platforms, alongside traditional setups. As CompTIA explains:

The certification requires a candidate to demonstrate the hands-on ability and knowledge to test devices in new environments, such as the cloud and mobile, in addition to traditional desktops and servers [3].

For additional preparation, try CertMaster Practice, which provides adaptive testing to help identify weak points and confirm you’re ready for the exam [3]. CompTIA also offers bundles that combine CertMaster Learn, CertMaster Practice, and the Official Study Guide, which can save you money [5]. If you’re in the U.S. military, check with Pearson VUE to see if you’re eligible to take the exam at an on-base testing center [5].

Exam Preparation Tips

Once you’ve reviewed the materials and practiced thoroughly, focus on refining your test strategy. Buy your exam voucher early and schedule your test date – this creates accountability and prevents procrastination [3].

Spend extra time on performance-based questions by practicing in lab environments. Use tools like Metasploitable and DVWA (Damn Vulnerable Web App) to sharpen your exploitation techniques [17]. Get comfortable with tools like Nmap for scanning, Metasploit for exploitation, Burp Suite for web testing, Wireshark for packet analysis, and SQLMap for SQL injection [17].

When taking the exam, tackle the multiple-choice questions first to secure quick points. Then, circle back to the more complex performance tasks [17]. Pay close attention to the Engagement Management domain, as it emphasizes reporting and compliance – critical skills for roles in DoD environments [11][14]. Make sure you’re also familiar with new PT0-003 topics, such as AI-based attacks (like prompt injection), cloud exploitation, and API abuse [16][17].

Keep in mind that the current PT0-003 version of the exam launched on December 17, 2024, and the older PT0-002 version will be retired on June 17, 2025 [11]. Once certified, your credential is valid for three years and can be renewed through Continuing Education units or by earning a higher-level certification like CompTIA SecurityX [14].

Career Benefits of PenTest+ for Cleared Professionals

Skills You’ll Gain from PenTest+

Earning the PenTest+ certification equips you with practical skills tailored for classified environments. For starters, you’ll master planning and scoping, which involves setting secure boundaries for assessments. The certification also covers the legal and compliance aspects crucial for adhering to Department of Defense (DoD) regulations – an absolute must for defense-related work.

You’ll sharpen your ability to identify vulnerabilities, not just in traditional networks but also across modern platforms like cloud, mobile, and IoT systems. The attacks and exploits section provides hands-on practice in simulating cyberattacks to pinpoint weaknesses. Even more importantly, you’ll learn how to translate technical findings into clear, actionable insights. As CompTIA puts it:

A penetration tester, or pen tester, is considered a white hat or good hacker. Although they must think like a bad guy, the end goal is to enhance organizational security [7].

The certification also validates your expertise with penetration testing tools and your ability to adjust strategies throughout different testing phases. What sets PenTest+ apart is its emphasis on hands-on skills, certifying your ability to operate at an intermediate level [3].

These capabilities open the door to a wide range of cleared roles.

Cleared Job Roles That Require PenTest+

The skills you gain with PenTest+ translate directly into high-demand roles that offer competitive salaries. The certification aligns with over seven roles outlined in the NICE Framework, such as Vulnerability Assessment Analyst, Cyber Defense Analyst, and Security Controls Assessor [3].

Job Role Key Responsibilities Salary Range
Penetration Tester Conducts simulated cyberattacks, uncovers vulnerabilities in networks and applications, and performs social engineering tests $132,457 – $135,000 [4][18]
Vulnerability Assessment Analyst Performs network scans, evaluates risks, applies patches, and drafts technical reports ~$104,000 [12]
Security Analyst II Monitors systems, detects anomalies, and generates detailed reports ~$96,000 [12]
CSSP Incident Responder Investigates security breaches and analyzes attack methods $110,000+ [4]
Cybersecurity Engineer Designs secure systems and tests defenses by exploiting vulnerabilities $110,000+ [4]

Top employers like Johns Hopkins University Applied Physics Laboratory, Northrop Grumman, and SecureWorks actively seek professionals with PenTest+ certification [7][9]. With over 17,000 U.S. job openings for penetration testers in a 12-month period [18] and 90% of employers emphasizing the importance of certifications in hiring decisions [6], this credential significantly boosts your job prospects.

Advancing to Senior Positions

Beyond entry and mid-level roles, PenTest+ positions you for advancement into senior offensive security roles. For example, it can lead to Red Team Operator positions, where you’ll conduct advanced adversary simulations. You could also move into Senior Security Engineer roles, designing and testing enterprise-level defense mechanisms.

The demand for cybersecurity professionals in the cleared sector is growing rapidly, with an 18% projected increase in job openings for cybersecurity analysts between 2023 and 2028 [4]. Penetration testers can expect median salaries around $135,000 [18]. Since PenTest+ is considered an intermediate-level credential, pairing it with advanced certifications like SecurityX (CASP+) can fast-track your promotion to senior positions, which often require five or more years of experience [3]. Additionally, the DoD’s increasing focus on "red team" capabilities highlights the rising need for offensive security expertise [3].

Finding PenTest+ Jobs on Cleared Cyber Security Jobs

Using Job Search Filters

Cleared Cyber Security Jobs makes it easier to find roles requiring the PenTest+ certification with its skill-based search filters. Simply type "PenTest+" or "CompTIA PenTest+" into the keyword or skill search bar to get started [20]. You can also search for roles with titles like "Penetration Tester", "Cyber Security Engineer", "Cyber Analyst", or "Red Cyber Operator" [23,27]. To refine your search further, use AI-driven matching and Boolean search options to align with your certifications and clearance level [20]. Filters like location (e.g., Maryland or Virginia, with high-demand cities such as Herndon, VA, and Linthicum, MD) and employers (e.g., Booz Allen Hamilton, CACI, Leidos, and Northrop Grumman) can help you zero in on the most relevant opportunities [23,24,27]. These tools are designed to help you maximize the value of your PenTest+ certification in finding top cleared roles.

Showcasing Your Certification

Recruiters often review your profile before accessing your full resume [21]. To make a strong impression, highlight that your PenTest+ certification meets DoD 8570.01-M requirements, as this compliance is crucial [9]. As CompTIA advises, "Certification makes a great first impression" [9]. Make sure your resume is uploaded and that PenTest+ is listed in your skills section to enable AI-driven matching with recruiters [24,25]. You can also set up job alerts by saving searches for "PenTest+" to receive email notifications about new roles [21].

G.B., a Technical Project Manager at CACI, points out the value of attending Cleared Job Fairs, especially for veterans transitioning into civilian careers: "For veterans especially, attending Cleared Job Fairs can be critical to a successful career transition" [21]. After optimizing your profile, take advantage of upcoming events and additional career tools offered by the platform.

Platform Resources for Cleared Professionals

The platform offers more than just job listings – it provides resources to expand your opportunities. Cleared Cyber Security Jobs hosts virtual and in-person job fairs, giving you a chance to connect directly with recruiters. Upcoming events include an in-person job fair on March 5, 2026, in Herndon, VA, and another on April 16, 2026, in Falls Church, VA [19]. For those unable to attend in person, a virtual hiring event is scheduled for February 19, 2026, focusing on the Huntsville area [20]. Be sure to upload your resume and tag it to the specific event so employers can easily find you [20].

Additional resources include career tools like "The Cleared Professional Podcast" and industry news updates to keep you informed about defense trends and certification requirements [24,26]. For instance, in January 2026, Tabitha Hancock of UberEther shared insights on the podcast about what federal agencies look for in standout candidates [19]. If you’re outside major hubs, virtual events provide a fantastic way to connect with top contractors across the country [20].

Full CompTIA PenTest+ (PT0-003) Module 1 | Engagement Management | CompTIA PenTest+ Exam Prep Course

Conclusion

The CompTIA PenTest+ certification is tailored for professionals in penetration testing roles, particularly those with security clearances. Approved under DoD directive 8140/8570.01-M [7], this certification qualifies you for government-mandated roles in defense and federal contracting. It demonstrates your capability to manage every stage of penetration testing – from planning to exploitation and reporting – while addressing modern challenges like cloud environments, APIs, and AI-related threats [10][11].

The field offers strong career and financial growth, supported by key industry metrics [4][8]. Beyond traditional penetration testing roles, the PenTest+ certification opens doors to positions such as Vulnerability Assessment Analyst, Security Analyst (II), and Application Security Vulnerability Specialist.

CompTIA emphasizes that certifications are crucial for staying competitive [22]. In fact, 9 out of 10 employers agree that certifications are critical when hiring, and IT-certified professionals are more likely to secure promotions [22]. These factors highlight the certification’s role in advancing your cybersecurity career.

To maximize the benefits of your PenTest+ certification, take advantage of Cleared Cyber Security Jobs’ specialized tools. Use skill-based search filters to find roles requiring PenTest+, showcase your DoD compliance on your profile, and connect with recruiters at upcoming job events. Whether you’re launching your career in penetration testing or targeting a senior position, combining your PenTest+ certification with an active security clearance sets you up for success in this high-demand field.

FAQs

Is PenTest+ enough to qualify for DoD 8570/8140 roles?

Yes, PenTest+ is officially approved by the Department of Defense (DoD) for specific roles under the 8570/8140 framework. It qualifies individuals for positions such as:

  • CSSP Analyst
  • Incident Responder
  • Auditor

This approval underscores its importance for professionals seeking cybersecurity roles within the DoD framework, particularly those requiring security clearances.

What hands-on labs should I practice for PT0-003?

Building practical skills is key to passing the PT0-003 (PenTest+) exam. Here are some hands-on labs that can help you prepare:

  • CertMaster Labs for PenTest+ PT0-003: These virtual labs let you work with tools, networks, and cloud environments while staying aligned with the exam’s objectives.
  • Reconnaissance Tools Practice: Get familiar with tools like Nmap, Wireshark, and Shodan to sharpen your information-gathering techniques.
  • Scenario-Based Labs: Dive into realistic penetration testing scenarios to practice vulnerability scanning, exploitation, and creating detailed reports.

These labs provide the practical experience needed to master the essential skills for the exam.

How do I prove cleared pen testing experience on my resume?

To highlight your cleared penetration testing experience, make sure to prominently display your active security clearance level (like Top Secret or TS/SCI) near the top of your resume. You can include it in your professional summary or even alongside your contact information. Additionally, emphasize that your work was performed under clearance by mentioning it in your job titles or project descriptions. This makes it easier for employers to see that you’re qualified for roles requiring clearance.

Related Blog Posts

  • OSCP Certification Career Guide for Cleared Offensive Security
  • GPEN Certification Career Guide for Cleared Penetration Testers
  • Security Plus Certification Career Guide for Cleared Entry Level
  • CySA Plus Certification Career Guide for Cleared SOC Analysts

Related Guides

  • CRTL Certification Career Guide for Cleared Red Team Leads
  • CRTO Certification Career Guide for Cleared Red Team Operators
  • CRTP Certification Career Guide for Cleared Red Team Professionals
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

CASP Plus Certification Career Guide for Cleared Security Architects

CyberSecJobs Editorial · February 13, 2026 ·

Looking to advance your career as a cleared security architect? The CASP+ certification, now rebranded as CompTIA SecurityX, is a hands-on, performance-based credential tailored for high-level cybersecurity professionals. Officially launched on December 17, 2024, SecurityX aligns with DoD Directive 8140/8570.01-M, making it a key qualification for roles like Security Architect, Systems Requirements Planner, and Security Control Assessor.

Key Highlights:

  • Focus Areas: Security architecture, engineering, operations, and compliance.
  • Exam Details: 90 questions, 165 minutes, pass/fail grading.
  • Relevance: Approved by the U.S. Department of Defense for critical cybersecurity roles.
  • Experience Needed: 10 years of IT work (5+ in security).
  • Career Impact: Opens doors to cleared roles with employers like the U.S. Army, Booz Allen Hamilton, and Verizon.

With cloud-based threats surging by 110% annually, SecurityX equips you to tackle challenges in automation, Zero Trust, and advanced cryptography. Whether you’re aiming to design secure systems or enhance your technical expertise, this certification positions you for success in high-demand, cleared cybersecurity roles.

CompTIA SecurityX is here (CASP+ is no more): What you need to know

CompTIA

sbb-itb-bf7aa6b

CASP+ Certification and Exam Overview

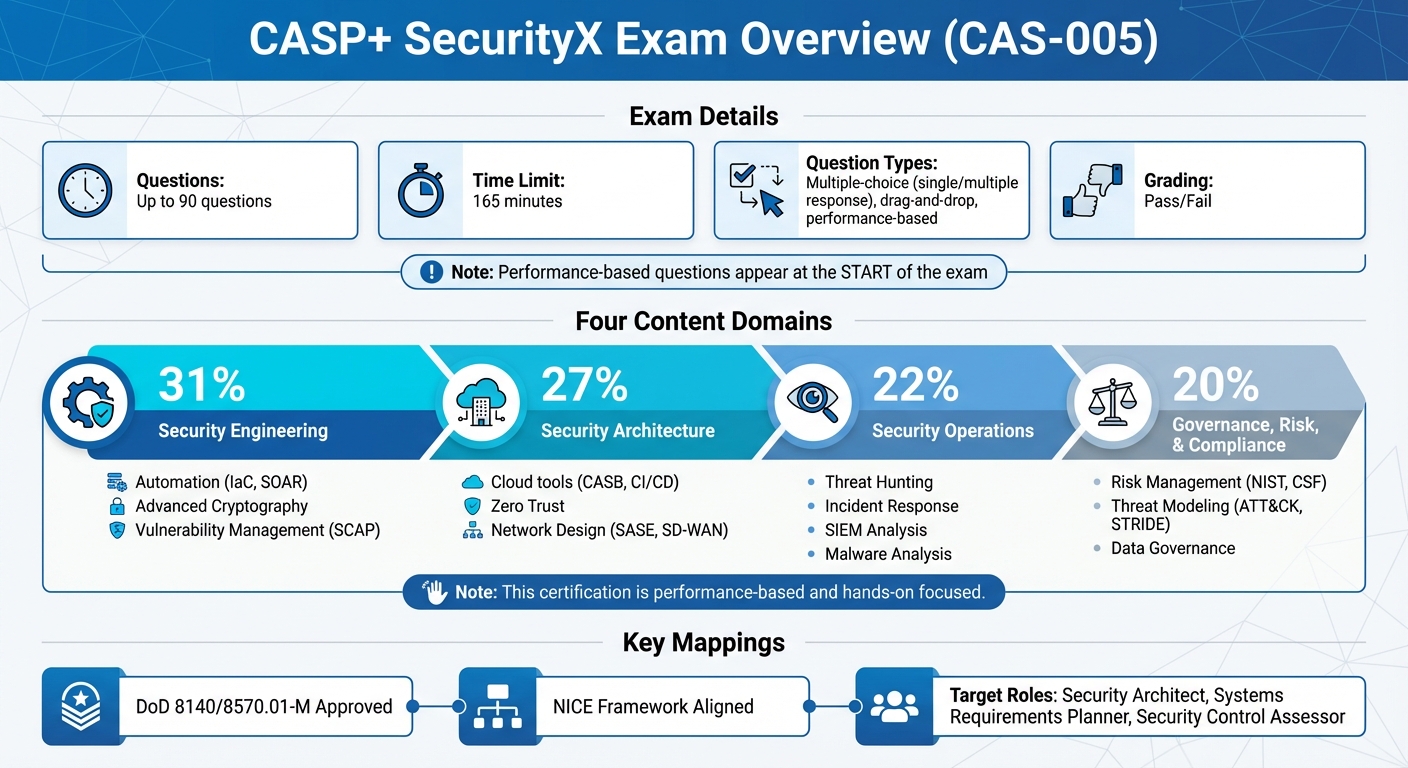
CASP+ SecurityX Exam Domains and Content Breakdown

CASP+ SecurityX Exam Domains and Content Breakdown

Exam Format and Content Domains

The SecurityX exam (CAS-005) includes up to 90 questions, which candidates must complete within a 165-minute time limit [1]. The question types are varied, featuring multiple-choice (both single and multiple response), drag-and-drop, and performance-based items. Unlike many other CompTIA exams, this one is graded on a pass/fail basis rather than a scaled score.

Performance-based questions, which simulate real-world technical problem-solving, appear at the start of the exam. During these tasks, the on-screen clock is hidden, so managing your time effectively is crucial. Additionally, an optional exit survey follows the exam, consisting of about 12 multiple-choice questions aimed at gathering feedback on your study experience.

The exam content is divided into four main domains, each weighted to reflect the expertise required for security architects:

Domain Weight Key Focus Areas
Security Engineering 31% Automation (IaC, SOAR), Advanced Cryptography, Vulnerability Management (SCAP)
Security Architecture 27% Cloud tools (CASB, CI/CD), Zero Trust, Network Design (SASE, SD-WAN)
Security Operations 22% Threat Hunting, Incident Response, SIEM Analysis, Malware Analysis
Governance, Risk, & Compliance 20% Risk Management (NIST, CSF), Threat Modeling (ATT&CK, STRIDE), Data Governance

These domains collectively assess the technical skills and strategic knowledge expected of advanced security architects.

Relevant Areas for Security Architects

Looking closer at the domain breakdown, several areas stand out as particularly relevant to security architects.

In the Security Engineering domain, which carries the highest weight at 31%, there’s a strong focus on automation and scripting. Proficiency in languages like PowerShell, Bash, or Python is essential, as well as a deep understanding of Infrastructure as Code (IaC) principles.

The Security Architecture domain, weighted at 27%, directly aligns with the responsibilities of a security architect. This section emphasizes designing secure systems for cloud, on-premises, and hybrid environments. Expect questions about Secure Access Service Edge (SASE), microsegmentation, and Zero Trust models. Familiarity with cloud-specific tools, such as Cloud Access Security Brokers (CASB) and shadow IT detection, is also critical.

The remaining domains – Security Operations (22%) and Governance, Risk, & Compliance (20%) – cover areas like threat hunting, incident response, and risk management. These sections incorporate frameworks such as NIST and CSF, ensuring that candidates are prepared for roles requiring advanced risk assessment and compliance strategies.

This certification is mapped to NICE and DoD 8140 work roles, including Security Architect, Systems Requirements Planner, and Security Control Assessor, reinforcing its importance for professionals in high-level security positions.

Prerequisites and Who Should Pursue CASP+

Experience Requirements for Cleared Professionals

CompTIA suggests 10 years of IT experience, with at least five years in security, before attempting CASP+ (now SecurityX) [8]. While there are no strict prerequisites, this certification is not geared toward recent graduates or those just starting their careers.

The exam assumes a strong understanding of topics covered in certifications like CompTIA Network+, Security+, CySA+, Cloud+, and PenTest+ [8]. To succeed, you should already be familiar with areas like identity and access management (IAM), cryptographic tools like SSL/TLS and PKI, networking basics such as TCP/IP, and key security technologies like firewalls and VPNs. If you’re still building these skills, a good path is to begin with Security+ (roughly two years of experience), followed by CySA+ or PenTest+ (three to four years) before tackling CASP+ [10].

Unlike certifications aimed at management roles, CASP+ is tailored for advanced practitioners who prefer staying hands-on with technology rather than shifting into purely leadership positions. Meeting these criteria ensures you’re well-prepared to use CASP+ as a way to propel your career forward.

How CASP+ Fits Your Career Path

CASP+ is the next logical step for senior security engineers and cleared security architects tasked with designing, building, and implementing secure systems in complex environments [2]. It’s also recognized by the U.S. Department of Defense as meeting Directive 8140/8570.01-M requirements, aligning with key roles like Security Architect, Systems Requirements Planner, and Security Control Assessor [8].

According to CompTIA, around 32% of certification holders report earning raises, promotions, or other benefits after completing their certification [8]. For professionals in federal contracting or government roles, CASP+ showcases your ability to combine high-level security strategy with hands-on technical execution – a skill set that’s becoming increasingly critical in positions requiring both architectural vision and practical implementation.

Why CASP+ Matters for Cleared Security Architects

DoD 8570 Compliance and Approval

CASP+ (recently rebranded as CompTIA SecurityX as of December 17, 2024) holds approval from the U.S. Department of Defense (DoD) under Directive 8140/8570.01-M. This makes it a required baseline certification for many roles involving privileged access in the cleared sector [4][5]. Specifically, the certification aligns with the Information Assurance System Architecture and Engineering (IASAE) specialty levels within the DoD 8570 framework – key for professionals in security architecture [11].

According to DoDM 8140.03, SecurityX is recognized for 31 critical roles, including Security Architect and Systems Security Analyst. Starting February 2025, all DoD civilian employees and military service members in Defense Cyber Workforce Framework roles must meet these updated qualifications.

What makes SecurityX stand out is its combined focus on security architecture and engineering concepts. This dual approach prepares professionals to both design and implement secure systems – an essential skill set in high-security environments. Cleared employers highly value this certification for roles that demand technical expertise and compliance with DoD standards. Beyond meeting these stringent requirements, SecurityX also positions individuals for career progression in the cybersecurity field.

Career Growth in Cleared Positions

Beyond its DoD compliance, SecurityX plays a pivotal role in career advancement for cleared professionals. It paves the way for senior roles that demand a blend of technical expertise and strategic vision. Unlike certifications aimed at managerial skills, SecurityX focuses on preparing practitioners for roles like Security Architect or Senior Security Engineer. CompTIA emphasizes this distinction:

"SecurityX is the only hands-on, performance-based certification for practitioners – not managers – at an advanced skill level of cybersecurity" [6].

Additionally, 90% of employers rely on certifications to identify top talent [4]. The updated SecurityX V5 exam reflects current trends, such as AI, automation with PowerShell/Python/Bash, and Zero Trust architecture [7]. These skills are vital, especially as cloud-related cyber threats have surged by 110% year-over-year [5]. With these capabilities, SecurityX-certified professionals are well-equipped to maintain a technical edge in an ever-evolving threat landscape, ensuring their expertise remains indispensable in cleared roles.

How to Prepare for the CASP+ Exam

Study Materials for Cleared Professionals

To get ready for the CASP+ exam, start with the CompTIA Official Study Guide and CertMaster Learn. These resources are designed to match the latest exam objectives, ensuring you cover everything you need to know [13][14]. Since the exam includes performance-based scenarios, focus especially on the hands-on skills required. Pay close attention to the four major domains, with Security Engineering and Security Architecture making up a hefty 58% of the test [7][12].

For practical experience, platforms like Qwiklabs and TryHackMe are excellent for tackling real-world security scenarios [13]. You can also use tools like VirtualBox or VMware to set up sandbox environments. These are perfect for practicing tasks like configuring firewalls, managing incidents, and working with encryption [13]. This hands-on approach mirrors the challenges you’ll face in cleared cybersecurity roles.

If you’re looking for additional resources, check out the "CompTIA CASP+ Study Guide" by Mike Meyers or the "CASP+ CompTIA Advanced Security Practitioner Study Guide" by Wm. Arthur Conklin [13]. These guides not only dive into exam content but also help you prepare for the practical tasks discussed in the next section.

Study Planning and Time Management

Once you’ve gathered your materials, creating a structured study plan is key to success. Break your study sessions into 45 to 60-minute blocks, followed by 10 to 15-minute breaks. This method, often called the Pomodoro Technique, can help you stay focused and retain more information [13]. Since performance-based questions are time-consuming and appear at the start of the exam, practice solving them in simulated environments to build both speed and confidence [9]. Full-length practice exams – taken under timed conditions and without notes – are another great way to simulate the test day experience [13].

Use the official exam objectives to evaluate your current knowledge. Spend extra time on areas you find challenging, such as advanced cryptography or cloud control strategies [12][13]. To make your study time even more effective, relate your daily work tasks to the exam content. For example, apply concepts like risk assessment, cloud configuration, or log analysis to your current projects [15]. Finally, consider joining CASP+ study groups on platforms like Reddit or LinkedIn. These communities are great for exchanging tips and discussing complex topics with others preparing for the exam [13].

Finding Cleared Jobs with CASP+ Certification

Using Cleared Cyber Security Jobs

Once you’ve earned your CASP+ certification, the next step is putting it to work to land the right cleared position. Platforms like Cleared Cyber Security Jobs can help you showcase your clearance level and technical expertise to recruiters. This tool highlights your CASP+/SecurityX credential, clearance status, and key skills, using an AI-powered engine that combines Boolean and semantic criteria for better job matching. You can refine your job search by clearance level (Secret, TS/SCI, or TS/SCI with polygraph), location, and technical skills. The platform also features virtual and in-person hiring events, giving you opportunities to expand your professional network.

Common Cleared Roles for CASP+ Holders

The CASP+ certification opens doors to a variety of cleared roles that align with DoD 8140/8570.01-M standards, including positions at IAT Level III and IASAE levels [3][18]. Your validated expertise makes you a strong candidate for these critical roles. For example, Security Architect positions are in demand, where you’ll design secure IT infrastructures and develop enterprise-wide strategies [16][17]. Other roles include Technical Lead Analyst, where you’ll guide teams in assessing security risks and implementing solutions, and Application Security Engineer, focusing on securing CI/CD pipelines and containerized environments.

Employers such as the U.S. Army, U.S. Navy, Booz Allen Hamilton, Leidos, and Northrop Grumman frequently seek professionals with CASP+ certification. Holding a TS/SCI clearance can significantly boost your earning potential, with salaries averaging 40.6% higher and reaching up to $148,314 for those with a Full Scope Polygraph [18].

"SecurityX is the industry standard for advanced-level competency for technical professionals who wish to remain immersed in technology as opposed to strictly managing." – CompTIA [4]

Renewing Your CASP+ Certification

Keeping your SecurityX certification (formerly CASP+) up to date is just as important as earning it in the first place. This ensures you remain compliant and skilled for cleared roles. The certification is valid for three years [20]. To maintain your status and meet DoD 8140/8570 compliance, you’ll need to earn 75 Continuing Education Units (CEUs) within that three-year period [20]. This is the highest CEU requirement among CompTIA certifications, reflecting the advanced level of this credential [22].

There are two ways to renew your certification. The first is the single activity route: you can either pass the latest SecurityX exam (currently priced at $509 [23]) or earn an approved non-CompTIA certification, such as CISSP or CISM [20]. The second option is the multiple activities route, which involves accumulating 75 CEUs through various professional activities. These can include attending webinars, completing training courses, publishing articles, or documenting relevant work experience [19]. At least half of these activities must align with the current exam objectives [22].

CompTIA emphasizes the importance of renewal as part of professional growth:

"Renewing your certification gives you a great opportunity to document your knowledge in technology areas that matter to employers and are important to your IT career." – CompTIA [20]

To make the process easier, use CompTIA’s CEU assessment tool to confirm your activities meet the requirements before committing time to them [22]. Be sure to upload documentation to your certification record while the training courses are still on the pre-approved list. If a course is removed before you upload your proof, those CEUs won’t count [21]. Additionally, you can leverage your day-to-day work in security architecture under the "Work Experience" category to earn CEUs without extra costs [19].

If you fail to renew your certification before it expires, your only option to regain active status is to retake the current exam [20]. Unlike other CompTIA certifications, you can’t renew SecurityX by earning a "higher-level" certification. Your choices are limited to earning CEUs, obtaining a qualifying non-CompTIA certification, or retaking the exam [20][23]. This renewal process helps ensure your skills stay sharp and relevant for advancing your career in cleared security roles.

Conclusion

SecurityX, previously known as CASP+, combines security architecture and engineering expertise in a way that sets it apart [5]. For cleared security architects, it demonstrates your ability to design and implement secure solutions in complex environments while meeting DoD 8140/8570 compliance standards. Unlike management-focused certifications, SecurityX highlights your advanced technical and hands-on skills.

This certification offers real career advantages. Around 32% of certified professionals report pay raises or promotions [8], and the Bureau of Labor Statistics forecasts a 33% growth rate for Information Security Analysts between 2023 and 2033 [8]. Employers like the U.S. Army, U.S. Navy, Booz Allen Hamilton, and General Dynamics actively seek SecurityX-certified individuals for cleared positions [3].

The upcoming rebrand to SecurityX on December 17, 2024, reflects its adaptation to emerging threats. With cloud-focused cyber threats surging by 110% annually and cloud intrusions up 75% [5], the updated exam emphasizes automation, artificial intelligence, and Zero Trust architectures to ensure your skills stay relevant. This shift aligns with the rapidly changing threat landscape and employer demands. Certified professionals should update their records to reflect the new name [5].

Staying certified requires ongoing effort. To maintain your credential, you’ll need 75 CEUs every three years [8]. Regular training, practical work experience, and professional development are crucial to staying competitive and meeting compliance requirements, helping you retain your cleared status and advance your career.

FAQs

Is CASP+ the same as CompTIA SecurityX?

The CASP+ certification has been renamed SecurityX. Tailored for security architects and senior security engineers, this advanced certification focuses on practical expertise in designing and implementing secure solutions. The updated SecurityX version now features more hands-on components and real-world scenarios, ensuring it aligns closely with the demands of advanced cybersecurity roles.

What cleared roles does SecurityX satisfy under DoD 8140/8570?

SecurityX plays key roles such as security architect and security engineer under the DoD 8140/8570 directives. It is officially approved by the Department of Defense (DoD) to meet the requirements outlined in 8140/8570.01-M. The program is acknowledged for its expertise in areas like risk management, enterprise security, and security architecture. These qualifications align perfectly with the directive’s expectations for cybersecurity professionals in advanced, cleared positions.

How should I practice for the performance-based questions?

To get ready for performance-based questions on the CASP+ exam, dedicate time to hands-on practice that mirrors real-world cybersecurity challenges. Work in labs, simulations, or virtual setups to strengthen your skills in areas like enterprise security operations, architecture, and risk management. Focus on scenario-driven resources that highlight practical applications, helping you confidently tackle complex security solutions during the exam.

Related Blog Posts

  • CISSP Cleared Cybersecurity vs CASP+ – The Certification ROI Debate for TS/SCI Holders
  • GSEC Certification Career Guide for Cleared Security Essentials
  • Security Plus Certification Career Guide for Cleared Entry Level
  • CySA Plus Certification Career Guide for Cleared SOC Analysts

Related Guides

  • CAP Certification Career Guide for Cleared Authorization Pros
  • CGRC Certification Career Guide for Cleared GRC Analysts
  • CRISC Certification Career Guide for Cleared Risk Professionals
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

CySA Plus Certification Career Guide for Cleared SOC Analysts

CyberSecJobs Editorial · February 13, 2026 ·

The CySA+ certification is a must-have for cleared SOC analysts aiming to excel in cybersecurity roles. It focuses on skills like behavioral analytics, incident response, and vulnerability management, making it ideal for managing classified systems and meeting DoD 8140/8570 requirements. Here’s a quick overview:

  • Why It Matters: CySA+ supports roles like Cyber Defense Analyst and Incident Responder, with salaries ranging from $91,015 to over $107,090 annually. It also meets mandatory DoD standards for cleared environments.
  • Exam Details: Costs $425, includes up to 85 questions, and requires a score of 750/900 to pass. Key focus areas include Security Operations (33%), Vulnerability Management (30%), Incident Response (20%), and Reporting/Communication (17%).
  • Preparation Tips: Recommended for candidates with 4+ years of SOC experience. Use tools like Wireshark, SIEM platforms, and scripting languages (Python, PowerShell) alongside CompTIA’s CertMaster suite for study resources.
  • Career Benefits: Opens doors to advanced roles like Threat Hunter, SOC Manager, and Detection Engineer. Holding a clearance can significantly boost salaries, with TS/SCI clearances adding $20,000–$30,000 or more annually.

CySA+ certification not only advances your skills but also positions you for leadership roles in high-demand cybersecurity markets.

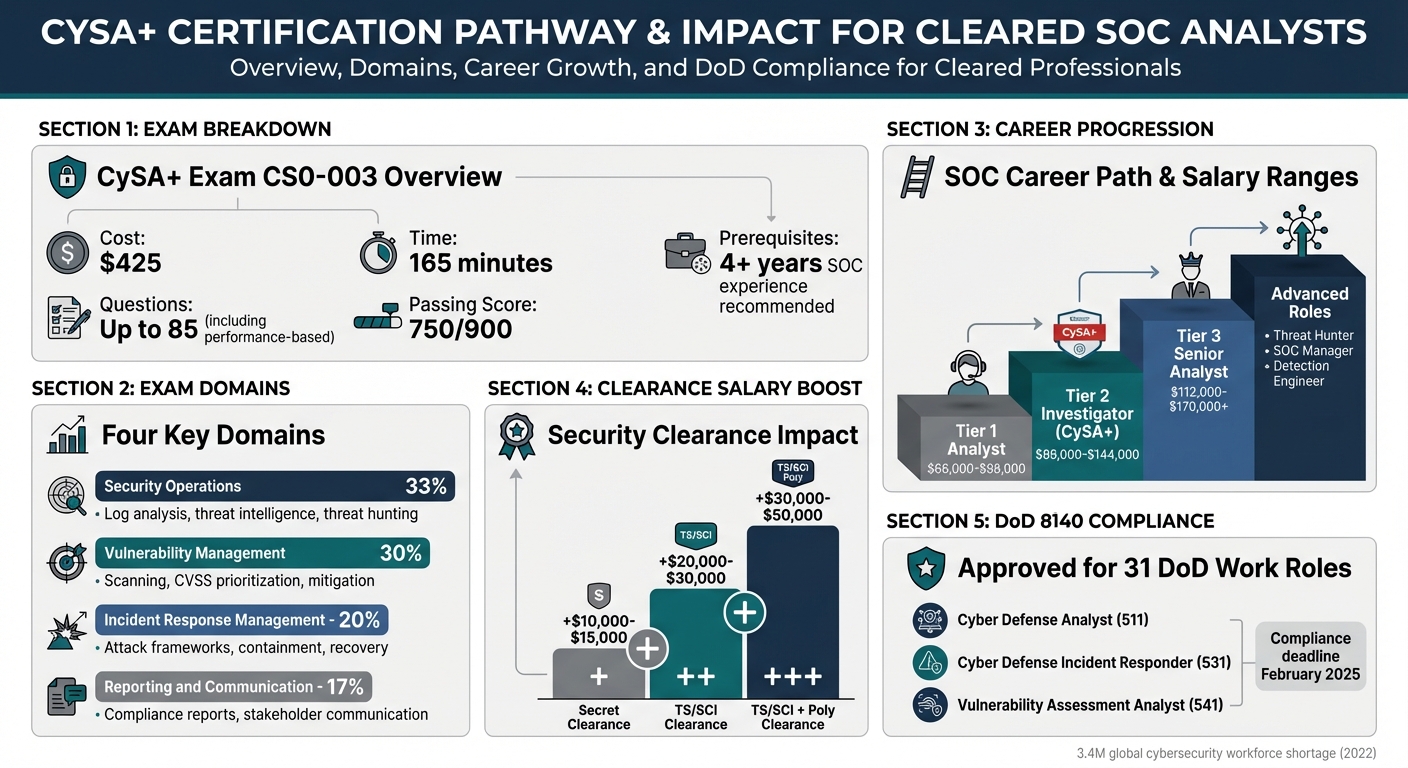
CySA+ Exam Domains and Career Progression for Cleared SOC Analysts

CySA+ Exam Domains and Career Progression for Cleared SOC Analysts

How to Study for the CompTIA CySA+ (and Pass the First Time)

CompTIA

sbb-itb-bf7aa6b

What is the CySA+ Certification?

The CompTIA Cybersecurity Analyst (CySA+) certification demonstrates your ability to identify, manage, and respond to cybersecurity threats through continuous monitoring and behavioral analytics. Unlike entry-level certifications that focus on general security concepts, CySA+ emphasizes detecting unusual activity patterns rather than relying on known threat signatures. This makes it a valuable credential for SOC analysts tasked with identifying sophisticated cyberattacks [6].

As a vendor-neutral certification, CySA+ equips you with skills that apply across various tools and platforms, including Wireshark, SIEM solutions, and scripting languages like Python and PowerShell [4]. The CS0-003 exam consists of up to 85 questions, including performance-based tasks that simulate real-world SOC scenarios. Candidates have 165 minutes to complete the test, and a passing score is 750 out of 900 [5]. This certification is ideal for roles such as SOC analysts, threat intelligence analysts, and incident responders. It is also approved under the DoD 8140/8570.01-M framework for cybersecurity roles. CompTIA recommends having prior certifications like Network+ or Security+, along with at least four years of hands-on experience in SOC operations or incident response [6][2]. These prerequisites ensure candidates are well-prepared for the exam’s focus on practical, real-world challenges.

CySA+ Exam Domains

The CySA+ exam is structured around four key domains that reflect the responsibilities of SOC professionals:

  • Security Operations (33%): Focuses on tasks like analyzing logs, managing threat intelligence, and conducting threat-hunting activities.
  • Vulnerability Management (30%): Tests your ability to perform vulnerability scans, prioritize risks using CVSS scores, and recommend mitigation strategies.
  • Incident Response Management (20%): Covers the entire incident response process, from detection to containment and recovery, while referencing frameworks like MITRE ATT&CK and the Cyber Kill Chain.
  • Reporting and Communication (17%): Highlights the importance of translating technical findings into reports and actionable intelligence, especially in environments dealing with sensitive data.
Domain Weight Key Focus Areas
Security Operations 33% Log analysis, threat intelligence, threat hunting, SIEM/EDR tools, identity management, encryption
Vulnerability Management 30% Scanning, CVSS-based prioritization, mitigation strategies, patch management
Incident Response Management 20% Attack frameworks, containment, recovery, and lifecycle management
Reporting and Communication 17% Compliance reports, stakeholder communication, performance metrics

The latest exam version (CS0-003) has been updated to address emerging trends like Security Orchestration and Automated Response (SOAR), Endpoint Detection and Response (EDR), Extended Detection and Response (XDR), cloud security, mobile threats, and zero trust architecture [2].

Why CySA+ Matters for Cleared SOC Analysts

The CySA+ certification goes beyond technical skills to meet the unique challenges of cleared environments, where professionals often face advanced persistent threats targeting classified systems. By focusing on behavioral analytics, CySA+ enables analysts to detect anomalies that traditional, signature-based tools might miss [3]. This is particularly important when safeguarding systems that manage sensitive government data, where breaches could have serious national security consequences.

The certification also emphasizes protecting sensitive information through encryption and secure architectures while ensuring compliance with regulations like the Federal Information Security Management Act (FISMA) [1]. Additionally, the Reporting and Communication domain equips analysts with the skills to document incidents and share findings without jeopardizing classified information – an essential capability for SOC professionals working in high-security environments.

How to Prepare for the CySA+ Exam

Exam Prerequisites and Recommended Experience

The CySA+ exam doesn’t require any previous certifications, so you can register for it without meeting specific prerequisites. However, CompTIA suggests that candidates have around four years of hands-on experience in roles like SOC analyst, incident response analyst, or something similar. This is because the test focuses heavily on practical, job-related skills rather than just theoretical knowledge.

If you’re working in a cleared government SOC environment, you’re likely already gaining experience in behavioral analytics, intrusion detection, and incident response – all of which align closely with the exam’s objectives. The certification is tied to several DoD 8140 work roles, such as Cyber Defense Analyst, Cyber Defense Incident Responder, and Vulnerability Assessment Analyst. If these responsibilities are part of your day-to-day work, you’re already building a solid base. For those with less SOC experience, it’s important to plan for extra study time to close any knowledge gaps.

Study Resources and Materials

Once you’ve assessed your experience, start preparing by reviewing the official exam objectives. You can download the CS0-003 exam objectives directly from CompTIA’s website to understand what areas to prioritize. CompTIA’s CertMaster suite offers resources tailored for this exam, including:

  • CertMaster Learn: eLearning with videos and flashcards to build foundational knowledge.
  • CertMaster Labs: Virtual environments for hands-on practice.
  • CertMaster Practice: Adaptive tools with timed practice exams to help you prepare under test-like conditions.

If you’re already working in a cleared SOC environment, you can enhance your preparation by practicing with the tools you use daily. For example, set up virtual machines and work with tools like Wireshark, SIEM platforms, VirusTotal, Python, and PowerShell. Open-source tools such as Elastic Stack and threat intelligence feeds can also help reinforce practical skills. Taking full-length, timed practice tests using tools like CertMaster Practice is another great way to simulate the actual test environment.

Creating a Study Plan and Scheduling Your Exam

Once you’ve gathered your study materials, create a study plan that aligns your current SOC tasks with the exam’s four main domains. This approach helps you identify areas that need extra focus. The exam voucher itself costs $425, but you can save money by purchasing bundles that include training materials [4]. Tools like CertMaster Learn’s countdown calendar and personalized progress dashboard can be helpful for staying on track, especially if you’re juggling exam prep with a full-time cleared role.

When you feel ready, buy your exam voucher from the CompTIA Store and schedule your test through Pearson VUE. If you’re in the military and hold a cleared role, check if you qualify to take the exam at an on-base testing center, which can make scheduling and logistics easier.

Using CySA+ Skills in Cleared SOC Roles

Incident Response and Threat Management

In cleared environments, government systems often face advanced threats that can slip past traditional signature-based detection methods. Identifying these threats involves analyzing anomalies across networks, hosts, and applications [7][10]. With CySA+ certification, you’ll be equipped to use tools like Security Information and Event Management (SIEM) systems, Endpoint Detection and Response (EDR), and Extended Detection and Response (XDR) – tools that are staples in most SOCs [7][8].

The certification also teaches you to work with frameworks such as MITRE ATT&CK, the Cyber Kill Chain, and the Diamond Model. These frameworks provide a structured way to manage the incident response lifecycle, from detection and analysis to containment, eradication, and recovery [7][10]. This knowledge helps you better understand the behavior of threat actors and respond effectively.

CySA+ goes beyond incident response by teaching the distinction between threat intelligence and threat hunting. You’ll learn to analyze threat actor tactics, techniques, and procedures (TTPs) to proactively identify advanced threats before they can cause harm [7][8]. Since the certification is approved for multiple DoD 8140 work roles, such as Cyber Defense Incident Responder and Vulnerability Assessment Analyst, the skills you gain directly align with the needs of cleared SOC operations [7][9].

Vulnerability Assessment for Classified Systems

CySA+ also prepares you to manage vulnerabilities in classified systems, where precision is even more critical than in standard IT environments. You’ll learn to use various scanning methods – credentialed, agent-based, and active/passive – to achieve more accurate assessments [7]. For sensitive enclaves, credentialed scans are particularly useful as they minimize false positives and provide a clearer picture of your internal security posture [7].

The certification also covers identifying vulnerabilities in specialized systems often found in cleared environments, such as SCADA, Industrial Control Systems (ICS), and System-on-Chip (SoC) [11][12]. You’ll gain the skills to prioritize remediation using the Common Vulnerability Scoring System (CVSS) while considering factors like asset value and exploitability [7][11]. For systems that can’t be patched immediately due to mission-critical requirements, CySA+ helps you recommend alternative controls to reduce risk [7]. Additionally, you’ll learn to identify where systems deviate from enclave policies, local security guidelines, or federal regulations like FISMA [12][13].

Reporting and Communication with Classified Data

Beyond technical expertise, clear communication is essential in cleared environments. CySA+ dedicates 17% of its exam to reporting and communication, ensuring you can create actionable reports and deliver key performance metrics to both technical and non-technical stakeholders [7][14][15][16]. This skill is invaluable when presenting complex technical data to leadership or collaborating with other agencies [15][16].

"It validates a tech professional’s expertise in incident response and vulnerability management processes, emphasizing the critical communication skills necessary for effective security analysis and compliance." – CompTIA [7]

When working with classified data, maintaining accurate records of security incidents and response actions is not just a best practice – it’s a compliance requirement. These records ensure your organization adheres to industry standards and regulations [15].

Advancing Your Career with CySA+ Certification

SOC Career Progression Paths

CySA+ acts as a stepping stone for advancing from entry-level tasks to more complex responsibilities in a Security Operations Center (SOC). At Tier 1, your focus is on following predefined procedures and triaging alerts. Once you earn your CySA+ certification, you’ll take on more advanced duties, such as developing mitigation strategies, performing root cause analysis, and making critical containment decisions that require professional judgment [18].

This certification can open doors to senior technical roles like Threat Hunter or Detection Engineer, where you’ll create custom detection logic and lead hypothesis-driven investigations. It can also pave the way for leadership roles, such as SOC Manager or Team Lead, where your technical expertise helps shape strategic decisions [18].

The salary growth reflects these advancements. Tier 1 analysts typically earn between $66,000 and $98,000 annually, while Tier 2 investigators with CySA+ certification can see earnings climb to $86,000–$144,000. Senior Tier 3 analysts often earn $112,000–$170,000+ within four to seven years [18]. Security clearance can further boost these figures – holding a Secret clearance could add $10,000–$15,000 to your base salary, while a TS/SCI clearance might increase it by $20,000–$30,000. For roles requiring a TS/SCI with polygraph, compensation may rise by an additional $30,000–$50,000 [18].

To accelerate your career, invest in skills like scripting with Python or PowerShell to automate tasks such as log parsing and alert enrichment – 24% of mid-level Security Operations job listings mention these skills [18]. Additionally, mastering a specific SIEM platform can make you even more competitive. For instance, Splunk is mentioned in 37% of SOC Analyst postings, and Microsoft Sentinel appears in 50% of SIEM Engineer roles [18]. Pairing CySA+ certification with expertise in these tools positions you strongly in the job market, helping you advance to roles that require both technical and analytical expertise.

Meeting DoD 8140 Requirements

DoD 8140

For professionals in cleared roles, CySA+ isn’t just a helpful credential – it’s often mandatory. The certification is approved for 31 specific work roles under the Department of Defense Manual 8140.03 framework, providing more versatility than many entry-level certifications [17]. These roles include Cyber Defense Analyst (511), Cyber Defense Incident Responder (531), and Vulnerability Assessment Analyst (541) [17].

"The DoDM 8140.03 qualification standards focus on a demonstration of capability rather than a compliance-based approach… ensuring that the cyber workforce is competent in performing the required functions of their job role." – CompTIA [17]

By February 2025, all DoD cybersecurity personnel are required to meet these standards [17]. If you’re new to a cleared role, you’ll typically have 180 days from your assignment date to obtain the necessary certification [20][21]. Missing this deadline can result in losing system access, so it’s essential to plan ahead.

Before scheduling your exam, confirm your specific DCWF (Department of Defense Cyber Workforce Framework) work role code with your Information Assurance Manager to ensure CySA+ aligns with your position [17][22]. The certification also meets requirements for Information Assurance Technical (IAT) Level II and various Cyber Security Service Provider (CSSP) roles, giving you flexibility to transition between cleared positions without needing additional certifications [20][21]. This alignment with DoD standards not only secures your current role but also opens up opportunities for growth in cleared cybersecurity positions.

Job Search Tips on Cleared Cyber Security Jobs

Cleared Cyber Security Jobs

Earning your CySA+ certification enhances your technical skills and boosts your profile in the job market. When searching for roles on Cleared Cyber Security Jobs, highlight your CySA+ certification to target positions where it’s explicitly listed as a requirement, such as "Cyber Defense Analyst" or "Systems Security Analyst" [17]. Considering that 96% of HR managers use IT certifications as a filtering criterion during recruitment [19], showcasing your CySA+ credential on your resume can help you pass initial screening processes.

Focus your job search on high-demand areas like Arlington, VA, and Northern Virginia, where salaries for cleared, certified analysts tend to be the highest [18]. Use the platform’s job alert feature to receive notifications for positions that match your CySA+ certification and clearance level. With SOC Analyst ranked as the #1 most in-demand cybersecurity role [18], this is an excellent time to enter the market.

To stand out, go beyond listing your certification. Use GitHub to display scripts that demonstrate your automation skills, or create detailed write-ups of alert triage exercises to showcase your analytical expertise [18]. If you attend job fairs hosted by the platform, be ready to discuss how you’ve applied CySA+ concepts – such as mapping threats using the MITRE ATT&CK framework – in practical scenarios. Combining certification with hands-on experience and a clear demonstration of your skills positions you as a top-tier candidate in the competitive cybersecurity job market.

Conclusion

The CySA+ certification represents an important milestone for cleared SOC analysts aiming to advance their careers in government and defense cybersecurity. With a global shortage of 3.4 million cybersecurity professionals as of 2022 – and around 60% of organizations reporting open cybersecurity roles [23] – this certification equips you to meet growing demand while also satisfying the mandatory DoD 8140 requirements.

Success begins with thorough preparation. To tackle performance-based questions effectively, blend theoretical knowledge with hands-on experience using tools like SIEMs, Wireshark, and scripting languages. Though the $425 exam fee may seem steep, it’s an investment with the potential for significant returns, as certified professionals typically earn between $52,000 and $116,000 annually [9].

This preparation doesn’t just help you pass the exam – it builds practical expertise that’s critical in high-security environments. You’ll be ready to analyze SIEM alerts, evaluate vulnerabilities in classified systems, and handle incident response with precision, all while adhering to strict protocols for sensitive data.

Once certified, CySA+ opens doors to senior roles like Threat Hunter, Detection Engineer, or SOC Manager. When exploring opportunities on Cleared Cyber Security Jobs, highlight your certification prominently. Focus on high-demand areas such as Northern Virginia, where cleared and certified analysts often earn top-tier salaries. Don’t forget to set up job alerts to stay updated on roles that align with your qualifications.

FAQs

Is CySA+ harder than Security+?

Yes, CySA+ is often viewed as more challenging than Security+. While Security+ serves as an entry-level certification covering basic security principles, CySA+ takes things a step further. It’s an intermediate-level certification aimed at analysts, requiring a stronger grasp of topics like threat management, incident response, and security operations. Unlike Security+, CySA+ emphasizes applying foundational knowledge to practical, real-world situations, which many candidates find more demanding.

How long should I study for CySA+ if I work in a cleared SOC?

For SOC professionals with security clearances, getting ready for the CySA+ exam usually requires about 3 months of preparation. Aim to spend 10–15 hours per week studying, though the exact amount may vary based on your prior experience and understanding of cybersecurity concepts. Be flexible with your schedule to ensure you cover all necessary material and feel confident on exam day.

What jobs should I apply for after earning CySA+ with a clearance?

With a CySA+ certification and a security clearance, you’re well-positioned for roles such as SOC Analyst, Vulnerability Analyst, Threat Intelligence Analyst, or Cybersecurity Analyst. These jobs typically involve tasks like monitoring threats, responding to incidents, and managing vulnerabilities.

Your clearance can also open doors to government or defense positions, including roles like Cybersecurity Engineer or Cyber Defense Analyst. These positions often require advanced skills in detecting threats and implementing robust security measures.

Related Blog Posts

  • Top 10 Cyber Security Jobs for Cleared Professionals
  • CISA Certification Career Guide for Cleared IT Auditors
  • GSEC Certification Career Guide for Cleared Security Essentials
  • Security Plus Certification Career Guide for Cleared Entry Level

Related Guides

  • BTL2 Certification Career Guide for Cleared Blue Team Level 2
  • BTL1 Certification Career Guide for Cleared Blue Team Level 1
  • Security Plus Certification Career Guide for Cleared Entry Level
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

Security Plus Certification Career Guide for Cleared Entry Level

CyberSecJobs Editorial · February 11, 2026 ·

Looking to break into cybersecurity with a clearance? The CompTIA Security+ certification is a must-have for entry-level roles in government and defense. It’s recognized under the DoD 8140.03 framework, qualifying you for 31 cybersecurity roles like Security Analyst, SOC Analyst, and Network Security Administrator. With over 82,000 job openings requiring this credential, it’s your gateway to high-demand positions and salaries starting at $45,000 to $70,000 annually.

Here’s what you need to know:

  • Exam Details: 90 questions, 90 minutes, $425 fee, passing score of 750/900.
  • Study Tips: Use video courses (e.g., Professor Messer), hands-on labs, and practice exams to prepare.
  • Clearance Advantage: Security+ certified professionals with clearance earn 25-40% more.

This guide covers everything: preparing for the exam, finding cleared jobs, optimizing your resume, and advancing your career with certifications like CySA+ or CISSP. Whether you’re a veteran or new to IT, Security+ can set you up for success in a growing field.

How to PASS Your Security+ in ONE MONTH | CompTIA Security+ Study Guide For a Complete Beginner

sbb-itb-bf7aa6b

Entry-Level Cybersecurity Roles That Require Security+

Entry-Level Cybersecurity Roles Requiring Security+ Certification: Salaries and Responsibilities

Entry-Level Cybersecurity Roles Requiring Security+ Certification: Salaries and Responsibilities

The Security+ certification is a powerful credential for cleared professionals aiming to make an immediate impact in cybersecurity. It’s required or preferred in over 60% of cleared cybersecurity job listings, with 82,494 current openings, making it the second most sought-after certification after CISSP [3][5][9]. Below are three key entry-level roles where Security+ plays a critical role.

Security Analyst

As a Security Analyst, you’ll be on the frontlines, monitoring network activity, performing vulnerability scans, conducting penetration tests, and applying critical security patches [4][5]. This role involves analyzing reports from security tools to detect unusual behavior and recommending measures to strengthen defenses [4][6]. In cleared environments, you’ll also ensure compliance with NIST frameworks and perform regular audits to meet Department of Defense (DoD) standards.

The average salary for a Security Analyst is about $107,517, with entry-level positions starting between $60,000 and $70,000 annually [4][3]. To excel, you’ll need skills in risk assessment, security frameworks, and tools for vulnerability management.

SOC Analyst

SOC (Security Operations Center) Analysts are the first line of defense in identifying and responding to threats in real time [6]. Working within a SOC, you’ll monitor alerts from tools like Splunk or ELK, perform initial incident triage, investigate suspicious activity, document incidents, and escalate critical threats to senior analysts [4][6]. This role requires constant vigilance to analyze attack patterns and prevent breaches before they escalate.

"Nearly every government job requires Sec+ for InfoSec/IT work. As most of those jobs are general IT work, if you know anything about computers and have Sec+, you can get a federal service job." – Cody Jackson, InfoSec Manager [7]

Starting salaries for Tier 1 SOC Analysts range from $45,000 to $55,000, with experienced analysts earning between $80,000 and $95,000 annually [3][6]. Key skills include log analysis, knowledge of network protocols, and the ability to work rotating shifts to ensure 24/7 security coverage.

Network Security Administrator

Network Security Administrators are responsible for managing and securing network infrastructure in cleared environments [5][8]. This includes configuring and maintaining firewalls, managing user access controls, implementing security policies, and monitoring network traffic for anomalies [4][6]. Hands-on experience with network protocols and security devices is essential for this role.

Network Security Administrators earn an average salary of $91,000, with junior roles in cleared environments offering between $77,500 and $109,500 [5][8][11]. This position is an excellent starting point for advancing into specialized roles like security architecture and involves conducting regular audits to ensure compliance with DoD security standards.

Role Average Starting Salary Key Responsibilities
Security Analyst $60,000 – $70,000 Vulnerability scanning, patching, compliance
SOC Analyst (Tier 1) $45,000 – $55,000 Alert monitoring, incident triage, documentation
Network Security Admin $77,500 – $109,500 Firewall setup, access management, policy enforcement

These roles not only offer attractive salaries but also serve as critical stepping stones in the cybersecurity field. Cleared professionals with Security+ certification tend to earn 25% to 40% more than their non-cleared counterparts. Additionally, government roles typically offer a 15% to 20% salary premium over private sector positions [10]. For veterans with security clearances, pairing their clearable status with Security+ certification can give them a significant edge in securing federal contracting jobs [2].

How to Get Your Security+ Certification

Earning your Security+ certification might be simpler than you think. There are no formal prerequisites – no degree or prior certifications are required to register for the exam. That said, CompTIA suggests having a Network+ certification and roughly two years of IT administration experience with a focus on security before attempting Security+ [16][17][20]. If you’re transitioning from the military or switching careers, don’t let this hold you back. Many professionals pass the exam with dedicated study and practical experience. Proper preparation not only helps you pass but also ensures you’re ready for cybersecurity roles requiring clearance. Now, let’s dive into the exam structure, study tools, and the registration process.

Exam Domains and Topics

The current Security+ exam (SY0-701) includes up to 90 questions – both multiple-choice and performance-based – and you’ll have 90 minutes to complete it. A passing score is 750 out of 900 [1][12]. The exam is divided into five key domains:

  • Security Operations (28%): Covers areas like incident response, asset management, and vulnerability management.
  • Threats, Vulnerabilities, and Mitigations (22%): Focuses on threat actors, attack techniques, malware, and social engineering.
  • Security Program Management and Oversight (20%): Includes governance, risk management, and compliance with frameworks like HIPAA and GDPR.
  • Security Architecture (18%): Addresses cloud models, IoT security, data protection, and system resilience.
  • General Security Concepts (12%): Covers the CIA triad, Zero Trust principles, and cryptography basics [1][13].

Performance-based questions (PBQs) are especially critical. These simulate tasks like configuring firewalls or setting up access controls, which mirror real-world scenarios in cybersecurity roles.

Study Resources and Materials

A solid "study stack" is key to passing on your first attempt. Start with video courses – Professor Messer offers free resources on YouTube, while Jason Dion’s Udemy courses are great for quick learning [14][12]. Pair these with books like Mike Meyers’ All-in-One guide or Darril Gibson’s Get Certified Get Ahead for in-depth technical insights [13][12].

"Without labs, most students forget half of what they read when preparing. If you configure a firewall rule yourself, you’ll remember it ten times longer." – Professor, Programs.com [12]

Hands-on labs are a must. CompTIA CertMaster Labs provides structured exercises, or you can create your own virtual lab using VirtualBox or VMware. Practice tasks like configuring firewalls, setting up access control lists, and running vulnerability scans [15][12]. Finally, test your readiness with practice exams from CertMaster Practice, Boson ExSim-Max, or Professor Messer. Aim to score consistently between 80% and 90% on practice tests before scheduling your exam [13].

Flashcards can also help with memorizing port numbers and acronyms. During practice exams, flag challenging questions and revisit them later – this strategy works well on the actual test since there’s no penalty for incorrect answers [13].

Prerequisites and Exam Registration

When you’re ready, log in to your CompTIA account and click "Schedule and Manage Exams" to register through Pearson VUE [18]. Choose the SY0-701 exam and decide whether to test online via OnVUE or at a Pearson VUE testing center [16][18][20]. Select your preferred date, time, and language, then complete payment or apply a voucher code at checkout [18].

The exam voucher costs $425, or $474 with a retake option. Overall, costs can range from $600–$800 for self-study materials to as much as $3,500 for bootcamps [12][13]. Active-duty military personnel might qualify for up to $2,000 in certification training funds through Army COOL or AF COOL programs [19].

Pro Tip: Ensure the name on your CompTIA account matches your government-issued ID exactly, or you could be turned away at the testing center [18]. If testing online, run a system compatibility check ahead of time to avoid technical issues with the OnVUE software [16]. You can reschedule your exam up to 24 hours before your appointment without penalty [13].

The Security+ certification is valid for three years. To renew, you can earn 50 Continuing Education Units (CEUs) or pass a higher-level exam like CySA+ or CASP+ [16][19]. For those in cleared roles, Security+ satisfies DoD 8140/8570 compliance requirements for IAT Level II positions, making it a critical credential for government and contractor jobs [19][13].

Using Security+ to Find Cleared Jobs

If you’ve earned your Security+ certification, you’re already on the right path to landing a cleared job. But certification alone isn’t enough – you need to know how to search effectively, present your credentials, and stay visible to employers. Platforms like Cleared Cyber Security Jobs are tailored for this purpose, connecting security-cleared professionals with direct-hire employers in defense and intelligence. Unlike general job boards, every position here requires U.S. citizenship and an active security clearance, ensuring you see only relevant opportunities. Below, we’ll cover how to refine your job search, craft an optimized resume, and take advantage of job alerts and events.

How to Filter Jobs on Cleared Cyber Security Jobs

Cleared Cyber Security Jobs

Start by using search filters to zero in on roles that fit your qualifications. Enter "Security+" or "CompTIA Security+" as keywords to find positions where this certification is explicitly required or preferred. Then, narrow your results by clearance level – whether it’s Secret, Top Secret, or TS/SCI. You can also filter by location, job type (full-time, part-time, contract), and experience level to target entry-level positions like Security Analyst, SOC Analyst, or Network Security Administrator.

Pay close attention to job descriptions mentioning IAT Level II or IAM Level I compliance. These categories align with Security+ certification and are essential for meeting federal requirements. Matching your qualifications to these standards is key to positioning yourself as a strong candidate.

How to Write Your Resume for Cleared Roles

Your resume should make two things immediately clear: you’re Security+ certified, and you hold a security clearance. Highlight these in your header or professional summary. For example: "Security+ certified professional with an active Secret clearance and two years of IT support experience." This ensures recruiters and Applicant Tracking Systems (ATS) can quickly identify your qualifications.

Include a dedicated "Certifications" or "Technical Skills" section to list CompTIA Security+ and other relevant credentials. Clearly state your clearance status, such as "Active Secret" or "Active TS/SCI." If your clearance is inactive but still within the 24-month reinstatement window, note it as "Inactive, Eligible for Reinstatement." Avoid mentioning sensitive details like classified project names, clearance ID numbers, or investigation dates.

When detailing your work experience, focus on measurable achievements. Instead of saying, "Supported cybersecurity operations", use specifics like: "Reduced system vulnerabilities by 35% through proactive monitoring and patch management." Use action verbs and numbers to demonstrate your impact, and align your language with the technical skills and DoD 8140 requirements listed in job postings.

"I currently hold an active Secret clearance, which enables me to support secure, mission-critical projects from day one." – MyPerfectResume [22]

Setting Up Job Alerts and Attending Job Fairs

Streamline your job search by setting up automated alerts. Save your search criteria – such as "Security+" and your clearance level – to receive email updates when new positions are posted. Completing your candidate profile with details about your clearance, certification, and skills can also make you more visible to recruiters.

Don’t overlook the value of cleared job fairs. These events connect you directly with defense and intelligence employers. For example, upcoming 2026 events include:

  • CI or FS Poly Cleared Job Fair: March 5, 2026, at the Hyatt Regency in Herndon, VA (2:00 PM – 5:30 PM)
  • All Clearances Cleared Job Fair: April 16, 2026, at the Westin in Falls Church, VA (2:00 PM – 5:00 PM)
  • Additional events: May 14, 2026, in Hanover, MD, and June 3, 2026, in Herndon, VA [21].

When attending, bring multiple copies of your resume, dress professionally, and be ready to explain how your certification and clearance align with employer needs. For veterans, these fairs can be especially helpful in transitioning to civilian roles.

"I recently transitioned out of the military and started attending Cleared Job Fairs… I was offered a position shortly after. I accepted and moved directly from the military into my current position, without a lapse in employment." – G.B., Technical Project Manager, CACI [23]

Career Growth After Security+ Certification

Earning your Security+ certification is just the beginning. It lays the groundwork for a career in cybersecurity, and after 3–5 years in cleared roles, you can transition into mid-level positions with more responsibility and higher pay. With cybersecurity roles expected to grow by 32% through 2033 [10], knowing which paths to take and how to enhance your qualifications is critical. Here’s how you can build on your entry-level experience and move forward.

Moving to Mid-Level Positions

Once you’ve gained experience in roles like Security Analyst or SOC Analyst, you can step into mid-level positions such as Incident Response Specialist, Vulnerability Analyst, or Forensics Specialist. These roles focus on tasks like risk assessment, advanced threat hunting, and creating security policies. For cleared professionals, many of these positions align with DoD 8140 requirements, where Security+ is the baseline certification for IAT Level II roles [10][24].

In the defense contracting world, mid-level roles for Security+ certified professionals often offer salaries ranging from $85,000 to $110,000 [10]. For instance, Information Security Analysts typically earn between $65,000 and $80,000 [9], with job growth in this field projected at 33% from 2023 to 2033 [11]. Security Engineers, who focus on designing and safeguarding network architecture, can earn around $150,000 [11][24]. To stand out for these roles, it’s essential to develop skills in scripting languages like Python or PowerShell and gain expertise with SIEM platforms such as Splunk or Sentinel.

Adding More Certifications

Expanding your certification portfolio is a smart way to accelerate your career. Within a year or two of earning Security+, consider pursuing certifications like CompTIA CySA+ if you’re interested in threat detection and behavioral analytics, or CompTIA PenTest+ for a focus on offensive security and vulnerability assessment [10][11].

After reaching five years of experience, aim for the CISSP (Certified Information Systems Security Professional), which is widely regarded as the top credential for senior-level roles. CISSP-certified professionals earn an average salary of $126,000 [24]. If you don’t yet meet the experience requirement, passing the exam to become an Associate of (ISC)² can still boost your profile with cleared recruiters. For those who prefer technical roles over management, CompTIA SecurityX (formerly CASP+) validates advanced skills in security architecture and engineering [10][11].

Cloud certifications are becoming increasingly important, with 94% of organizations now relying on cloud services [10]. Certifications like AWS Certified Security – Specialty (around $300) and Microsoft Azure Security Engineer (AZ-500) (around $165) are particularly valuable for cleared professionals working in government-related cloud security roles [25][26].

Specializations and Growing Fields

Specializing in areas like cloud security, threat intelligence, and incident response can open doors to some of the fastest-growing roles in cybersecurity. For example, threat hunting is expected to grow by 105%, while threat intelligence roles are projected to increase by 53% over the next five years [27]. While Security+ offers a strong foundation by covering hybrid environments such as cloud, IoT, and operational technology (OT), advancing in these fields requires platform-specific expertise.

To specialize in cloud security, focus on mastering tools like AWS IAM, VPC security, and GuardDuty, or Azure Sentinel and Azure AD. For roles in threat intelligence and incident response, certifications like CySA+ are invaluable. Additionally, building a home lab using virtual environments like VMware or VirtualBox – along with tools like Splunk, Microsoft Sentinel, and Nessus – can provide hands-on experience that employers value [10].

Cleared professionals should also consider structured government roles, such as GS-11/12 or GS-13/14 Information Security Specialist positions. These roles offer salaries ranging from approximately $55,000 to over $125,000, depending on location [10]. To stay competitive, plan to invest $3,000 to $8,000 annually in advanced certifications and industry conferences like Black Hat or RSA [10].

Conclusion

The Security+ certification is a gateway to cybersecurity roles that require security clearance. It meets the DoD Directive 8140 requirements for IAT Level II positions, which are common for entry-level jobs in defense contracting and federal agencies. With over 82,494 job listings specifically calling for Security+ certification[9], this credential opens doors to competitive salaries in a field that’s growing rapidly.

If you already have a security clearance, Security+ may be the last piece you need to qualify for these roles. Security-cleared professionals with this certification earn 25–40% more than those without clearance, and many contractors offer clearance bonuses ranging from $5,000 to $15,000 on top of base pay[10]. The exam itself costs $392[9], and you can prepare effectively using tools like CertMaster Learn and hands-on practice labs.

Once certified, update your resume to emphasize both your Security+ credential and your clearance level. Platforms like Cleared Cyber Security Jobs allow you to filter for roles requiring Security+ and set up alerts for positions like SOC Analyst, Security Administrator, or Junior InfoSec Specialist.

Keep in mind, the Security+ certification is valid for three years and requires 50 Continuing Education Units (CEUs) for renewal. Consider planning your next steps early – whether that’s CySA+ for defensive roles, PenTest+ for offensive positions, or CISSP for senior-level opportunities. With cybersecurity jobs expected to grow by 32% through 2033[10], certified professionals with security clearance will remain in high demand.

Start preparing today to secure your spot in this fast-growing and essential field. Taking this step ensures you’re ready to meet the challenges of a dynamic cybersecurity landscape.

FAQs

What clearance level is typically required for Security+ jobs?

Security+ roles frequently demand a Secret or Top Secret security clearance, especially when working with government contractors or in positions connected to national security. These clearances are crucial for handling classified information and fulfilling the responsibilities required in such high-security environments.

How long should I study for Security+ if I’m new to IT?

If you’re just starting out in IT, aim to dedicate 12 to 16 weeks – or around 200 to 300 hours – to your studies. The exact time will depend on your learning speed and prior knowledge. The key is to create a steady, consistent study routine that helps you absorb the material effectively and build a solid base for the exam.

How do I list my clearance on a resume safely?

When including your security clearance on a resume, it’s important to do so carefully and professionally. Mention the clearance level (e.g., Confidential, Secret, or Top Secret), the issuing agency (like the Department of Defense), and the date of issuance or investigation. This information is best placed near the top of your resume, either after your contact details or in your professional summary. Be mindful not to disclose any sensitive or classified details – this ensures you maintain confidentiality while effectively highlighting your qualifications.

Related Blog Posts

  • CIO-SP3 Cybersecurity Positions vs DISA Encore III – Which Vehicle Drives Your Career?
  • Cleared Resume OPSEC Guidelines – What NSA Says You Can and Can’t Say
  • Cleared Cybersecurity Career Assessment – Your Success Scorecard and Action Plan
  • GSEC Certification Career Guide for Cleared Security Essentials


Related Guides

  • BTL2 Certification Career Guide for Cleared Blue Team Level 2
  • BTL1 Certification Career Guide for Cleared Blue Team Level 1
  • CySA Plus Certification Career Guide for Cleared SOC Analysts
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers
  • « Go to Previous Page
  • Go to page 1
  • Interim pages omitted …
  • Go to page 45
  • Go to page 46
  • Go to page 47
  • Go to page 48
  • Go to page 49
  • Interim pages omitted …
  • Go to page 68
  • Go to Next Page »
  • Facebook
  • Instagram
  • LinkedIn
  • Twitter
  • YouTube

Cleared Cyber Security Jobs | CyberSecJobs.com

  • Contact
  • About
  • Privacy Policy