• Skip to primary navigation
  • Skip to main content
Cleared Cyber Security Jobs | CyberSecJobs.com

Cleared Cyber Security Jobs | CyberSecJobs.com

Cleared Cyber Security Jobs

  • Home
  • Search Cleared Cyber Jobs
  • Job Fairs
  • Career Resources

Certifications

CySA Plus Certification Career Guide for Cleared SOC Analysts

CyberSecJobs Editorial · February 13, 2026 ·

The CySA+ certification is a must-have for cleared SOC analysts aiming to excel in cybersecurity roles. It focuses on skills like behavioral analytics, incident response, and vulnerability management, making it ideal for managing classified systems and meeting DoD 8140/8570 requirements. Here’s a quick overview:

  • Why It Matters: CySA+ supports roles like Cyber Defense Analyst and Incident Responder, with salaries ranging from $91,015 to over $107,090 annually. It also meets mandatory DoD standards for cleared environments.
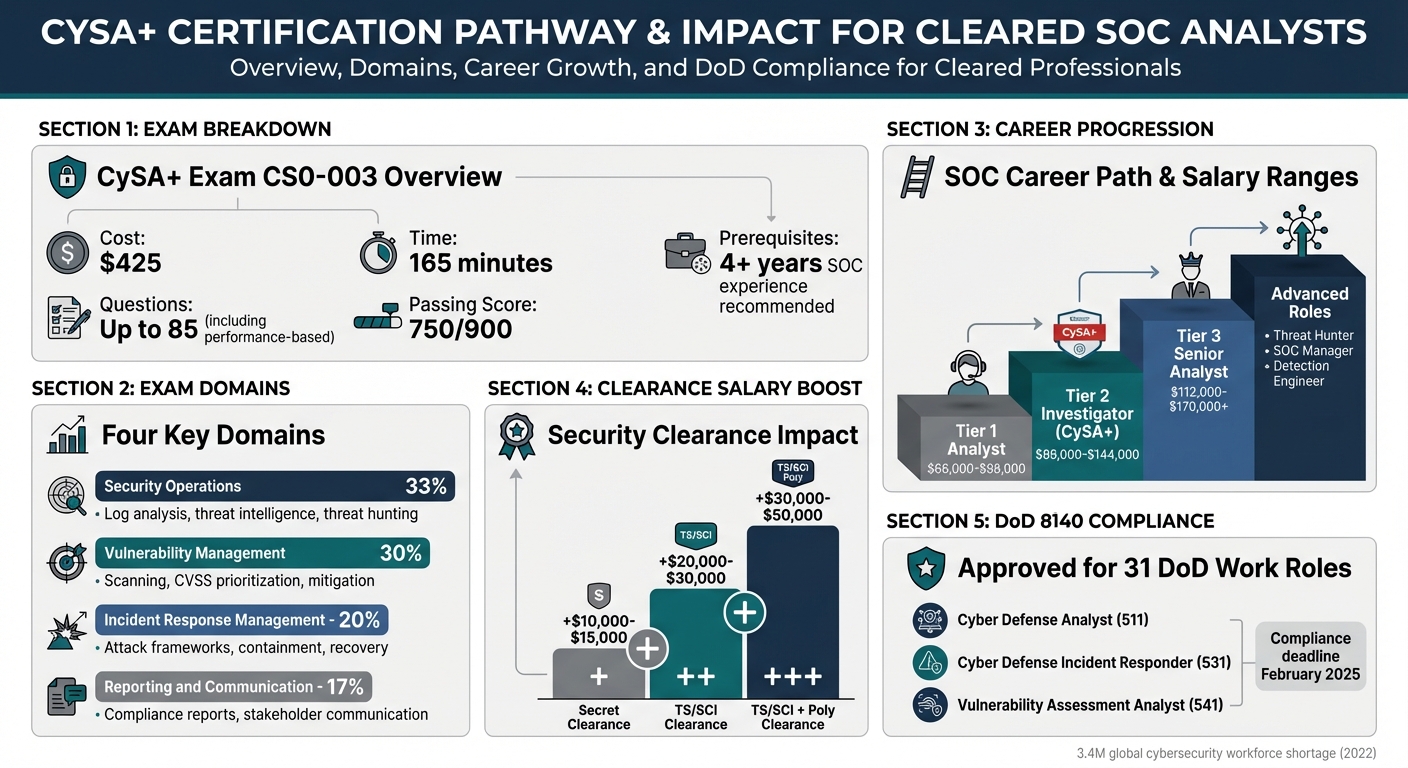
  • Exam Details: Costs $425, includes up to 85 questions, and requires a score of 750/900 to pass. Key focus areas include Security Operations (33%), Vulnerability Management (30%), Incident Response (20%), and Reporting/Communication (17%).
  • Preparation Tips: Recommended for candidates with 4+ years of SOC experience. Use tools like Wireshark, SIEM platforms, and scripting languages (Python, PowerShell) alongside CompTIA’s CertMaster suite for study resources.
  • Career Benefits: Opens doors to advanced roles like Threat Hunter, SOC Manager, and Detection Engineer. Holding a clearance can significantly boost salaries, with TS/SCI clearances adding $20,000–$30,000 or more annually.

CySA+ certification not only advances your skills but also positions you for leadership roles in high-demand cybersecurity markets.
CySA+ Exam Domains and Career Progression for Cleared SOC Analysts

CySA+ Exam Domains and Career Progression for Cleared SOC Analysts

How to Study for the CompTIA CySA+ (and Pass the First Time)
CompTIA

sbb-itb-bf7aa6b

What is the CySA+ Certification?

The CompTIA Cybersecurity Analyst (CySA+) certification demonstrates your ability to identify, manage, and respond to cybersecurity threats through continuous monitoring and behavioral analytics. Unlike entry-level certifications that focus on general security concepts, CySA+ emphasizes detecting unusual activity patterns rather than relying on known threat signatures. This makes it a valuable credential for SOC analysts tasked with identifying sophisticated cyberattacks [6].

As a vendor-neutral certification, CySA+ equips you with skills that apply across various tools and platforms, including Wireshark, SIEM solutions, and scripting languages like Python and PowerShell [4]. The CS0-003 exam consists of up to 85 questions, including performance-based tasks that simulate real-world SOC scenarios. Candidates have 165 minutes to complete the test, and a passing score is 750 out of 900 [5]. This certification is ideal for roles such as SOC analysts, threat intelligence analysts, and incident responders. It is also approved under the DoD 8140/8570.01-M framework for cybersecurity roles. CompTIA recommends having prior certifications like Network+ or Security+, along with at least four years of hands-on experience in SOC operations or incident response [6][2]. These prerequisites ensure candidates are well-prepared for the exam’s focus on practical, real-world challenges.

CySA+ Exam Domains

The CySA+ exam is structured around four key domains that reflect the responsibilities of SOC professionals:

  • Security Operations (33%): Focuses on tasks like analyzing logs, managing threat intelligence, and conducting threat-hunting activities.
  • Vulnerability Management (30%): Tests your ability to perform vulnerability scans, prioritize risks using CVSS scores, and recommend mitigation strategies.
  • Incident Response Management (20%): Covers the entire incident response process, from detection to containment and recovery, while referencing frameworks like MITRE ATT&CK and the Cyber Kill Chain.
  • Reporting and Communication (17%): Highlights the importance of translating technical findings into reports and actionable intelligence, especially in environments dealing with sensitive data.
Domain Weight Key Focus Areas
Security Operations 33% Log analysis, threat intelligence, threat hunting, SIEM/EDR tools, identity management, encryption
Vulnerability Management 30% Scanning, CVSS-based prioritization, mitigation strategies, patch management
Incident Response Management 20% Attack frameworks, containment, recovery, and lifecycle management
Reporting and Communication 17% Compliance reports, stakeholder communication, performance metrics

The latest exam version (CS0-003) has been updated to address emerging trends like Security Orchestration and Automated Response (SOAR), Endpoint Detection and Response (EDR), Extended Detection and Response (XDR), cloud security, mobile threats, and zero trust architecture [2].

Why CySA+ Matters for Cleared SOC Analysts

The CySA+ certification goes beyond technical skills to meet the unique challenges of cleared environments, where professionals often face advanced persistent threats targeting classified systems. By focusing on behavioral analytics, CySA+ enables analysts to detect anomalies that traditional, signature-based tools might miss [3]. This is particularly important when safeguarding systems that manage sensitive government data, where breaches could have serious national security consequences.

The certification also emphasizes protecting sensitive information through encryption and secure architectures while ensuring compliance with regulations like the Federal Information Security Management Act (FISMA) [1]. Additionally, the Reporting and Communication domain equips analysts with the skills to document incidents and share findings without jeopardizing classified information – an essential capability for SOC professionals working in high-security environments.

How to Prepare for the CySA+ Exam

Exam Prerequisites and Recommended Experience

The CySA+ exam doesn’t require any previous certifications, so you can register for it without meeting specific prerequisites. However, CompTIA suggests that candidates have around four years of hands-on experience in roles like SOC analyst, incident response analyst, or something similar. This is because the test focuses heavily on practical, job-related skills rather than just theoretical knowledge.

If you’re working in a cleared government SOC environment, you’re likely already gaining experience in behavioral analytics, intrusion detection, and incident response – all of which align closely with the exam’s objectives. The certification is tied to several DoD 8140 work roles, such as Cyber Defense Analyst, Cyber Defense Incident Responder, and Vulnerability Assessment Analyst. If these responsibilities are part of your day-to-day work, you’re already building a solid base. For those with less SOC experience, it’s important to plan for extra study time to close any knowledge gaps.

Study Resources and Materials

Once you’ve assessed your experience, start preparing by reviewing the official exam objectives. You can download the CS0-003 exam objectives directly from CompTIA’s website to understand what areas to prioritize. CompTIA’s CertMaster suite offers resources tailored for this exam, including:

  • CertMaster Learn: eLearning with videos and flashcards to build foundational knowledge.
  • CertMaster Labs: Virtual environments for hands-on practice.
  • CertMaster Practice: Adaptive tools with timed practice exams to help you prepare under test-like conditions.

If you’re already working in a cleared SOC environment, you can enhance your preparation by practicing with the tools you use daily. For example, set up virtual machines and work with tools like Wireshark, SIEM platforms, VirusTotal, Python, and PowerShell. Open-source tools such as Elastic Stack and threat intelligence feeds can also help reinforce practical skills. Taking full-length, timed practice tests using tools like CertMaster Practice is another great way to simulate the actual test environment.

Creating a Study Plan and Scheduling Your Exam

Once you’ve gathered your study materials, create a study plan that aligns your current SOC tasks with the exam’s four main domains. This approach helps you identify areas that need extra focus. The exam voucher itself costs $425, but you can save money by purchasing bundles that include training materials [4]. Tools like CertMaster Learn’s countdown calendar and personalized progress dashboard can be helpful for staying on track, especially if you’re juggling exam prep with a full-time cleared role.

When you feel ready, buy your exam voucher from the CompTIA Store and schedule your test through Pearson VUE. If you’re in the military and hold a cleared role, check if you qualify to take the exam at an on-base testing center, which can make scheduling and logistics easier.

Using CySA+ Skills in Cleared SOC Roles

Incident Response and Threat Management

In cleared environments, government systems often face advanced threats that can slip past traditional signature-based detection methods. Identifying these threats involves analyzing anomalies across networks, hosts, and applications [7][10]. With CySA+ certification, you’ll be equipped to use tools like Security Information and Event Management (SIEM) systems, Endpoint Detection and Response (EDR), and Extended Detection and Response (XDR) – tools that are staples in most SOCs [7][8].

The certification also teaches you to work with frameworks such as MITRE ATT&CK, the Cyber Kill Chain, and the Diamond Model. These frameworks provide a structured way to manage the incident response lifecycle, from detection and analysis to containment, eradication, and recovery [7][10]. This knowledge helps you better understand the behavior of threat actors and respond effectively.

CySA+ goes beyond incident response by teaching the distinction between threat intelligence and threat hunting. You’ll learn to analyze threat actor tactics, techniques, and procedures (TTPs) to proactively identify advanced threats before they can cause harm [7][8]. Since the certification is approved for multiple DoD 8140 work roles, such as Cyber Defense Incident Responder and Vulnerability Assessment Analyst, the skills you gain directly align with the needs of cleared SOC operations [7][9].

Vulnerability Assessment for Classified Systems

CySA+ also prepares you to manage vulnerabilities in classified systems, where precision is even more critical than in standard IT environments. You’ll learn to use various scanning methods – credentialed, agent-based, and active/passive – to achieve more accurate assessments [7]. For sensitive enclaves, credentialed scans are particularly useful as they minimize false positives and provide a clearer picture of your internal security posture [7].

The certification also covers identifying vulnerabilities in specialized systems often found in cleared environments, such as SCADA, Industrial Control Systems (ICS), and System-on-Chip (SoC) [11][12]. You’ll gain the skills to prioritize remediation using the Common Vulnerability Scoring System (CVSS) while considering factors like asset value and exploitability [7][11]. For systems that can’t be patched immediately due to mission-critical requirements, CySA+ helps you recommend alternative controls to reduce risk [7]. Additionally, you’ll learn to identify where systems deviate from enclave policies, local security guidelines, or federal regulations like FISMA [12][13].

Reporting and Communication with Classified Data

Beyond technical expertise, clear communication is essential in cleared environments. CySA+ dedicates 17% of its exam to reporting and communication, ensuring you can create actionable reports and deliver key performance metrics to both technical and non-technical stakeholders [7][14][15][16]. This skill is invaluable when presenting complex technical data to leadership or collaborating with other agencies [15][16].

"It validates a tech professional’s expertise in incident response and vulnerability management processes, emphasizing the critical communication skills necessary for effective security analysis and compliance." – CompTIA [7]

When working with classified data, maintaining accurate records of security incidents and response actions is not just a best practice – it’s a compliance requirement. These records ensure your organization adheres to industry standards and regulations [15].

Advancing Your Career with CySA+ Certification

SOC Career Progression Paths

CySA+ acts as a stepping stone for advancing from entry-level tasks to more complex responsibilities in a Security Operations Center (SOC). At Tier 1, your focus is on following predefined procedures and triaging alerts. Once you earn your CySA+ certification, you’ll take on more advanced duties, such as developing mitigation strategies, performing root cause analysis, and making critical containment decisions that require professional judgment [18].

This certification can open doors to senior technical roles like Threat Hunter or Detection Engineer, where you’ll create custom detection logic and lead hypothesis-driven investigations. It can also pave the way for leadership roles, such as SOC Manager or Team Lead, where your technical expertise helps shape strategic decisions [18].

The salary growth reflects these advancements. Tier 1 analysts typically earn between $66,000 and $98,000 annually, while Tier 2 investigators with CySA+ certification can see earnings climb to $86,000–$144,000. Senior Tier 3 analysts often earn $112,000–$170,000+ within four to seven years [18]. Security clearance can further boost these figures – holding a Secret clearance could add $10,000–$15,000 to your base salary, while a TS/SCI clearance might increase it by $20,000–$30,000. For roles requiring a TS/SCI with polygraph, compensation may rise by an additional $30,000–$50,000 [18].

To accelerate your career, invest in skills like scripting with Python or PowerShell to automate tasks such as log parsing and alert enrichment – 24% of mid-level Security Operations job listings mention these skills [18]. Additionally, mastering a specific SIEM platform can make you even more competitive. For instance, Splunk is mentioned in 37% of SOC Analyst postings, and Microsoft Sentinel appears in 50% of SIEM Engineer roles [18]. Pairing CySA+ certification with expertise in these tools positions you strongly in the job market, helping you advance to roles that require both technical and analytical expertise.

Meeting DoD 8140 Requirements
DoD 8140

For professionals in cleared roles, CySA+ isn’t just a helpful credential – it’s often mandatory. The certification is approved for 31 specific work roles under the Department of Defense Manual 8140.03 framework, providing more versatility than many entry-level certifications [17]. These roles include Cyber Defense Analyst (511), Cyber Defense Incident Responder (531), and Vulnerability Assessment Analyst (541) [17].

"The DoDM 8140.03 qualification standards focus on a demonstration of capability rather than a compliance-based approach… ensuring that the cyber workforce is competent in performing the required functions of their job role." – CompTIA [17]

By February 2025, all DoD cybersecurity personnel are required to meet these standards [17]. If you’re new to a cleared role, you’ll typically have 180 days from your assignment date to obtain the necessary certification [20][21]. Missing this deadline can result in losing system access, so it’s essential to plan ahead.

Before scheduling your exam, confirm your specific DCWF (Department of Defense Cyber Workforce Framework) work role code with your Information Assurance Manager to ensure CySA+ aligns with your position [17][22]. The certification also meets requirements for Information Assurance Technical (IAT) Level II and various Cyber Security Service Provider (CSSP) roles, giving you flexibility to transition between cleared positions without needing additional certifications [20][21]. This alignment with DoD standards not only secures your current role but also opens up opportunities for growth in cleared cybersecurity positions.

Job Search Tips on Cleared Cyber Security Jobs
Cleared Cyber Security Jobs

Earning your CySA+ certification enhances your technical skills and boosts your profile in the job market. When searching for roles on Cleared Cyber Security Jobs, highlight your CySA+ certification to target positions where it’s explicitly listed as a requirement, such as "Cyber Defense Analyst" or "Systems Security Analyst" [17]. Considering that 96% of HR managers use IT certifications as a filtering criterion during recruitment [19], showcasing your CySA+ credential on your resume can help you pass initial screening processes.

Focus your job search on high-demand areas like Arlington, VA, and Northern Virginia, where salaries for cleared, certified analysts tend to be the highest [18]. Use the platform’s job alert feature to receive notifications for positions that match your CySA+ certification and clearance level. With SOC Analyst ranked as the #1 most in-demand cybersecurity role [18], this is an excellent time to enter the market.

To stand out, go beyond listing your certification. Use GitHub to display scripts that demonstrate your automation skills, or create detailed write-ups of alert triage exercises to showcase your analytical expertise [18]. If you attend job fairs hosted by the platform, be ready to discuss how you’ve applied CySA+ concepts – such as mapping threats using the MITRE ATT&CK framework – in practical scenarios. Combining certification with hands-on experience and a clear demonstration of your skills positions you as a top-tier candidate in the competitive cybersecurity job market.

Conclusion

The CySA+ certification represents an important milestone for cleared SOC analysts aiming to advance their careers in government and defense cybersecurity. With a global shortage of 3.4 million cybersecurity professionals as of 2022 – and around 60% of organizations reporting open cybersecurity roles [23] – this certification equips you to meet growing demand while also satisfying the mandatory DoD 8140 requirements.

Success begins with thorough preparation. To tackle performance-based questions effectively, blend theoretical knowledge with hands-on experience using tools like SIEMs, Wireshark, and scripting languages. Though the $425 exam fee may seem steep, it’s an investment with the potential for significant returns, as certified professionals typically earn between $52,000 and $116,000 annually [9].

This preparation doesn’t just help you pass the exam – it builds practical expertise that’s critical in high-security environments. You’ll be ready to analyze SIEM alerts, evaluate vulnerabilities in classified systems, and handle incident response with precision, all while adhering to strict protocols for sensitive data.

Once certified, CySA+ opens doors to senior roles like Threat Hunter, Detection Engineer, or SOC Manager. When exploring opportunities on Cleared Cyber Security Jobs, highlight your certification prominently. Focus on high-demand areas such as Northern Virginia, where cleared and certified analysts often earn top-tier salaries. Don’t forget to set up job alerts to stay updated on roles that align with your qualifications.

FAQs

Is CySA+ harder than Security+?

Yes, CySA+ is often viewed as more challenging than Security+. While Security+ serves as an entry-level certification covering basic security principles, CySA+ takes things a step further. It’s an intermediate-level certification aimed at analysts, requiring a stronger grasp of topics like threat management, incident response, and security operations. Unlike Security+, CySA+ emphasizes applying foundational knowledge to practical, real-world situations, which many candidates find more demanding.

How long should I study for CySA+ if I work in a cleared SOC?

For SOC professionals with security clearances, getting ready for the CySA+ exam usually requires about 3 months of preparation. Aim to spend 10–15 hours per week studying, though the exact amount may vary based on your prior experience and understanding of cybersecurity concepts. Be flexible with your schedule to ensure you cover all necessary material and feel confident on exam day.

What jobs should I apply for after earning CySA+ with a clearance?

With a CySA+ certification and a security clearance, you’re well-positioned for roles such as SOC Analyst, Vulnerability Analyst, Threat Intelligence Analyst, or Cybersecurity Analyst. These jobs typically involve tasks like monitoring threats, responding to incidents, and managing vulnerabilities.

Your clearance can also open doors to government or defense positions, including roles like Cybersecurity Engineer or Cyber Defense Analyst. These positions often require advanced skills in detecting threats and implementing robust security measures.
Related Blog Posts

  • Top 10 Cyber Security Jobs for Cleared Professionals
  • CISA Certification Career Guide for Cleared IT Auditors
  • GSEC Certification Career Guide for Cleared Security Essentials
  • Security Plus Certification Career Guide for Cleared Entry Level

Related Guides

  • BTL2 Certification Career Guide for Cleared Blue Team Level 2
  • BTL1 Certification Career Guide for Cleared Blue Team Level 1
  • Security Plus Certification Career Guide for Cleared Entry Level
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

Security Plus Certification Career Guide for Cleared Entry Level

CyberSecJobs Editorial · February 11, 2026 ·

Looking to break into cybersecurity with a clearance? The CompTIA Security+ certification is a must-have for entry-level roles in government and defense. It’s recognized under the DoD 8140.03 framework, qualifying you for 31 cybersecurity roles like Security Analyst, SOC Analyst, and Network Security Administrator. With over 82,000 job openings requiring this credential, it’s your gateway to high-demand positions and salaries starting at $45,000 to $70,000 annually.

Here’s what you need to know:

  • Exam Details: 90 questions, 90 minutes, $425 fee, passing score of 750/900.
  • Study Tips: Use video courses (e.g., Professor Messer), hands-on labs, and practice exams to prepare.
  • Clearance Advantage: Security+ certified professionals with clearance earn 25-40% more.

This guide covers everything: preparing for the exam, finding cleared jobs, optimizing your resume, and advancing your career with certifications like CySA+ or CISSP. Whether you’re a veteran or new to IT, Security+ can set you up for success in a growing field.

How to PASS Your Security+ in ONE MONTH | CompTIA Security+ Study Guide For a Complete Beginner

sbb-itb-bf7aa6b

Entry-Level Cybersecurity Roles That Require Security+

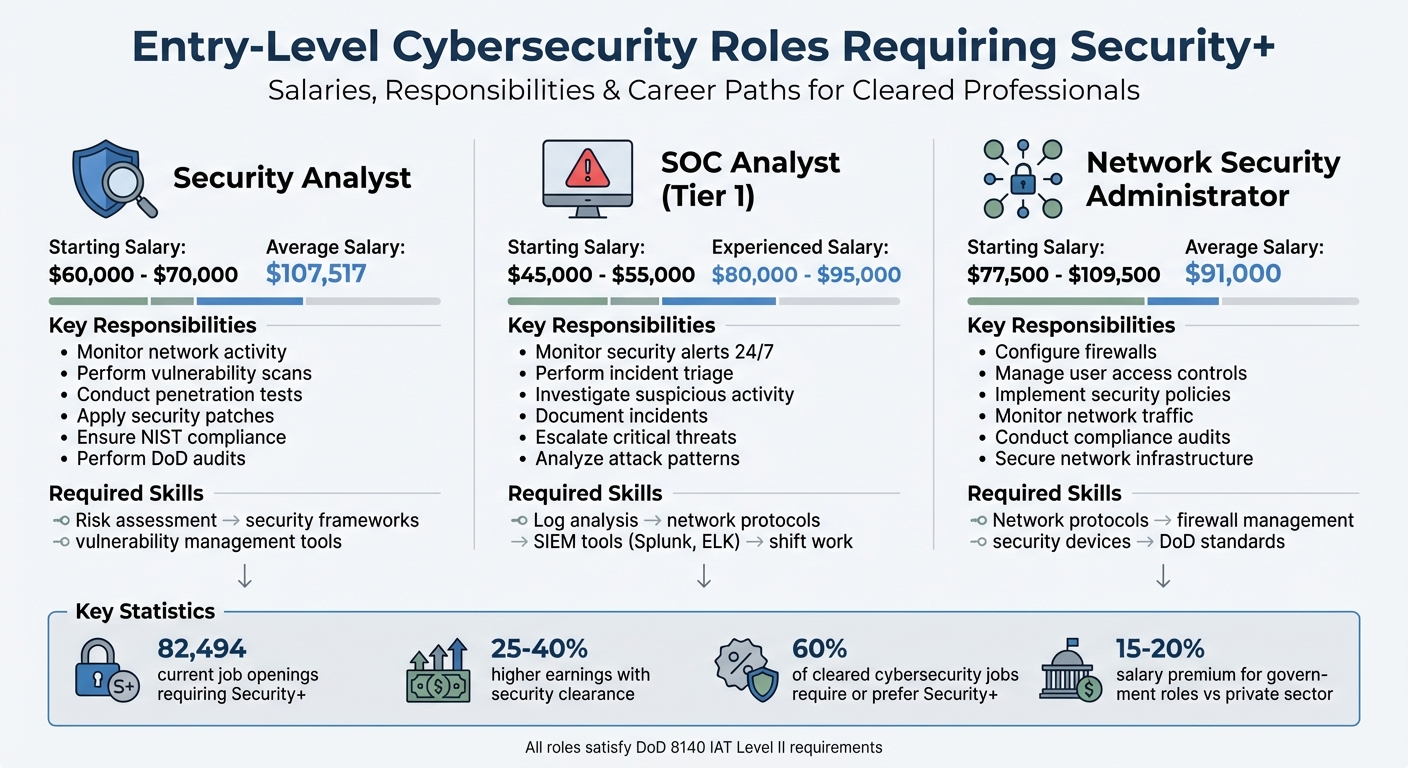
Entry-Level Cybersecurity Roles Requiring Security+ Certification: Salaries and Responsibilities

Entry-Level Cybersecurity Roles Requiring Security+ Certification: Salaries and Responsibilities

The Security+ certification is a powerful credential for cleared professionals aiming to make an immediate impact in cybersecurity. It’s required or preferred in over 60% of cleared cybersecurity job listings, with 82,494 current openings, making it the second most sought-after certification after CISSP [3][5][9]. Below are three key entry-level roles where Security+ plays a critical role.

Security Analyst

As a Security Analyst, you’ll be on the frontlines, monitoring network activity, performing vulnerability scans, conducting penetration tests, and applying critical security patches [4][5]. This role involves analyzing reports from security tools to detect unusual behavior and recommending measures to strengthen defenses [4][6]. In cleared environments, you’ll also ensure compliance with NIST frameworks and perform regular audits to meet Department of Defense (DoD) standards.

The average salary for a Security Analyst is about $107,517, with entry-level positions starting between $60,000 and $70,000 annually [4][3]. To excel, you’ll need skills in risk assessment, security frameworks, and tools for vulnerability management.

SOC Analyst

SOC (Security Operations Center) Analysts are the first line of defense in identifying and responding to threats in real time [6]. Working within a SOC, you’ll monitor alerts from tools like Splunk or ELK, perform initial incident triage, investigate suspicious activity, document incidents, and escalate critical threats to senior analysts [4][6]. This role requires constant vigilance to analyze attack patterns and prevent breaches before they escalate.

"Nearly every government job requires Sec+ for InfoSec/IT work. As most of those jobs are general IT work, if you know anything about computers and have Sec+, you can get a federal service job." – Cody Jackson, InfoSec Manager [7]

Starting salaries for Tier 1 SOC Analysts range from $45,000 to $55,000, with experienced analysts earning between $80,000 and $95,000 annually [3][6]. Key skills include log analysis, knowledge of network protocols, and the ability to work rotating shifts to ensure 24/7 security coverage.

Network Security Administrator

Network Security Administrators are responsible for managing and securing network infrastructure in cleared environments [5][8]. This includes configuring and maintaining firewalls, managing user access controls, implementing security policies, and monitoring network traffic for anomalies [4][6]. Hands-on experience with network protocols and security devices is essential for this role.

Network Security Administrators earn an average salary of $91,000, with junior roles in cleared environments offering between $77,500 and $109,500 [5][8][11]. This position is an excellent starting point for advancing into specialized roles like security architecture and involves conducting regular audits to ensure compliance with DoD security standards.

Role Average Starting Salary Key Responsibilities
Security Analyst $60,000 – $70,000 Vulnerability scanning, patching, compliance
SOC Analyst (Tier 1) $45,000 – $55,000 Alert monitoring, incident triage, documentation
Network Security Admin $77,500 – $109,500 Firewall setup, access management, policy enforcement

These roles not only offer attractive salaries but also serve as critical stepping stones in the cybersecurity field. Cleared professionals with Security+ certification tend to earn 25% to 40% more than their non-cleared counterparts. Additionally, government roles typically offer a 15% to 20% salary premium over private sector positions [10]. For veterans with security clearances, pairing their clearable status with Security+ certification can give them a significant edge in securing federal contracting jobs [2].

How to Get Your Security+ Certification

Earning your Security+ certification might be simpler than you think. There are no formal prerequisites – no degree or prior certifications are required to register for the exam. That said, CompTIA suggests having a Network+ certification and roughly two years of IT administration experience with a focus on security before attempting Security+ [16][17][20]. If you’re transitioning from the military or switching careers, don’t let this hold you back. Many professionals pass the exam with dedicated study and practical experience. Proper preparation not only helps you pass but also ensures you’re ready for cybersecurity roles requiring clearance. Now, let’s dive into the exam structure, study tools, and the registration process.

Exam Domains and Topics

The current Security+ exam (SY0-701) includes up to 90 questions – both multiple-choice and performance-based – and you’ll have 90 minutes to complete it. A passing score is 750 out of 900 [1][12]. The exam is divided into five key domains:

  • Security Operations (28%): Covers areas like incident response, asset management, and vulnerability management.
  • Threats, Vulnerabilities, and Mitigations (22%): Focuses on threat actors, attack techniques, malware, and social engineering.
  • Security Program Management and Oversight (20%): Includes governance, risk management, and compliance with frameworks like HIPAA and GDPR.
  • Security Architecture (18%): Addresses cloud models, IoT security, data protection, and system resilience.
  • General Security Concepts (12%): Covers the CIA triad, Zero Trust principles, and cryptography basics [1][13].

Performance-based questions (PBQs) are especially critical. These simulate tasks like configuring firewalls or setting up access controls, which mirror real-world scenarios in cybersecurity roles.

Study Resources and Materials

A solid "study stack" is key to passing on your first attempt. Start with video courses – Professor Messer offers free resources on YouTube, while Jason Dion’s Udemy courses are great for quick learning [14][12]. Pair these with books like Mike Meyers’ All-in-One guide or Darril Gibson’s Get Certified Get Ahead for in-depth technical insights [13][12].

"Without labs, most students forget half of what they read when preparing. If you configure a firewall rule yourself, you’ll remember it ten times longer." – Professor, Programs.com [12]

Hands-on labs are a must. CompTIA CertMaster Labs provides structured exercises, or you can create your own virtual lab using VirtualBox or VMware. Practice tasks like configuring firewalls, setting up access control lists, and running vulnerability scans [15][12]. Finally, test your readiness with practice exams from CertMaster Practice, Boson ExSim-Max, or Professor Messer. Aim to score consistently between 80% and 90% on practice tests before scheduling your exam [13].

Flashcards can also help with memorizing port numbers and acronyms. During practice exams, flag challenging questions and revisit them later – this strategy works well on the actual test since there’s no penalty for incorrect answers [13].

Prerequisites and Exam Registration

When you’re ready, log in to your CompTIA account and click "Schedule and Manage Exams" to register through Pearson VUE [18]. Choose the SY0-701 exam and decide whether to test online via OnVUE or at a Pearson VUE testing center [16][18][20]. Select your preferred date, time, and language, then complete payment or apply a voucher code at checkout [18].

The exam voucher costs $425, or $474 with a retake option. Overall, costs can range from $600–$800 for self-study materials to as much as $3,500 for bootcamps [12][13]. Active-duty military personnel might qualify for up to $2,000 in certification training funds through Army COOL or AF COOL programs [19].

Pro Tip: Ensure the name on your CompTIA account matches your government-issued ID exactly, or you could be turned away at the testing center [18]. If testing online, run a system compatibility check ahead of time to avoid technical issues with the OnVUE software [16]. You can reschedule your exam up to 24 hours before your appointment without penalty [13].

The Security+ certification is valid for three years. To renew, you can earn 50 Continuing Education Units (CEUs) or pass a higher-level exam like CySA+ or CASP+ [16][19]. For those in cleared roles, Security+ satisfies DoD 8140/8570 compliance requirements for IAT Level II positions, making it a critical credential for government and contractor jobs [19][13].

Using Security+ to Find Cleared Jobs

If you’ve earned your Security+ certification, you’re already on the right path to landing a cleared job. But certification alone isn’t enough – you need to know how to search effectively, present your credentials, and stay visible to employers. Platforms like Cleared Cyber Security Jobs are tailored for this purpose, connecting security-cleared professionals with direct-hire employers in defense and intelligence. Unlike general job boards, every position here requires U.S. citizenship and an active security clearance, ensuring you see only relevant opportunities. Below, we’ll cover how to refine your job search, craft an optimized resume, and take advantage of job alerts and events.

How to Filter Jobs on Cleared Cyber Security Jobs

Cleared Cyber Security Jobs

Start by using search filters to zero in on roles that fit your qualifications. Enter "Security+" or "CompTIA Security+" as keywords to find positions where this certification is explicitly required or preferred. Then, narrow your results by clearance level – whether it’s Secret, Top Secret, or TS/SCI. You can also filter by location, job type (full-time, part-time, contract), and experience level to target entry-level positions like Security Analyst, SOC Analyst, or Network Security Administrator.

Pay close attention to job descriptions mentioning IAT Level II or IAM Level I compliance. These categories align with Security+ certification and are essential for meeting federal requirements. Matching your qualifications to these standards is key to positioning yourself as a strong candidate.

How to Write Your Resume for Cleared Roles

Your resume should make two things immediately clear: you’re Security+ certified, and you hold a security clearance. Highlight these in your header or professional summary. For example: "Security+ certified professional with an active Secret clearance and two years of IT support experience." This ensures recruiters and Applicant Tracking Systems (ATS) can quickly identify your qualifications.

Include a dedicated "Certifications" or "Technical Skills" section to list CompTIA Security+ and other relevant credentials. Clearly state your clearance status, such as "Active Secret" or "Active TS/SCI." If your clearance is inactive but still within the 24-month reinstatement window, note it as "Inactive, Eligible for Reinstatement." Avoid mentioning sensitive details like classified project names, clearance ID numbers, or investigation dates.

When detailing your work experience, focus on measurable achievements. Instead of saying, "Supported cybersecurity operations", use specifics like: "Reduced system vulnerabilities by 35% through proactive monitoring and patch management." Use action verbs and numbers to demonstrate your impact, and align your language with the technical skills and DoD 8140 requirements listed in job postings.

"I currently hold an active Secret clearance, which enables me to support secure, mission-critical projects from day one." – MyPerfectResume [22]

Setting Up Job Alerts and Attending Job Fairs

Streamline your job search by setting up automated alerts. Save your search criteria – such as "Security+" and your clearance level – to receive email updates when new positions are posted. Completing your candidate profile with details about your clearance, certification, and skills can also make you more visible to recruiters.

Don’t overlook the value of cleared job fairs. These events connect you directly with defense and intelligence employers. For example, upcoming 2026 events include:

  • CI or FS Poly Cleared Job Fair: March 5, 2026, at the Hyatt Regency in Herndon, VA (2:00 PM – 5:30 PM)
  • All Clearances Cleared Job Fair: April 16, 2026, at the Westin in Falls Church, VA (2:00 PM – 5:00 PM)
  • Additional events: May 14, 2026, in Hanover, MD, and June 3, 2026, in Herndon, VA [21].

When attending, bring multiple copies of your resume, dress professionally, and be ready to explain how your certification and clearance align with employer needs. For veterans, these fairs can be especially helpful in transitioning to civilian roles.

"I recently transitioned out of the military and started attending Cleared Job Fairs… I was offered a position shortly after. I accepted and moved directly from the military into my current position, without a lapse in employment." – G.B., Technical Project Manager, CACI [23]

Career Growth After Security+ Certification

Earning your Security+ certification is just the beginning. It lays the groundwork for a career in cybersecurity, and after 3–5 years in cleared roles, you can transition into mid-level positions with more responsibility and higher pay. With cybersecurity roles expected to grow by 32% through 2033 [10], knowing which paths to take and how to enhance your qualifications is critical. Here’s how you can build on your entry-level experience and move forward.

Moving to Mid-Level Positions

Once you’ve gained experience in roles like Security Analyst or SOC Analyst, you can step into mid-level positions such as Incident Response Specialist, Vulnerability Analyst, or Forensics Specialist. These roles focus on tasks like risk assessment, advanced threat hunting, and creating security policies. For cleared professionals, many of these positions align with DoD 8140 requirements, where Security+ is the baseline certification for IAT Level II roles [10][24].

In the defense contracting world, mid-level roles for Security+ certified professionals often offer salaries ranging from $85,000 to $110,000 [10]. For instance, Information Security Analysts typically earn between $65,000 and $80,000 [9], with job growth in this field projected at 33% from 2023 to 2033 [11]. Security Engineers, who focus on designing and safeguarding network architecture, can earn around $150,000 [11][24]. To stand out for these roles, it’s essential to develop skills in scripting languages like Python or PowerShell and gain expertise with SIEM platforms such as Splunk or Sentinel.

Adding More Certifications

Expanding your certification portfolio is a smart way to accelerate your career. Within a year or two of earning Security+, consider pursuing certifications like CompTIA CySA+ if you’re interested in threat detection and behavioral analytics, or CompTIA PenTest+ for a focus on offensive security and vulnerability assessment [10][11].

After reaching five years of experience, aim for the CISSP (Certified Information Systems Security Professional), which is widely regarded as the top credential for senior-level roles. CISSP-certified professionals earn an average salary of $126,000 [24]. If you don’t yet meet the experience requirement, passing the exam to become an Associate of (ISC)² can still boost your profile with cleared recruiters. For those who prefer technical roles over management, CompTIA SecurityX (formerly CASP+) validates advanced skills in security architecture and engineering [10][11].

Cloud certifications are becoming increasingly important, with 94% of organizations now relying on cloud services [10]. Certifications like AWS Certified Security – Specialty (around $300) and Microsoft Azure Security Engineer (AZ-500) (around $165) are particularly valuable for cleared professionals working in government-related cloud security roles [25][26].

Specializations and Growing Fields

Specializing in areas like cloud security, threat intelligence, and incident response can open doors to some of the fastest-growing roles in cybersecurity. For example, threat hunting is expected to grow by 105%, while threat intelligence roles are projected to increase by 53% over the next five years [27]. While Security+ offers a strong foundation by covering hybrid environments such as cloud, IoT, and operational technology (OT), advancing in these fields requires platform-specific expertise.

To specialize in cloud security, focus on mastering tools like AWS IAM, VPC security, and GuardDuty, or Azure Sentinel and Azure AD. For roles in threat intelligence and incident response, certifications like CySA+ are invaluable. Additionally, building a home lab using virtual environments like VMware or VirtualBox – along with tools like Splunk, Microsoft Sentinel, and Nessus – can provide hands-on experience that employers value [10].

Cleared professionals should also consider structured government roles, such as GS-11/12 or GS-13/14 Information Security Specialist positions. These roles offer salaries ranging from approximately $55,000 to over $125,000, depending on location [10]. To stay competitive, plan to invest $3,000 to $8,000 annually in advanced certifications and industry conferences like Black Hat or RSA [10].

Conclusion

The Security+ certification is a gateway to cybersecurity roles that require security clearance. It meets the DoD Directive 8140 requirements for IAT Level II positions, which are common for entry-level jobs in defense contracting and federal agencies. With over 82,494 job listings specifically calling for Security+ certification[9], this credential opens doors to competitive salaries in a field that’s growing rapidly.

If you already have a security clearance, Security+ may be the last piece you need to qualify for these roles. Security-cleared professionals with this certification earn 25–40% more than those without clearance, and many contractors offer clearance bonuses ranging from $5,000 to $15,000 on top of base pay[10]. The exam itself costs $392[9], and you can prepare effectively using tools like CertMaster Learn and hands-on practice labs.

Once certified, update your resume to emphasize both your Security+ credential and your clearance level. Platforms like Cleared Cyber Security Jobs allow you to filter for roles requiring Security+ and set up alerts for positions like SOC Analyst, Security Administrator, or Junior InfoSec Specialist.

Keep in mind, the Security+ certification is valid for three years and requires 50 Continuing Education Units (CEUs) for renewal. Consider planning your next steps early – whether that’s CySA+ for defensive roles, PenTest+ for offensive positions, or CISSP for senior-level opportunities. With cybersecurity jobs expected to grow by 32% through 2033[10], certified professionals with security clearance will remain in high demand.

Start preparing today to secure your spot in this fast-growing and essential field. Taking this step ensures you’re ready to meet the challenges of a dynamic cybersecurity landscape.

FAQs

What clearance level is typically required for Security+ jobs?

Security+ roles frequently demand a Secret or Top Secret security clearance, especially when working with government contractors or in positions connected to national security. These clearances are crucial for handling classified information and fulfilling the responsibilities required in such high-security environments.

How long should I study for Security+ if I’m new to IT?

If you’re just starting out in IT, aim to dedicate 12 to 16 weeks – or around 200 to 300 hours – to your studies. The exact time will depend on your learning speed and prior knowledge. The key is to create a steady, consistent study routine that helps you absorb the material effectively and build a solid base for the exam.

How do I list my clearance on a resume safely?

When including your security clearance on a resume, it’s important to do so carefully and professionally. Mention the clearance level (e.g., Confidential, Secret, or Top Secret), the issuing agency (like the Department of Defense), and the date of issuance or investigation. This information is best placed near the top of your resume, either after your contact details or in your professional summary. Be mindful not to disclose any sensitive or classified details – this ensures you maintain confidentiality while effectively highlighting your qualifications.

Related Blog Posts

  • CIO-SP3 Cybersecurity Positions vs DISA Encore III – Which Vehicle Drives Your Career?
  • Cleared Resume OPSEC Guidelines – What NSA Says You Can and Can’t Say
  • Cleared Cybersecurity Career Assessment – Your Success Scorecard and Action Plan
  • GSEC Certification Career Guide for Cleared Security Essentials


Related Guides

  • BTL2 Certification Career Guide for Cleared Blue Team Level 2
  • BTL1 Certification Career Guide for Cleared Blue Team Level 1
  • CySA Plus Certification Career Guide for Cleared SOC Analysts
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

GRID Certification Career Guide for Cleared Incident Response

CyberSecJobs Editorial · February 11, 2026 ·

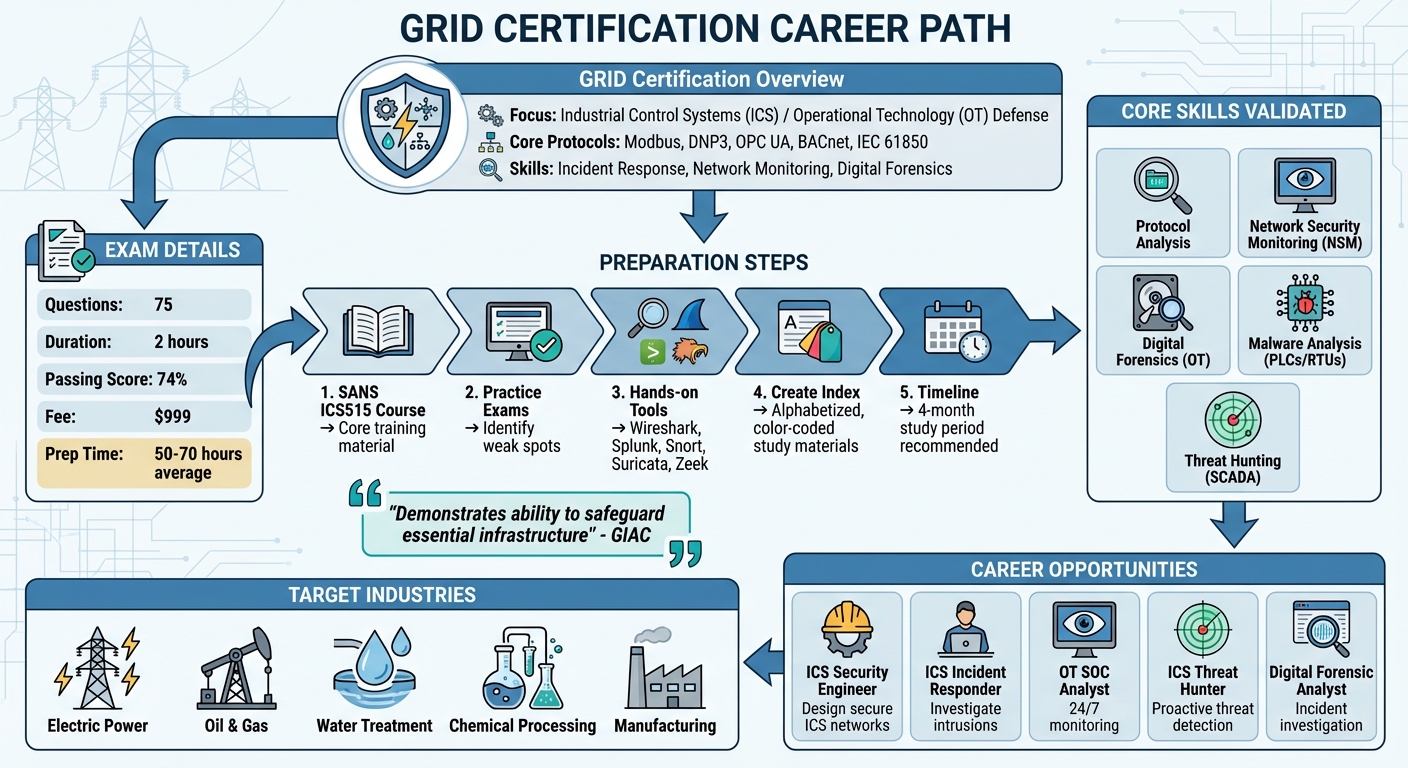
The GRID certification is a must-have for cleared professionals safeguarding critical infrastructure like power grids and water treatment facilities. It equips you with specialized skills to secure Industrial Control Systems (ICS) against cyber threats while ensuring operational continuity. Here’s what you need to know:

  • What is GRID? A certification focused on defending ICS/OT environments, covering protocols like Modbus and DNP3, incident response, network monitoring, and digital forensics.
  • Why it matters: Cyberattacks on ICS are increasing, and GRID proves you can handle threats in high-stakes environments without disrupting operations.
  • Exam details: 75 questions, 2 hours, passing score of 74%, $999 fee.
  • Career impact: Opens doors to roles like ICS Security Engineer, Incident Responder, OT SOC Analyst, and Threat Hunter in critical industries.

Preparing for GRID: Use the SANS ICS515 course, practice exams, and tools like Wireshark and Splunk to master exam topics. Focus on hands-on practice and real-world scenarios to build confidence.

Next steps: Update your job profile to highlight GRID certification, leverage cleared job platforms, and attend networking events to connect with employers in the ICS/OT sector. This certification positions you for impactful roles where your expertise protects essential operations.

GRID Certification Path: From Preparation to Career Success

GRID Certification Path: From Preparation to Career Success

Skills and Competencies Validated by GRID

Core Skills for ICS Security

The GRID certification confirms a range of technical skills tailored to securing industrial control system (ICS) networks. It goes beyond passive monitoring, focusing on mitigation and threat detection informed by real-world attack strategies [1]. This certification ensures you understand adversary tactics and how to strengthen ICS defenses accordingly.

A key area of expertise is protocol analysis, which is essential for understanding and protecting industrial networks. GRID-certified professionals are skilled in analyzing protocols like Modbus, DNP3, OPC UA, BACnet, and IEC 61850. These protocols are the backbone of systems ranging from power grids to manufacturing operations but often lack built-in security features like authentication. With GRID, you demonstrate the ability to identify normal protocol behavior and detect malicious deviations. Additionally, you gain proficiency in network security monitoring (NSM) – capturing and interpreting ICS network traffic, maintaining visibility across operational technology (OT) environments, and spotting early signs of threats.

Digital forensics in OT environments presents unique challenges, as critical systems can’t simply be taken offline for investigation. GRID certification validates your ability to analyze system memory, logs, and artifacts to investigate breaches without disrupting operations. You’ll also develop skills in malware analysis for industrial components, such as programmable logic controllers (PLCs) and remote terminal units (RTUs). On top of that, you’ll be equipped for threat hunting, proactively identifying anomalies and hidden dangers in SCADA networks.

"Earning this credential demonstrates that you’re not only well-versed in threat detection and incident response, but also capable of applying these skills in real-time, high-risk environments where mistakes can have serious consequences."
– André Hammer, Readynez [5]

Mastering these techniques involves hands-on experience with specialized tools. GRID certification ensures you’re proficient with tools like Wireshark for packet analysis, Snort for intrusion detection, Splunk for log analysis, TCPdump, and Security Onion. You’ll learn to interpret outputs to detect malformed packets or unusual command sequences in industrial traffic. GRID also emphasizes integrating threat intelligence, enabling you to anticipate adversary tactics and protect critical infrastructure effectively. These skills are essential for incident response teams operating in high-stakes environments.

How GRID Applies to Cleared Incident Response Teams

The skills validated by GRID are indispensable for incident response teams working in classified and high-risk ICS operations. For professionals safeguarding classified ICS infrastructure, this certification translates directly into operational readiness. It ensures you can detect, contain, and resolve attacks while maintaining operational continuity – where even a minor error can have serious repercussions. GRID-certified experts are equipped to handle advanced persistent threats (APTs) in critical OT environments and manage incidents in sectors like energy.

In cleared environments, asset visibility is a top priority. Many of these systems are legacy setups with undocumented networks, making it challenging to maintain oversight. GRID certification demonstrates your ability to conduct asset discovery and maintain network visibility across complex ICS setups. These skills are vital for securing infrastructure that may have been designed decades ago without modern cybersecurity considerations. With GRID, you’ll be capable of mapping attack surfaces, identifying vulnerable components, and maintaining situational awareness during active incidents. The certification also confirms your ability to apply threat intelligence, helping you anticipate how state-sponsored actors and other sophisticated adversaries might target critical systems.

sbb-itb-bf7aa6b

How to Prepare for the GRID Certification Exam

Study Resources and Training Options

The cornerstone of preparing for the GRID certification is the SANS ICS515: ICS Visibility, Detection, and Response course[2]. This course delivers essential material, hands-on labs, and exercises designed to help you succeed in the exam. To accommodate busy professionals, SANS provides flexible delivery options, making it easier to fit studying into a packed schedule.

Beyond the official course, GIAC practice exams are a must-have tool. These practice tests mimic the actual exam, giving you a feel for the question style and helping you pinpoint areas that need more attention. On average, candidates spend 50 to 70 hours preparing, but this can vary depending on your prior experience with ICS/OT systems[2].

Practical skills are just as important as theoretical knowledge. Spend time working with tools like Wireshark, Splunk, and intrusion detection systems such as Snort, Suricata, and Zeek. Familiarize yourself with the MITRE ATT&CK for ICS framework and study incident analyses like Triton, Industroyer, and Stuxnet. These resources will deepen your understanding of real-world scenarios and align with the GRID certification’s focus.

Preparation Tips for Cleared Professionals

For cleared professionals juggling operational duties, having a focused strategy is critical. Start by creating a personalized, alphabetized, color-coded index of your printed study materials. Highlight key terms, protocol behaviors (e.g., "Modbus = no authentication"), and reference specific pages in the SANS courseware. A well-organized index is invaluable since you’ll have about 90 seconds per question to locate information during the exam.

Schedule your practice tests strategically. Take one midway through your study period to identify weak spots and another 3–5 days before the exam to simulate test conditions and improve your indexing speed. Use active study methods – complete labs on your own first, then review the solutions and note key takeaways.

GIAC recommends starting your preparation immediately after the training, aiming for a four-month study timeline. For professionals with limited time, prioritize hands-on practice over passive reading. Capture and analyze ICS protocol traffic – such as Modbus, DNP3, and BACnet – using tools like Wireshark. This approach reinforces your practical skills and ensures you’re ready for the GRID exam.

Career Opportunities with GRID Certification

Cleared Job Roles That Require GRID

Earning a GRID certification can open doors to specialized roles in industries like electric power, oil & gas, water treatment, chemical processing, and manufacturing. These sectors rely on professionals with the skills to secure and defend Industrial Control Systems (ICS) networks – precisely what the GRID certification validates.

ICS Security Engineers are responsible for designing and implementing secure ICS network systems in cleared environments. They collaborate with control system experts and operational teams to manage firewall logs, intrusion detection systems, and endpoint security tools. Their work also ensures compliance with regulations like NERC CIP. Meanwhile, ICS Incident Responders focus on investigating intrusions in industrial environments, providing remediation, and maintaining constant vigilance to ensure operational safety and uptime.

OT SOC Analysts monitor ICS protocols around the clock, using security intelligence and anomaly detection to identify malicious activity in industrial networks. ICS Threat Hunters apply their expertise in ICS-specific threat analysis to actively track adversaries within critical infrastructure. Additionally, Digital Forensic Analysts investigate incidents and analyze data from Windows and Linux systems in industrial settings, applying digital forensics and incident response (DFIR) techniques tailored to ICS environments.

These roles highlight why GRID certification is a powerful asset for advancing careers in cleared, high-security environments.

How GRID Advances Your Career

The GRID certification signals to employers that you have over two years of relevant experience and a specialized skill set. It’s particularly valuable because it bridges the gap between traditional IT security and Operational Technology (OT) – a combination crucial for protecting national infrastructure.

"Earning an ICS certification confirms your ability to safeguard essential infrastructure and demonstrates your value in the workplace." – GIAC Certifications [3]

This certification validates a wide range of skills, including ICS-focused digital forensics, incident response, network security monitoring, and threat hunting. For cleared professionals, it paves the way to higher-paying roles and career growth in industries where safeguarding sensitive assets is critical. With a $999 investment [4], GRID positions you for senior roles that demand proven expertise in ICS defense. Beyond enhancing your technical skills, it sharpens your focus for pursuing job opportunities in high-stakes environments where your contributions truly matter.

Using Cleared Cyber Security Jobs for GRID-Certified Job Searches

How to Optimize Your Job Search

Cleared Cyber Security Jobs allows you to leverage your security clearance and GRID certification to stand out in the specialized field of ICS incident response. Start by building a complete profile that clearly displays your clearance level – whether it’s Secret, TS/SCI, or TS/SCI with CI Poly – and highlights essential skills like GRID, ICS Security, Active Defense, and Network Security Monitoring. The platform uses AI-driven matching, combining Boolean and semantic search methods, to pair you with roles that align with both your security clearance and ICS/OT expertise.

To refine your search, set up alerts using keywords like ICS Incident Response, OT Security, and Active Defense so you’re notified as soon as relevant positions are posted. You can also use Boolean search strings (e.g., "GRID" OR "ICS Security") to narrow down results effectively. Be sure to select all applicable clearance levels and include a Zip Code with a specific mileage radius to broaden your reach.

Your profile is often the first thing recruiters see, even before your resume, so make sure it emphasizes your GRID certification and ICS-related skills. Keeping your profile updated ensures you’re visible to recruiters and ready for new opportunities. These adjustments also lay the groundwork for successful networking, which we’ll explore next.

Networking and Job Fairs

In addition to optimizing your online profile, attending networking events and job fairs is a key step in advancing your career. Cleared Cyber Security Jobs organizes both virtual and in-person hiring events, giving you direct access to recruiters from defense and intelligence contractors. Upcoming events include:

  • Cleared Careers Virtual Huntsville Hiring Event – February 19, 2026
  • Cleared Careers Hiring Event at UCCS in Colorado Springs – April 2, 2026
  • Cleared Careers Nationwide Virtual Hiring Event – May 12, 2026

These events are a great chance to showcase the unique value of your GRID certification and demonstrate how your expertise in ICS incident response and active defense contributes to protecting critical infrastructure.

When you upload your resume to the platform, it’s tagged for specific job fairs, making it easier for employers to find professionals with specialized certifications like GRID. Subscribing to the Cleared+ newsletter can also keep you informed about GovCon companies, providing insights into contract activity, hiring trends, and mission priorities – valuable information for targeting employers actively hiring for ICS/OT roles.

As you network, be ready to discuss real-world incident response scenarios and explain how GRID equips you with a practical, effective approach to safeguarding operational technology environments.

"Intrusion detection, incident response and digital forensics are my everyday working areas. My GIAC certs provided a practical framework that is comprehensive and effective. Clients trust my work when they know I’m certified." – Juan Manzano, GSE [6]

Conclusion and Next Steps

Key Takeaways

The GRID certification stands out as a vital credential for professionals focused on defending industrial control systems (ICS). It equips cleared incident response experts with the skills needed to tackle the unique challenges of operational technology (OT). Unlike general IT certifications, GRID zeroes in on defending critical infrastructure where uptime, safety, and resilience are non-negotiable. From asset discovery and network monitoring to digital forensics and incident response, this certification validates your ability to safeguard systems like power grids and water treatment facilities against advanced cyber threats.

Earning the GRID certification requires thorough preparation. Understanding the exam’s format, duration, passing criteria, fees, and renewal process is essential for success. These details not only prepare you for the exam but also guide your next steps as you plan your career in ICS defense.

Next Steps for GRID-Certified Professionals

Now that you’ve earned your GRID certification, it’s time to put it to work. Start by updating your Cleared Cyber Security Jobs profile to highlight your clearance and GRID expertise, ensuring you’re visible to employers looking for professionals with your skills.

Stay informed about the latest ICS threats by making daily reading a habit. Cybersecurity recruiter Josh Fullmer from Dragos advises, "Pick one or two relevant resources and read something every day" [7]. Hands-on experience is just as important – continue honing your skills with tools like Wireshark, Splunk, and Snort.

Expand your professional network by joining organizations such as ISSA or (ISC)² and attending industry events like RSA, Black Hat, or AFCEA conferences. These opportunities not only keep you ahead of emerging threats but also connect you with potential employers in the critical infrastructure sector. Your GRID certification positions you to take on roles where you’ll play a key part in protecting systems that millions depend on daily.

ICS515: ICS Visibility, Detection, and Response | GRID

FAQs

Is GRID worth it if I’m new to ICS/OT?

Yes, the GRID certification is worth pursuing, even for beginners in ICS/OT. It lays a solid groundwork in areas like active defense, ICS-specific threats, and incident response strategies. These skills are crucial for safeguarding industrial control systems, making this certification a meaningful step toward developing expertise in this specialized domain.

What hands-on skills should I practice most for the GRID exam?

To prepare effectively for the GRID exam, concentrate on mastering active defense concepts, detection and analysis techniques, and ICS-focused digital forensics. It’s equally important to gain practical experience in areas like incident response, malware analysis, threat analysis, and threat intelligence fundamentals. These skills not only align with the exam’s core objectives but are also critical for success in the field.

How do I translate GRID into cleared incident response job interviews?

When it comes to protecting industrial control systems (ICS), active defense strategies are essential. These systems, which often manage critical infrastructure like power grids, water treatment facilities, and transportation networks, face unique threats that require specialized approaches. Active defense involves not just reacting to threats but proactively identifying and mitigating risks before they escalate. This includes monitoring network traffic for anomalies, deploying intrusion detection systems tailored to ICS protocols, and implementing segmentation to limit lateral movement within the network.

ICS-Specific Digital Forensics

Digital forensics in ICS environments is a highly specialized field. Unlike traditional IT systems, ICS devices often use proprietary protocols and hardware, making forensic investigations more complex. Expertise in ICS-specific digital forensics means understanding how to extract, analyze, and preserve data from these systems without disrupting operations. This skill is critical for identifying the root cause of incidents and ensuring that evidence is admissible for legal or regulatory purposes.

Threat Analysis and Incident Response Techniques

Threat analysis in ICS environments requires a deep understanding of the unique attack vectors and vulnerabilities these systems face. From supply chain risks to insider threats, the ability to analyze and prioritize risks is crucial. Incident response techniques for ICS must be tailored to minimize downtime and avoid further damage. This includes creating detailed response plans, coordinating with operational technology (OT) teams, and ensuring compliance with industry regulations.

Protecting Critical Infrastructure and Addressing ICS-Specific Threats

The stakes are incredibly high when it comes to ICS. A single breach can have far-reaching consequences, from economic disruption to public safety risks. By combining active defense, specialized forensics, and targeted incident response, it’s possible to address ICS-specific threats effectively. These skills not only protect critical infrastructure but also demonstrate the ability to navigate the unique challenges of cleared incident response roles, where precision and expertise are non-negotiable.

Related Blog Posts

  • OT Security Clearance Jobs – The Critical Infrastructure Opportunity
  • GCIH Certification Career Guide for Cleared Incident Handlers
  • GSEC Certification Career Guide for Cleared Security Essentials
  • GICSP Certification Career Guide for Cleared ICS Security

Related Guides

  • CHFI Certification Career Guide for Cleared Forensic Investigators
  • GREM Certification Career Guide for Cleared Malware Analysts
  • GNFA Certification Career Guide for Cleared Network Forensics
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

GICSP Certification Career Guide for Cleared ICS Security

CyberSecJobs Editorial · February 11, 2026 ·

The Global Industrial Cyber Security Professional (GICSP) certification is designed for professionals securing industrial control systems (ICS) in critical environments. It focuses on bridging IT and operational technology (OT) skills, addressing unique challenges in sectors like energy, water, and manufacturing. GICSP is recognized by the U.S. Department of Defense (DoD) 8570.0.1 program and qualifies for roles such as IAT Level II, CND-A, and CND-IS.

Key Takeaways:

  • Who Should Consider GICSP? IT professionals, OT security analysts, engineers, and managers in ICS environments.
  • Exam Details: 82 questions, 3 hours, 71% passing score, costs $1,899. Open-book format with printed materials allowed.
  • Career Benefits: Average salary of $135,000; applicable to roles in critical infrastructure and defense sectors.
  • Preparation Tips: Study SANS ICS410, practice with tools like Wireshark, and create a detailed index for the open-book exam.

This certification is ideal for cleared professionals looking to validate their ICS security expertise and advance in high-demand roles.

Who Should Get GICSP Certification?

Cleared Professionals in ICS/OT Security

The GICSP certification is designed for IT professionals, OT security analysts, security engineers, and managers responsible for safeguarding industrial control system (ICS) environments [8].

"The GICSP assesses a diverse set of professionals who engineer or support control systems and share responsibility for the security of these environments." – GIAC [8]

Roles that benefit the most include SCADA Security Engineers, OT Cybersecurity Specialists, Critical Infrastructure Analysts, and ICS Consultants [9][10]. These professionals often operate in critical sectors like energy (including nuclear facilities), manufacturing, water treatment facilities, and transportation hubs such as airports [10]. For cleared professionals working in defense and critical infrastructure, the certification validates their expertise in securing environments where failures can lead to severe consequences.

The certification is especially useful for those transitioning from IT security into operational technology (OT) roles. Control system engineers and SCADA technicians leverage GICSP to demonstrate their ability to protect industrial processes [12]. With an average base salary of around $135,000 for GICSP-certified professionals [10], it’s clear that the certification holds strong value in the job market for specialized OT security skills.

This focus on specialized knowledge lays the groundwork for the experience and skills required, as outlined below.

Experience and Skills Needed

Although GICSP doesn’t mandate extensive experience, candidates should have a solid grasp of IT and OT fundamentals, making it an accessible option for those moving into critical infrastructure roles [9][10]. Many candidates pursue the certification after gaining 1–2 years of ICS or IT experience to further develop their expertise.

Before diving into GICSP, candidates should understand basic computer networking and security protocols. Earning a CompTIA Network+ certification is often recommended as a foundational step [11]. For cleared professionals, maintaining an active security clearance is crucial, as many roles tied to GICSP involve sensitive defense and critical infrastructure systems. Additionally, the certification can be applied toward fulfilling one year of the five-year experience requirement for the CISSP certification, making it a valuable stepping stone for those aiming for leadership positions in the future [10].

sbb-itb-bf7aa6b

Career Benefits of GICSP Certification

Bridging the IT-OT Skills Gap

The GICSP certification is a game-changer for professionals working at the intersection of IT and OT in critical infrastructure security. As industrial systems become more interconnected, there’s a growing demand for individuals who can effectively operate in both domains. This certification equips you with the expertise to blend IT security protocols with OT-specific needs seamlessly [7][14].

"GICSP holders are not constrained by silos – they are the integrators, the polymaths who can explain to a field technician why a firewall rule matters, or to a CISO why a firmware update might compromise uptime." – Prepaway [7]

This ability to navigate both worlds is especially valuable in industries where cyber threats can cause physical harm, such as disrupting energy grids or halting production lines. The certification’s focus on dual-domain knowledge not only boosts your technical versatility but also enhances your career prospects, including compensation and advancement opportunities.

Job Market Demand for GICSP-Certified Professionals

The GICSP credential isn’t just about technical know-how – it’s also a powerful career asset. With IT and OT integration becoming a priority, certified professionals are in high demand. Financially, the numbers speak volumes: GICSP holders in the U.S. earn an average annual salary of $104,852, with top earners reaching $139,500 [14]. On top of that, these professionals typically earn 15% to 25% more than their non-certified counterparts, with salary increases often ranging from 10% to 30% [14].

The certification also opens doors to senior-level roles such as ICS Security Architect, Industrial Systems Analyst, and Cybersecurity Program Manager [7]. For those working in defense or government sectors, the GICSP is approved under the U.S. Department of Defense (DoD) 8570.0.1 Information Assurance Workforce Improvement program. It qualifies for categories like CND-A, CND-IS, and IAT Level II, making it a valuable credential for positions requiring validated ICS security expertise [14][5].

One of the standout advantages of GICSP is its adaptability across industries. Certified professionals are recognized as experts in cyber-physical systems, making them sought after in fields like oil and gas, utilities, manufacturing, transportation, and healthcare automation [7]. This cross-sector relevance ensures that your certification remains valuable, no matter where your career takes you.

Compliance and Industry Standards

As regulatory scrutiny tightens across critical infrastructure sectors, having a GICSP certification positions you as a key player in ensuring governance and audit readiness. The skills you gain directly support compliance with major frameworks such as NERC CIP (North American Electric Reliability Corporation Critical Infrastructure Protection), NIST 800-82, and IEC 62443 [7][14]. For those in defense-related roles, the certification also helps meet Cybersecurity Maturity Model Certification (CMMC) requirements, which are becoming increasingly important for contractors [7].

Global organizations also value GICSP-certified professionals for their expertise in international compliance standards, including the European NIS Directive [7]. As cyberattacks on industrial systems grow in frequency and complexity, industries face stricter enforcement of these standards [2][7][14]. Your certification demonstrates not only technical proficiency but also a solid understanding of the regulatory landscape surrounding critical infrastructure.

Independent contractors and consultants find the GICSP particularly beneficial when navigating diverse compliance requirements. It validates your ability to adapt security principles to the unique needs of different industries, making you a trusted advisor in managing complex regulatory environments [7].

How to Prepare for the GICSP Exam

Preparation Steps

Start by reviewing the GIAC GICSP blueprint, which outlines key areas like ICS architecture, attack surfaces, defense strategies, incident response, and governance [8]. A great resource to consider is the SANS ICS410: ICS/SCADA Security Essentials course. This course is tailored to match these objectives and dives into topics like the Purdue Reference Architecture (Levels 0–3) and hands-on protocol analysis [17].

To make the most of your open-book exam, create a well-organized physical index. Alphabetize definitions and explanations from your study materials for quick reference [14]. Since digital resources aren’t allowed, this index can be a lifesaver. Tools such as Voltaire or Lesley Carhart’s GIAC Indexing Guide offer helpful tips for structuring it [17]. If you’re working full-time, aim to dedicate 2–3 hours on weekday evenings and full days on weekends, allowing about 3–4 weeks for preparation [17].

Hands-on skills are also critical. Practice using tools like Wireshark for analyzing industrial protocols, and get comfortable with PowerShell, Linux command-line operations, and basic PLC programming (like ladder logic) [18]. These skills are especially important for the CyberLive sections of the exam, where you’ll solve practical security challenges using real code and virtual machines [8]. This blend of theoretical study and hands-on practice will prepare you for both the exam and real-world scenarios.

Study Resources and Tools

Alongside the SANS ICS410 course, GIAC’s official practice tests are a must. They simulate the 3-hour exam environment and help you identify any weak areas [17]. As Keirsten Brager, a Lead Security Engineer, points out:

"The practice tests in the course are meant to reinforce the knowledge gained in the course, not pass the GIAC exam. GIAC has its own practice exams that simulate the real environment."

These practice exams cost around $399 and closely mirror the actual test format [14].

For additional study, consider the book Practical Industrial Cybersecurity: ICS, Industry 4.0, and IIoT by Wiley, which is specifically designed to support GICSP exam preparation [19]. Spending time in virtual lab environments like CyberLive is also highly recommended. These labs let you work with real programs and code, sharpening your practical skills [8]. During the exam, aim to answer multiple-choice questions in about one minute each, leaving enough time for the hands-on scenarios [18].

Once you’ve gathered your resources and mapped out your study plan, take time to familiarize yourself with the exam format and related costs.

Exam Format, Cost, and Requirements

You can take the exam remotely through ProctorU or in person at PearsonVUE testing centers [8]. It’s open-book, meaning you can bring printed materials and your index, but digital resources are strictly prohibited [14]. The exam structure emphasizes hands-on skills, reflecting the practical focus of the certification.

For remote testing, you’ll need two forms of government-issued ID, such as a driver’s license and passport, and these must match the details on your exam record [17].

The exam costs $1,899 for the initial attempt, with retakes priced at about $899 after a required 30-day waiting period [14]. Other expenses include a $175 reseating fee for missed exams and a certification renewal fee of approximately $499 every four years [14]. Keep in mind, you have 120 days from the activation date to complete your certification attempt [8], so plan your schedule wisely.

How to Prepare for GICSP Certification Without SANS Training | Your Self-Study Guide

SANS

Cleared ICS Job Roles That Value GICSP Certification

GICSP Certification Salary Ranges by Job Role

GICSP Certification Salary Ranges by Job Role

Common Cleared ICS Security Roles

The GICSP certification is a game-changer for professionals aiming to secure roles in critical infrastructure protection. It’s especially relevant for positions like ICS Security Engineers and ICS Security Specialists, who are responsible for designing, implementing, and maintaining the security of networked control systems. These roles often involve monitoring firewall logs, managing intrusion detection systems, and ensuring endpoint security in industrial environments [20]. A solid grasp of the Purdue Reference Architecture and hands-on experience with both IT and operational technology are essential for these positions.

Another key role is that of OT Cybersecurity Analysts, who focus on investigating intrusions and identifying vulnerabilities in systems that manage physical processes [1][20]. Similarly, Cyber Security Software Engineers work on creating software solutions tailored to address industrial security challenges [20]. The GICSP certification is particularly valuable in these roles because of its vendor-neutral approach, bridging the gap between IT, engineering, and cybersecurity disciplines [1][13].

Industries like electric power, oil and gas, water, chemical production, and critical manufacturing place a high value on this certification [20].

Finding GICSP-Aligned Roles on Cleared Cyber Security Jobs

Cleared Cyber Security Jobs

For those with a GICSP certification, Cleared Cyber Security Jobs offers a tailored platform to connect with employers in the ICS space. Their search tools help you identify positions that specifically list GICSP as a preferred or required qualification. By uploading your resume, you can directly apply for cleared ICS roles with hiring organizations.

The platform also provides job alerts customized to your certification, notifying you when relevant openings arise. Since all employers on the site are direct-hire organizations, you’ll bypass third-party recruiters and connect directly with companies looking for cleared professionals. Additionally, job fairs hosted by the platform offer a chance to meet hiring managers from critical infrastructure sectors in person. Importantly, these services are free for job seekers, though U.S. citizenship and an active security clearance are required to access the full range of opportunities. This streamlined process makes it easier to transition from certification to career advancement.

Salary Ranges and Role Comparisons

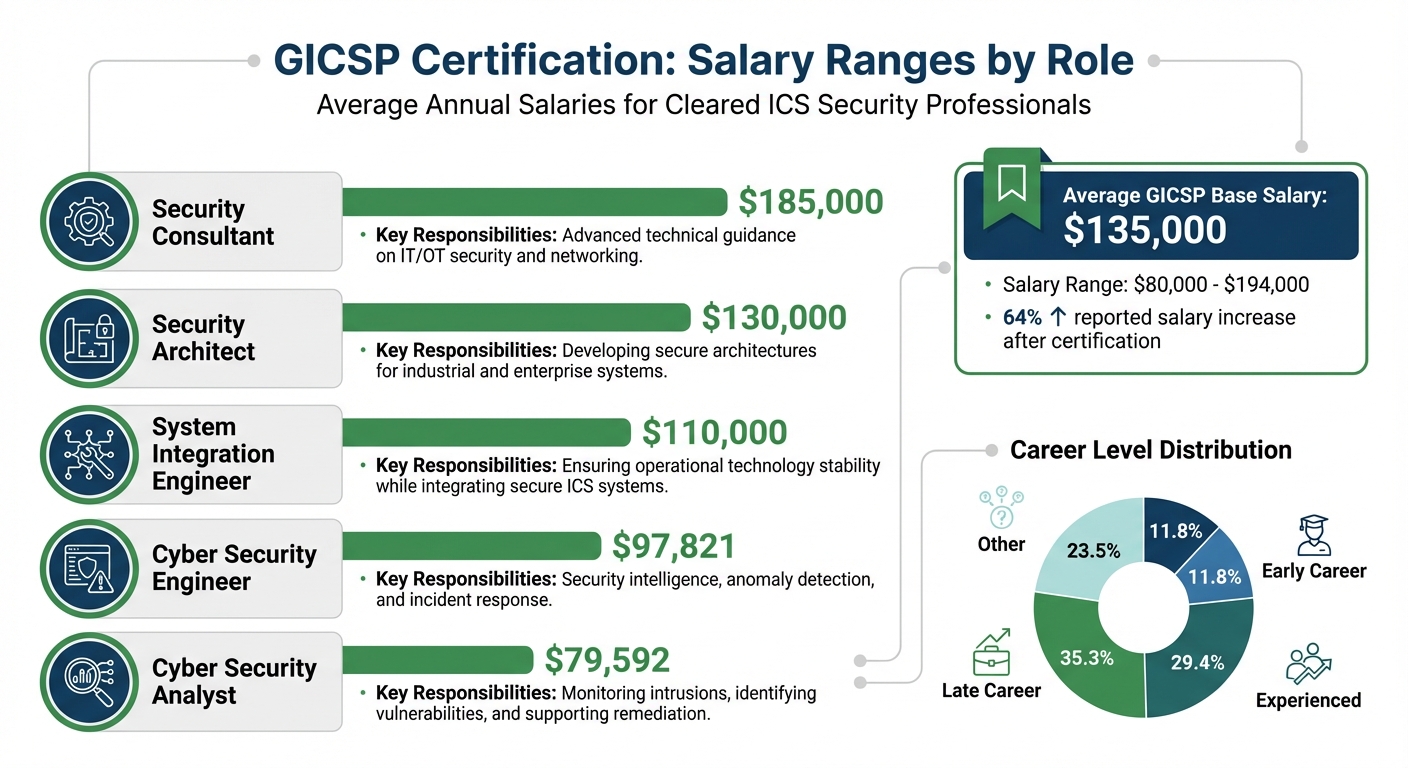
GICSP-certified professionals enjoy competitive salaries, with an average base salary of around $135,000 per year. Depending on the role, experience, and complexity of the systems involved, salaries range from $80,000 to $194,000 [15][16].

Job Title Average Salary Key Responsibilities
Security Consultant $185,000 Offering advanced technical guidance on IT/OT security and networking [16]
Security Architect $130,000 Developing secure architectures for industrial and enterprise systems [16]
System Integration Engineer $110,000 Ensuring operational technology stability while integrating secure ICS systems [16]
Cyber Security Engineer $97,821 Conducting security intelligence, anomaly detection, and incident response [15][20]
Cyber Security Analyst $79,592 Monitoring for intrusions, identifying vulnerabilities, and supporting remediation [15][20]

Statistics show that 64% of professionals reported a salary increase after earning certifications like the GICSP [13]. The majority of GICSP holders are seasoned professionals, with 35.3% in "Late Career" and 29.4% classified as "Experienced." Only 11.8% fall into the "Early Career" category [15]. This distribution aligns with the certification’s prerequisites, which include at least two years of work experience and post-secondary education [3].

Next Steps for Certification and Career Growth

Steps to Get Certified

Once your study plan is in place, it’s time to take action and secure your certification. To qualify, you’ll need at least two years of work experience and two years of post-high school education or training [3]. While these are the baseline requirements, many candidates choose to prepare through the SANS ICS410: ICS/SCADA Security Essentials course [6]. If you decide to take this course, it’s a smart move to schedule your exam as soon as you complete it – this helps keep the momentum going [2].

The process itself is straightforward: submit your application, formally agree to the GIAC Code of Ethics, and schedule your exam. You’ll have 120 days from account activation to complete the exam, which can be taken through ProctorU or PearsonVUE [1][3][4].

Using GICSP to Find Job Opportunities

Once you’ve earned your GICSP certification, it’s time to put it to work. Start by updating your resume on Cleared Cyber Security Jobs, a platform that connects you directly with hiring managers looking for GICSP-certified professionals. Use the platform’s search tools to pinpoint jobs where GICSP is listed as a preferred or required qualification, and set up job alerts to get notified about new opportunities tailored to your certification.

The GICSP certification also meets several Department of Defense (DoD) requirements, including IAT Level II, CND-A, and CND-IS, under DoD 8570.0.1 [5]. Highlighting this compliance on your resume can open doors to federal positions in critical sectors like energy, transportation, and federal network defense [13][5]. Once you’ve secured a role, staying current with your certification will ensure long-term career success.

Maintaining Your Certification

Your GICSP certification is valid for four years, but to renew it, you’ll need to earn 36 CPE credits or retake the latest version of the exam [21][3][22]. To make the renewal process smoother, it’s a good idea to track your CPE credits early by regularly logging into your GIAC account. Attending SANS training events and industry conferences can help you earn these credits while staying up-to-date with the latest industry trends [21].

Maintaining your certification not only keeps you competitive but also enhances the career benefits you’ve already gained. For instance, 64% of professionals reported salary increases after earning certifications like the GICSP [13]. To take your career further, consider adding related certifications to your portfolio, such as GIAC Response and Industrial Defense (GRID) or GIAC Critical Infrastructure Protection (GCIP) [2][6].

FAQs

Is GICSP worth it if I’m new to ICS/OT?

The GICSP certification can be a great asset, even for those just starting in the ICS/OT field. It introduces key concepts and provides a solid base in industrial control systems security, making it accessible to professionals regardless of their experience level. Beyond foundational knowledge, it also helps you develop practical skills and enhances your credibility in the ICS/OT domain, which can open doors for career advancement and align well with industry demands.

What should I bring to the GICSP open-book exam?

For the GICSP open-book exam, make sure to bring a valid form of identification and any reference materials that the exam provider specifically allows. Since this is an online, proctored exam, it’s important to carefully review the official instructions provided by GIAC or the testing service ahead of time. Double-check the guidelines to ensure you’re fully prepared and have all necessary items ready for exam day.

Which cleared job titles most often require GICSP?

The GICSP certification is frequently associated with roles like ICS Security Engineer and ICS Security Specialist. These positions typically focus on protecting industrial control systems, making this certification a sought-after qualification for professionals working in cleared ICS security roles.

Related Blog Posts

  • OT Security Clearance Jobs – The Critical Infrastructure Opportunity
  • GCIH Certification Career Guide for Cleared Incident Handlers
  • GSEC Certification Career Guide for Cleared Security Essentials
  • GCWN Certification Career Guide for Cleared Windows Security

Related Guides

  • Splunk Certification Career Guide for Cleared SIEM Analysts
  • ECSA Certification Career Guide for Cleared Security Analysts
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

GCWN Certification Career Guide for Cleared Windows Security

CyberSecJobs Editorial · February 11, 2026 ·

The GCWN certification, offered by GIAC, validated skills in securing Microsoft Windows systems, especially in government and military environments. However, as of early 2026, it is no longer available for new candidates. Current holders can maintain it through Continuing Professional Education (CPE) credits every four years.

Key points about the GCWN certification:

  • Focus Areas: PowerShell security, PKI management, Group Policy, AppLocker, system hardening, and Zero Trust policies.
  • Target Audience: Professionals with over two years of experience in Windows security, especially in cleared environments.
  • Exam Details: 75 questions, 120 minutes, passing score of 66%, and open-book format.
  • Training: SANS SEC505 course is recommended for preparation, with materials like textbooks, MP3s, and hands-on labs.
  • Recognition: Aligned with DoD 8570.01-M and 8140 frameworks, making it valuable for information assurance roles in government and military sectors.

Although the certification is now in abeyance, those who already hold it can leverage its benefits for career growth, salary increases, and specialized roles in cleared environments. Maintaining the certification ensures continued relevance in the cybersecurity job market.

GCWN Certification Requirements and Exam Details

GCWN Certification Exam Requirements and Specifications

GCWN Certification Exam Requirements and Specifications

Prerequisites for the GCWN Certification

The GCWN certification is aimed at professionals with over two years of experience in Windows security administration [5]. While GIAC doesn’t enforce formal prerequisites, having at least an Associate degree or equivalent hands-on experience is strongly recommended [5]. A solid background in Windows installation, configuration, and security – particularly with tools like PowerShell and PKI – can greatly enhance your readiness for the exam [1][7].

The SEC505: Securing Windows and PowerShell Automation course, offered by SANS, is the primary recommended training [7]. This certification is tailored for Windows administrators, blue team members, and professionals involved in government or military cyber defense [1]. If you’ve worked in these roles, your practical experience will be a valuable asset when preparing for the exam.

Exam Format and Core Topics

The GCWN exam includes 75 questions to be completed within a 120-minute time limit [6]. To pass, you’ll need a score of at least 66%, which translates to about 50 correct answers out of 75 [6]. The exam is conducted online and is proctored either remotely through ProctorU or onsite at PearsonVUE testing centers [1]. Once you activate your certification attempt, you’ll have 120 days to complete the exam [1].

Exam Component Specification
Number of Questions 75 [6]
Time Limit 120 minutes [6]
Passing Score 66% [6]
Exam Price $999 USD [6]
Completion Window 120 days from activation [1]
Certification Validity 4 years [5]

The exam focuses on six major areas:

  • PowerShell fundamentals: Covers objects, properties, methods, and scripting [6].
  • Remote command execution: Includes configuring PowerShell Remoting, OpenSSH, and Just Enough Admin (JEA) [6].
  • Active Directory and WMI scripting: Focuses on managing Group Policy and permissions [6].
  • Endpoint and PowerShell security: Involves implementing tools like AppLocker, Credential Guard, and advanced logging [6].
  • Hardening services and features: Covers Windows Firewall, IPsec zero trust policies, and audit policies [6].
  • Windows Certificate Services: Focuses on PKI for multi-factor authentication and digital signatures [6].

These areas are designed to address the unique security demands of environments where protecting sensitive or classified networks is a top priority.

sbb-itb-bf7aa6b

How to Prepare for the GCWN Exam

Study Materials and Resources

The SANS SEC505 course is a comprehensive package that includes textbooks, MP3 recordings, and lab exercises, all offered at a lower price when bundled with the exam voucher. Opting for this bundle is a more budget-friendly choice compared to purchasing the exam voucher separately, which costs $999. The course provides five to six textbooks that align with the exam objectives, along with audio files and hands-on lab exercises to enhance learning.

SANS also caters to different schedules with its flexible training formats. The Live Online format allows you to join instructor-led sessions from anywhere, while the OnDemand option lets you progress at your own pace. These formats are particularly helpful for professionals with security clearances who need to balance their classified work with exam preparation.

The GCWN exam is open-book, meaning you can bring hard-copy materials like textbooks and a personal index (electronic devices are not allowed). Crafting a detailed, color-coded index is crucial for quickly locating information during the test. GIAC emphasizes the importance of creating your own index as part of the learning process:

The whole point in building your own index is so you’ll learn and retain the material. Asking for mine or taking someone else’s is a shortcut that will likely lead to your own disappointment come exam time.

Additionally, candidates have access to practice exams, which are invaluable for identifying weak areas early in the 120-day study period. These resources form the foundation for effective preparation, as outlined below.

Study Tips for Cleared Professionals

GIAC exam candidates typically dedicate over 55 hours to studying. With a four-month window to prepare, you can break your study time into manageable sessions that fit around work and personal obligations. Using the provided materials and adopting consistent study habits will help you meet your exam goals.

Set up a study schedule with regular time blocks each week, choosing moments when you’re least likely to be interrupted – early mornings or evenings often work well. Use commute time to listen to the MP3 audio summaries, reinforcing key topics. Take a practice test early on to pinpoint areas that need extra attention, then adjust your study plan to focus on those gaps.

Hands-on practice is essential for mastering skills like PowerShell automation and Windows hardening. Repeat the course labs until you can confidently execute scripts and configurations without needing to refer to instructions. Whenever possible, apply what you’re learning to real-world tasks at work. This not only reinforces your understanding but also demonstrates the practical value of your skills.

Teaching a concept to someone else is another powerful way to solidify your knowledge. GIAC highlights this approach:

If you can teach someone else how a concept works, you’ve successfully mastered that idea or skill.

Start studying as soon as you complete the training to keep concepts fresh in your mind. Following these strategies will not only prepare you for the exam but also enhance your expertise in securing Windows environments, a critical skill for cleared professionals.

Career Benefits of the GCWN Certification

Career Growth in Cleared Windows Security Roles

Earning the GCWN certification opens doors to specialized roles in government and military cyber defense. It validates expertise in key areas like PowerShell automation, PKI management, Group Policy, and AppLocker – skills that are critical for safeguarding classified Windows environments[1][2]. These abilities are highly relevant for Blue Team roles and positions focused on implementing CIS Critical Security Controls within cleared networks, building on the technical and compliance knowledge discussed earlier.

GIAC certifications are listed as preferred qualifications in thousands of job postings globally, giving hiring managers confidence in a candidate’s technical capabilities[3]. For professionals already working in the field, this certification acts as a trusted credential. Nate Gonzalez, a professional who holds multiple GIAC certifications, shared:

Now that I am certified, I truly see the value of GIAC credentials – they helped me secure my dream role thanks to the skills and knowledge I’ve learned via taking SANS courses and passing GIAC exams

[3].

The GCWN certification is particularly beneficial for transitioning military personnel. Recognized by the U.S. Department of Labor as relevant to military occupational specialties, it helps veterans convert their service experience into civilian roles within cleared contractor environments[5]. Federal agencies officially recommend more than 20 GIAC certifications, including the GCWN, for government and military cybersecurity teams[4].

Although the GCWN is now in abeyance and no longer available for new purchase, current holders retain a competitive edge in the cleared job market by renewing their credentials through Continuing Professional Education (CPE) credits[1][2]. This ongoing certification maintenance ensures professionals remain relevant and well-positioned for career advancement.

Salary and Job Market Impact

The GCWN certification not only broadens career opportunities but also enhances earning potential. As an advanced credential, it signifies that candidates possess over two years of experience and relevant post-secondary education[5]. This makes them eligible for higher-level roles that demand proven expertise in securing Microsoft operating systems within classified environments. Arlin Halstead, Strategic HR Business Partner at NTT Security, highlighted:

The job function specific, technical certification ensures that their employees have proven expertise gained through GIAC certification

[4].

The certification’s emphasis on specialized skills meets critical needs in cleared environments where such expertise is in high demand[1][2]. Professionals who can demonstrate their ability to harden Windows systems are well-positioned for roles with increased responsibilities and higher salaries. By maintaining the certification through CPE credits, individuals continue to enjoy these career and financial benefits over time.

Using GCWN Skills in Cleared Environments

Strengthening Windows Security Systems

GCWN-certified professionals play a critical role in safeguarding cleared environments by leveraging tools like PowerShell and WMI. These tools allow precise management of Active Directory, Group Policy, and permissions – eliminating the risks associated with manual GUI methods and ensuring the integrity of classified networks [1][6].

To harden Windows services, professionals configure Firewall rules, implement IPsec zero-trust policies, and set up audit policies that align with federal logging requirements [1][6]. Additional layers of protection come from deploying AppLocker, Credential Guard, and Just Enough Administration (JEA). Public Key Infrastructure (PKI) management is also used to address multi-factor authentication (MFA), smart card integration, and encryption needs [1][2].

Practical hardening strategies often involve using DISA Security Technical Implementation Guides (STIGs) to create secure baselines for Privileged Access Workstations, which are critical for managing high-value resources like domain controllers [8]. For example, to address vulnerabilities like the "Printer Bug", GCWN professionals use Group Policy Objects (GPOs) to disable the Print Spooler service on domain controllers [9]. Replacing standard service accounts with Group Managed Service Accounts (GMSAs) further enhances security by enabling Active Directory to automatically manage and rotate passwords, reducing the risk of credential theft [9]. Regular audits of Foreign Security Principals in privileged groups and transitioning Kerberos delegation from unconstrained to constrained models are additional steps taken to prevent cross-forest compromises and unauthorized impersonation [9].

These techniques not only secure systems but also demonstrate your technical expertise and problem-solving skills.

Showing Your Value to Employers

Your technical contributions can translate into measurable career advantages. Highlight your GCWN skills by quantifying the impact of your security enhancements – for instance, explaining how implementing JEA reduced administrative exposure or how automating GPO audits identified and resolved misconfigurations. When interviewing, share real-world examples of how you used PowerShell automation to enforce CIS Critical Security Controls or configured IPsec policies to isolate sensitive networks. Employers value professionals who can clearly articulate system improvements and the results of their automation efforts.

On the job, keep your expertise visible by documenting your work and providing training to your team on essential Windows hardening techniques. Sharing your knowledge not only strengthens your team but also reinforces your position as a key contributor.

Conclusion

The GCWN certification showcases your ability to secure Windows systems in environments that handle national security and classified data. While this certification is currently unavailable for new candidates, those who already hold it continue to demonstrate expertise in areas like PowerShell automation, PKI management, and Zero Trust policies [1][2]. These are the exact skills that employers in cleared environments depend on to combat persistent threats and ransomware attacks.

If you’re a current GCWN holder, make sure to earn the required 36 CPEs every four years to keep your certification active [10]. This credential highlights your technical proficiency, making you a standout choice for many job opportunities [3].

The GCWN exam focused on practical Windows hardening skills – such as configuring IPsec policies and deploying AppLocker – ensuring certified professionals are ready to secure cleared networks from day one [1][6].

Your GCWN expertise can directly impact your career growth. As Nate Gonzalez shared, "Trust Me, I’m Certified" rings true – his certification helped him secure his dream job [3]. By documenting your achievements, measuring security improvements, and sharing knowledge with your team, you establish yourself as an invaluable resource in the cleared cybersecurity space. These efforts not only reinforce your position but also pave the way for future career milestones.

Whether you maintain your GCWN or continue expanding your skill set, these capabilities are crucial for safeguarding America’s most sensitive systems and staying ahead in the competitive world of cleared cybersecurity.

FAQs

If GCWN is unavailable, what should I do instead?

If the GCWN certification isn’t an option, look into other GIAC certifications that align with your career aspirations, such as those focusing on cyber defense or security management. Additionally, consider well-regarded cybersecurity credentials from trusted organizations to boost your qualifications. Prioritize certifications that build on your Windows security expertise and contribute to your ongoing professional growth.

How do I keep my GCWN active after 2026?

To keep your GCWN certification active beyond 2026, you’ll need to renew it every four years. This can be done in two ways: earning Continuing Professional Education (CPE) credits or retaking the exam. Be sure to review the certification requirements so you remain in line with the renewal guidelines.

What cleared jobs benefit most from GCWN skills?

Professionals in government, military, and defense roles – particularly those centered on Windows security and system administration – gain the most from GCWN skills. This includes Windows administrators, cybersecurity engineers, and blue team members responsible for managing security tools like PKI, Group Policy, and PowerShell. The GCWN certification not only boosts their credibility but also sharpens their ability to secure and strengthen Windows systems, which is especially critical in sensitive or classified settings. It’s a valuable credential for anyone in these fields.

Related Blog Posts

  • GPEN Certification Career Guide for Cleared Penetration Testers
  • GCIH Certification Career Guide for Cleared Incident Handlers
  • GSEC Certification Career Guide for Cleared Security Essentials
  • GCIA Certification Career Guide for Cleared Intrusion Analysts

Related Guides

  • Cisco CCIE Security Career Guide for Cleared Expert Engineers
  • Cisco CCNP Security Career Guide for Cleared Network Engineers
  • Cisco CCNA Security Career Guide for Cleared Network Professionals
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers
  • « Go to Previous Page
  • Go to page 1
  • Interim pages omitted …
  • Go to page 8
  • Go to page 9
  • Go to page 10
  • Go to page 11
  • Go to page 12
  • Interim pages omitted …
  • Go to page 14
  • Go to Next Page »
  • Facebook
  • Instagram
  • LinkedIn
  • Twitter
  • YouTube

Cleared Cyber Security Jobs | CyberSecJobs.com

  • Contact
  • About
  • Privacy Policy