• Skip to primary navigation
  • Skip to main content
Cleared Cyber Security Jobs | CyberSecJobs.com

Cleared Cyber Security Jobs | CyberSecJobs.com

Cleared Cyber Security Jobs

  • Home
  • Search Cleared Cyber Jobs
  • Job Fairs
  • Career Resources

Certifications

eCPPT Certification Career Guide for Cleared Professional Pen Testers

CyberSecJobs Editorial · February 22, 2026 ·

The eCPPT (eLearnSecurity Certified Professional Penetration Tester) is a hands-on certification tailored for cybersecurity professionals, particularly those in U.S. government and defense roles. It focuses on practical skills like Active Directory penetration testing, privilege escalation, and network pivoting – key abilities for navigating complex, secure environments. Unlike traditional certifications, the eCPPT emphasizes real-world scenarios through a 24-hour simulated penetration test.

Key Takeaways:

  • Who is it for? Professionals with at least 2 years of experience in offensive security, system administration, or security engineering.
  • Exam Focus: Active Directory (30%), exploitation/post-exploitation (25%), web application testing (15%), and more.
  • Format: 24-hour practical test using a restricted Kali Linux instance, with auto-graded results.
  • Cost: $200–$400 for the exam voucher; bundles with training range from $249–$599.
  • Renewal: Requires 36 CPE credits over 3 years; renewal fees are $99 if completed on time.

This certification is especially relevant for cleared penetration testers, as it aligns with the skills required for working in segmented networks and meeting strict documentation standards. It also serves as a stepping stone to higher-paying roles, with salaries for penetration testers ranging from $75,000 to $143,000 or more, depending on experience and location.

Preparation Tips:

  • Use INE’s Penetration Testing Professional (PTP) learning path for structured training.
  • Practice extensively in labs, focusing on Active Directory attacks, privilege escalation, and pivoting techniques.
  • Save offline resources like wordlists, scripts, and notes to simulate the exam’s restricted environment.

The eCPPT is a strong choice for cleared professionals looking to advance their careers in penetration testing or red team operations.

The Ultimate 2025 eCPPT Certification Guide | Hands-On Pentesting, AD Labs & Exam Success

sbb-itb-bf7aa6b

What is eCPPT Certification?
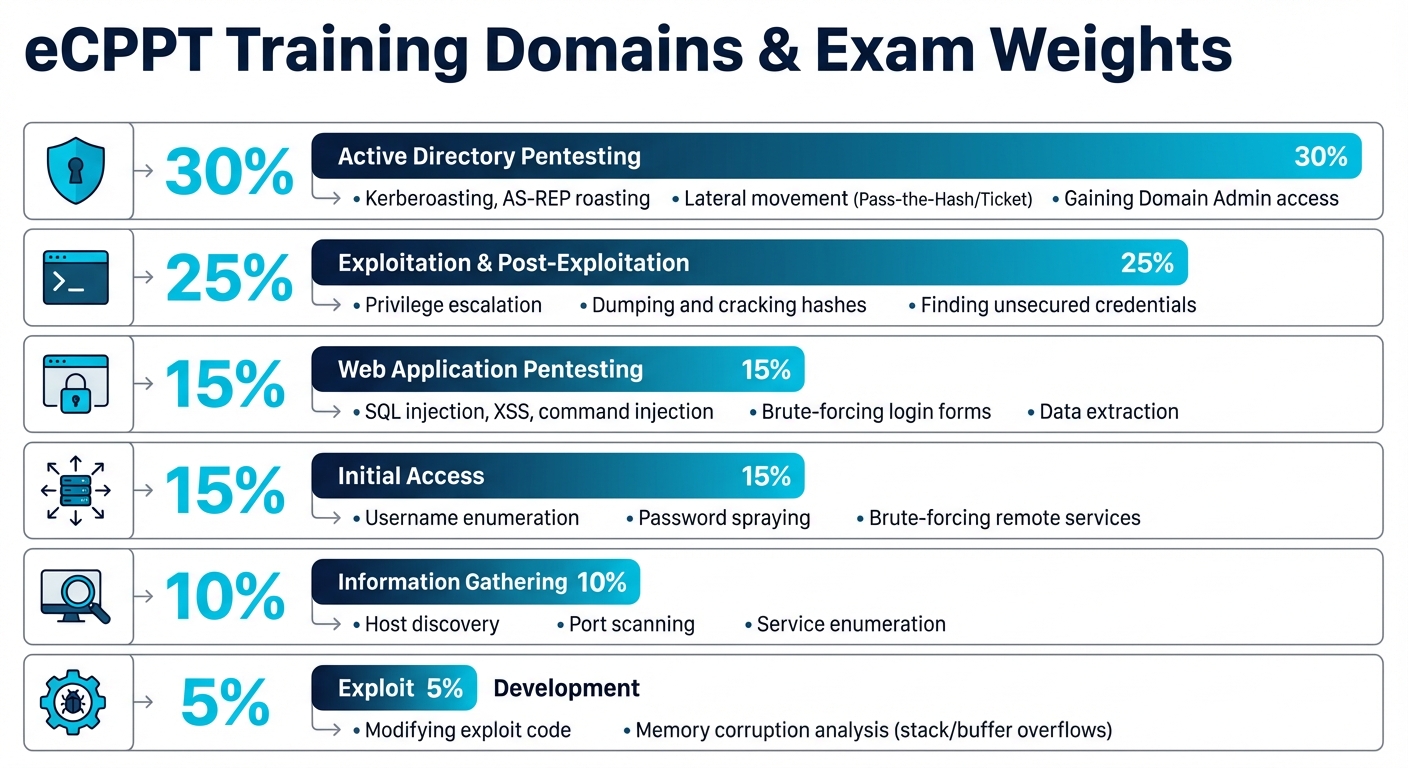
eCPPT Certification Training Domains and Exam Weight Distribution

eCPPT Certification Training Domains and Exam Weight Distribution

The eCPPT (Certified Professional Penetration Tester) is a hands-on certification designed to showcase practical offensive security skills. Unlike traditional certifications that rely on multiple-choice exams, the eCPPT requires candidates to perform simulated, real-world penetration tests. It’s tailored for professionals with at least two years of experience in offensive security, system administration, or security engineering, proving their ability to execute real attacks [1].

The certification remains valid for three years and follows a structured training and testing approach.

eCPPT Training Modules

The eCPPT certification is supported by the Penetration Testing Professional (PTP) learning path, which focuses on six essential domains. These domains are weighted based on their relevance to real-world scenarios. For instance, Active Directory penetration testing carries the most weight at 30% of the exam score, reflecting its importance in modern corporate setups. Exploitation and post-exploitation techniques make up 25%, while web application testing and initial access each account for 15% [1] [4].

Domain Weight Key Skills
Active Directory Pentesting 30% Techniques like Kerberoasting, AS-REP roasting, lateral movement (Pass-the-Hash/Ticket), and gaining Domain Admin access
Exploitation & Post-Exploitation 25% Privilege escalation, dumping and cracking hashes, finding unsecured credentials
Web Application Pentesting 15% Identifying SQL injection, XSS, command injection, brute-forcing login forms, and extracting data
Initial Access 15% Methods such as username enumeration, password spraying, and brute-forcing remote services
Information Gathering 10% Host discovery, port scanning, and service enumeration
Exploit Development 5% Modifying exploit code and analyzing memory corruption (e.g., stack/buffer overflows)

These modules emphasize practice, helping candidates develop "muscle memory" for common attack techniques. Topics like network pivoting, credential abuse, and lateral movement are thoroughly covered, which are especially crucial for navigating segmented networks or restricted environments [4].

Exam Format and Hands-On Testing

The eCPPT exam builds on the training modules, placing candidates in a realistic 24-hour penetration test against a simulated corporate network [4]. Using an in-browser Kali Linux instance with restricted internet access, candidates rely on their offline resources, such as notes, wordlists, and custom scripts. This setup replicates the challenges of secure, offline networks often seen in high-security environments, testing a participant’s ability to adapt under pressure.

In 2024–2025, INE introduced an updated, auto-graded exam system that delivers results within hours instead of weeks [4]. The exam includes 45 multiple-choice questions directly linked to the practical tasks performed during the lab. Instead of submitting a traditional penetration test report, candidates are evaluated on their technical execution in real time. If a candidate doesn’t pass on the first try, most vouchers include a free retake within 14 days, as long as both attempts are within the voucher’s 180-day validity period [4].

The exam cost ranges from $200 to $400 for a standalone voucher. Bundles that include three months of INE Premium access typically range from $249 to $599. To maintain the certification, candidates need to earn 36 continuing professional education (CPE) credits over three years. Renewal fees are $99 if completed before expiration or $199 during a 90-day grace period [4].

Why eCPPT Matters for Cleared Penetration Testers

The eCPPT certification sets you apart in cleared penetration testing roles by focusing on practical, hands-on skills rather than rote memorization. It assesses your ability to simulate real-world attacks on enterprise networks – systems commonly used by government agencies and defense contractors. This makes the certification directly relevant to the challenges faced in cleared roles, where understanding and navigating complex infrastructure is critical.

How eCPPT Meets Cleared Job Requirements

Cleared penetration testing jobs demand expertise in handling segmented networks and exploiting Active Directory systems, both of which are core components of the eCPPT curriculum. The certification dives deep into areas like Kerberos abuse, lateral movement techniques, and achieving Domain Admin access – skills essential for working with federal networks [1][4].

The exam emphasizes practical post-exploitation skills, including:

  • Privilege escalation
  • Credential abuse
  • Navigating restricted network segments

These competencies are crucial for tasks like assessing segmented defense networks or performing internal red team operations. The hands-on nature of the eCPPT exam mirrors the conditions penetration testers face in real scenarios.

"The certification exam assesses and validates that the individual has the knowledge, skills, and abilities required to fulfill the role of a modern Penetration Tester." – INE [1]

Additionally, the certification ensures that candidates master clear and actionable reporting, meeting the rigorous documentation standards required in federal environments [2].

Career Benefits for Cleared Professionals

The eCPPT certification enhances your career prospects in the cleared job market by validating skills that directly translate to higher earning potential. Entry-level penetration testers earn between $75,000 and $95,000, while seasoned professionals with advanced certifications can surpass $120,000 annually [5]. The certification’s three-year validity and requirement for 36 Continuing Professional Education (CPE) credits ensure that your skills remain relevant as threats evolve.

For many professionals, the eCPPT serves as a stepping stone from foundational certifications like Security+ to more advanced credentials. Its focus on Active Directory and internal network exploitation complements other offensive security certifications, creating a well-rounded skill set that appeals to government contractors.

"If you’re pursuing roles involving internal assessments, red teaming, or consulting on enterprise risk, eCPPT’s skill map aligns perfectly with what those jobs demand." – FlashGenius [4]

The updated exam format, introduced in 2024–2025, delivers results within hours instead of weeks. This quick turnaround allows candidates to demonstrate their technical skills promptly – an advantage when applying for cleared positions that require proof of current expertise. These streamlined processes and practical benefits underscore eCPPT’s value in advancing careers in the cleared penetration testing field.

How to Prepare for eCPPT Certification

Preparing for the eCPPT certification requires a focused, hands-on strategy that mirrors secure network conditions. This exam isn’t about rote memorization – it’s about practical skills. With its 24-hour, single-sitting format, success hinges on muscle memory built through extensive lab work. You’ll need to execute attacks under time pressure, with limited internet access, in a controlled environment.

Study Materials and Resources

The INE Penetration Testing Professional (PTP) Learning Path is the go-to resource, designed to align directly with the exam. An INE Premium subscription costs about $749 per year, offering full access to labs and materials. If you’re on a tighter budget, the Fundamentals Plan at $299 per year provides essential content. Exam vouchers alone range from $200 to $400, and promotional bundles combining the voucher with three months of Premium access typically cost between $249 and $599.

To complement INE’s materials, consider these additional resources:

  • HackTheBox Academy’s "Active Directory Enumeration & Attacks" module to sharpen your AD-related skills.
  • The PortSwigger Web Security Academy, which provides excellent practice for web vulnerabilities like SQL injection and command injection.
  • TryHackMe’s "Wreath" room, offering realistic pivoting scenarios similar to the exam environment.

Since the exam limits internet access, prepare an offline workflow. Save essential wordlists (like rockyou.txt and seasons.txt), custom scripts, and cheatsheets locally. Ensure you’re proficient with tools like OpenVPN for lab access, Metasploit for exploitation, and Nmap for reconnaissance. These tools will form the backbone of your toolkit during the exam.

Once your resources are ready, shift your focus to intensive lab practice to build the necessary hands-on experience.

Hands-On Practice Tips

Practical lab work is critical for mastering the eCPPT exam environment. Dedicate more time to labs than to reading. Set up a local Active Directory lab using virtual machines to practice techniques like Kerberoasting, AS-REP roasting, and delegation abuse. Repeated practice with these scenarios will help you navigate internal network segments more efficiently.

"Reading is not enough. You must log hours in the lab to develop the muscle memory required for success." – FlashGenius [4]

Simulate the exam by conducting a 24-hour mock test using only approved tools. Practice your "first-90-minute workflow", focusing on reconnaissance, gaining a foothold, and privilege escalation. Mastering time management during this phase is key. Additionally, practice setting up SOCKS proxies and routing, as navigating segmented networks is a crucial skill.

Effective note-taking can make or break your exam performance. Keep detailed records of hosts (IP addresses, domains, operating systems), credentials (usernames, passwords, domain statuses), and scan results. Organize this information in tables to track progress. Tools like Screenpresso can help you capture findings quickly during the exam. Even though the exam includes auto-grading, maintaining detailed command logs ensures you don’t overlook critical flags.

"One of many reasons that made me succeed the exam was proper note-taking, it is crucial to pass the exam and without that there is a big risk of failure!" – Str4ngerX [6]

For buffer overflow preparation, use TryHackMe’s "Buffer Overflow Prep" rooms or set up a Windows VM with Immunity Debugger and mona.py. While the official course covers exploit development, these additional resources can fill in any gaps. Also, keep a persistent ping running to the exam webserver to avoid VPN disconnections during critical moments – this simple step can save you from unnecessary frustration.

These targeted practices not only prepare you for the eCPPT exam but also sharpen the skills you’ll need for real-world, high-security environments.

How to Pass the eCPPT Exam as a Cleared Professional

The eCPPT’s intense 24-hour, single-sitting format is designed to simulate high-pressure, real-world scenarios. Success requires a mix of precise time management, sharp technical skills, and strict adherence to security protocols.

Managing the 24-Hour Exam Window

Since the exam is auto-graded, there’s no traditional reporting phase, meaning you’ll need to maximize every minute. Active Directory pentesting is the heaviest scoring section at 30%, followed by Exploitation and Post-Exploitation at 25% each[4]. These weightings should guide how you allocate your time. A possible breakdown could look like this:

  • First 90 minutes: Focus on recon and gaining an initial foothold.
  • 8–10 hours: Dedicate to Active Directory enumeration and lateral movement.
  • 6–8 hours: Work on privilege escalation.
  • 2–3 hours: Wrap up with verification and cleanup.

"Optimize your first-90-minute workflow: recon → foothold → privilege escalation → DA." – FlashGenius[4]

If you hit a wall with credential brute-forcing, don’t waste more than 30 minutes on wordlist attacks. Instead, pivot to alternative enumeration methods[6]. Many candidates have completed the exam in about 19 hours, even with breaks[6]. Scheduling short rest periods can help maintain focus and avoid burnout.

These time management strategies not only help you succeed in the exam but also align with the structured workflows required in secure environments.

Compliance Considerations for Cleared Environments

The eCPPT exam emphasizes manual techniques, reflecting the precision and understanding needed in cleared environments. While automated tools can save time, the exam – and your future roles – focus on knowing the "why" behind every command. This approach minimizes noise, reduces risk, and ensures careful execution in sensitive networks[7].

The exam is delivered through a browser-based interface using Apache Guacamole, which introduces unique challenges for cleared professionals[7]. Before starting, coordinate with your security team to secure any necessary authorizations for network access if you’re working from a secured facility. The restricted exam environment, with limited tools and no internet access, mirrors the conditions of air-gapped or highly controlled networks often encountered in cleared roles[4].

To prepare, build an offline repository of critical techniques – such as pivoting methods, buffer overflow approaches, and Active Directory attack workflows. Storing these in formats like PDFs or Obsidian vaults can be a game-changer in environments where internet access is restricted[3][2]. This habit not only supports exam success but also equips you for the challenges of working in tightly controlled operational settings.

Using eCPPT to Advance Your Cleared Career

The eCPPT certification can be a game-changer for anyone looking to grow in the fast-paced world of cybersecurity. According to the U.S. Bureau of Labor Statistics, demand for information security analysts, including penetration testers, is projected to grow by 33% between 2023 and 2033[9]. With cybercrime costs expected to exceed $10 trillion annually by 2025, organizations are on the hunt for professionals who don’t just know the theory but can demonstrate real-world offensive security skills[10].

This demand also translates into impressive earning potential. As of July 2025, penetration testers in the U.S. earn an average salary of $143,000, with even higher pay in cleared hubs. For example, McLean, VA leads with $169,897, followed by Chantilly, VA at $150,546, and Arlington, VA at $130,274[9].

The eCPPT certification stands out because of its hands-on approach. It validates your ability to perform tasks like compromising hosts, navigating network pivots, and escalating privileges in enterprise environments. For cleared employers, this practical expertise is invaluable, especially for roles requiring immediate operational readiness in red team operations and internal security assessments[4].

Finding Jobs with Cleared Cyber Security Jobs
Cleared Cyber Security Jobs

Once you’ve earned your eCPPT, the next step is finding the right job to match your skills. Cleared Cyber Security Jobs is a platform designed specifically for professionals with security clearances. It connects you with employers who value certifications like the eCPPT. The platform offers tools like job search filters to help you find roles that align with your clearance level and technical expertise. You can also upload your resume, set up alerts for penetration testing positions, and access resources tailored to the cleared workforce.

Another standout feature is the platform’s job fairs, where you can meet hiring managers directly – no intermediaries like staffing firms or third-party recruiters. For eCPPT holders, this is a golden opportunity to showcase your hands-on skills during conversations with employers who understand the certification’s technical depth. Best of all, these services are free for job seekers, though participation requires U.S. citizenship and an active security clearance.

Combining eCPPT with Other Certifications

To maximize its impact, the eCPPT works best when paired with other certifications. For instance, CISSP highlights your knowledge of security management, while CEH covers foundational ethical hacking concepts. The eCPPT complements these by proving you can execute sophisticated, real-world attacks. Together, they present a well-rounded skill set that balances strategic understanding with tactical expertise[4][8].

For cleared roles tied to the Defense Cyber Workforce Framework (DCWF), combining eCPPT with CompTIA Pentest+ is a strong move. While Pentest+ often meets DoD 8570 baseline requirements, the eCPPT demonstrates advanced skills like Active Directory exploitation and network pivoting, essential for high-level enterprise assessments[4][8][11]. If you’re transitioning from defensive roles such as SOC analysis or network engineering, this certification stack highlights your ability to operate effectively in both offensive and defensive capacities[5].

"The eCPPT certification stands out for its realism, efficiency, and focus on the technical depth that modern penetration testers need." – FlashGenius[4]

Conclusion

The eCPPT certification provides a practical, hands-on way to prove your skills in the cybersecurity field, especially within the cleared workforce. Unlike exams focused solely on theory, this certification shows you can perform real-world tasks – like exploiting Active Directory and network pivoting – in environments that closely resemble enterprise and government systems. This level of hands-on experience sets you up for success in demanding, high-pressure environments.

To make the most of your certification, take proactive steps to showcase your skills. Use platforms like Cleared Cyber Security Jobs to connect with hiring managers who value the technical expertise demonstrated by the eCPPT. Set up job alerts, attend job fairs, and emphasize your practical experience in your applications. Remember, your certification is valid for three years and requires 36 CPE credits for renewal [4]. Alternatively, you can aim for advanced certifications like OSCP or eWPT to further enhance your credentials.

Leverage the preparation strategies outlined in this guide to highlight your expertise. Build a polished, sanitized portfolio on platforms like GitHub or LinkedIn to showcase your projects and lab work. Regular lab practice will ensure your skills stay sharp and relevant.

"The eCPPT was well worth the time invested into it and I still occasionally reference my notes on my client engagements." – Jake Murphy, Offensive Security Team, Echelon Risk + Cyber

This certification demonstrates your ability to perform under pressure, navigate complex systems, and deliver the expertise that cleared employers are looking for.

FAQs

Is eCPPT accepted for DoD 8570/DCWF roles?

The eCPPT certification holds recognition under the DoD 8570 framework, making it valid for specific roles, including those at management and CSSP (Cybersecurity Service Provider) levels. Additionally, it aligns with the broader directives outlined in DoD 8140, ensuring its relevance for various essential job roles within the DCWF (DoD Cyber Workforce Framework).

What offline files should I bring to the exam?

While there aren’t any mandatory offline files for the eCPPT exam, it’s a good idea to come prepared with backups of your virtual machines, tools, documentation, and any binaries or scripts you plan to use. Double-check that your setup is complete and accessible before the exam begins. Having everything ready and backed up can make a big difference in ensuring a smooth experience.

How should I pace the 24-hour exam?

Starting the 24-hour eCPPT exam in the early afternoon can set you up for success. This timing allows you to work during peak alertness and still have flexibility for rest later. Time management is crucial – divide your focus across the exam’s domains, prioritizing areas like Active Directory penetration testing, which accounts for a significant 30% of the exam, and exploitation tasks.

Short breaks are essential to stay sharp, but keep them brief to avoid losing momentum. Fuel your focus with snacks and stay hydrated throughout the process. Reserve some time at the end to thoroughly review your work, ensuring no critical details are missed.
Related Blog Posts

  • PenTest Plus Certification Career Guide for Cleared Pen Testers
  • LPT Certification Career Guide for Cleared Pen Test Leads
  • PNPT Certification Career Guide for Cleared Practical Pen Testers
  • eJPT Certification Career Guide for Cleared Junior Pen Testers

Related Guides

  • CRTL Certification Career Guide for Cleared Red Team Leads
  • CRTO Certification Career Guide for Cleared Red Team Operators
  • CRTP Certification Career Guide for Cleared Red Team Professionals
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

eJPT Certification Career Guide for Cleared Junior Pen Testers

CyberSecJobs Editorial · February 21, 2026 ·

The eJPT (eLearnSecurity Junior Penetration Tester) certification is a hands-on, entry-level credential designed to validate penetration testing skills. It’s ideal for professionals in government or defense sectors with security clearances, as it focuses on practical techniques like network penetration, auditing, and web application testing. The exam costs $249, includes three months of training, and is valid for three years.

Key Highlights:

  • Exam Structure: 48-hour, open-book, browser-based test with 35–45 questions.
  • Domains Covered:
    • Host & Network Penetration Testing (35%)
    • Assessment Methodologies (25%)
    • Host & Network Auditing (25%)
    • Web Application Penetration Testing (15%)
  • Study Resources: INE’s Penetration Testing Student (PTS) course (153 hours, 108 labs).
  • Tools to Master: Nmap, Metasploit, Burp Suite, and pivoting techniques.

The certification is a stepping stone to more advanced credentials (e.g., eCPPT, OSCP) and aligns well with the growing demand for penetration testers. It also helps cleared professionals transition into offensive security roles or advance their careers.


This guide explains how the eJPT equips you with practical penetration testing skills, prepares you for cleared cybersecurity roles, and boosts your career prospects in a growing field.

The Definitive 2026 eJPT Certification Guide | Pass the eLearnSecurity Penetration Tester Exam

eLearnSecurity

sbb-itb-bf7aa6b

eJPT Exam Structure and Content Areas

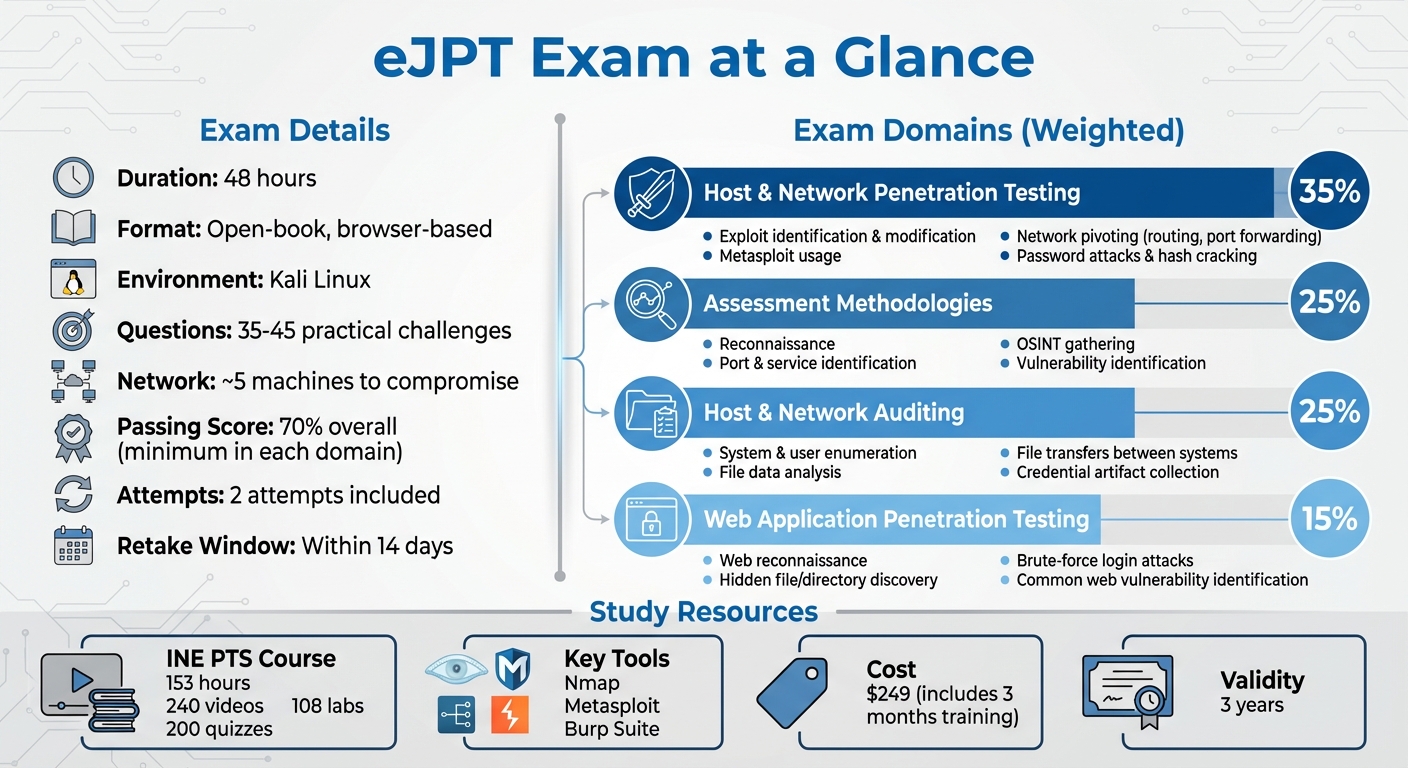
eJPT Certification Exam Structure and Domain Breakdown

eJPT Certification Exam Structure and Domain Breakdown

Exam Format and Key Details

The eJPT exam is a hands-on, open-book test conducted entirely within a browser-based Kali Linux environment. You’ll navigate a simulated network of around five machines, tackling tasks like enumeration, exploitation, pivoting, and privilege escalation to complete 35 practical challenges[6]. The focus here is on applying penetration testing skills rather than memorizing facts.

"Rather than questions designed to test how well you have memorized information, these questions assess your ability to actively perform the tasks and processes of a Junior Penetration Tester." – The INE Team[6]

To pass, you need an overall score of at least 70%, with minimum requirements in each of the four domains. Your exam voucher includes two attempts, but if you fail, the retake must be used within 14 days[8]. The exam also employs dynamic and static flagging technologies to ensure a unique experience for every candidate[6].

Understanding this practical format is essential to navigating the exam’s weighted content areas effectively.

Core Domains of the eJPT Exam

The exam evaluates your skills across four key domains, each weighted according to its importance in penetration testing:

  • Host and Network Penetration Testing (35%)
    This domain focuses on tasks like identifying and modifying exploits, using tools such as Metasploit, pivoting through networks with routing and port forwarding, conducting password attacks, and cracking hashes[6].
  • Assessment Methodologies (25%)
    Here, you’ll demonstrate your ability to perform reconnaissance, which includes locating endpoints, identifying ports and services, OS fingerprinting, gathering open-source intelligence (like emails or technical details), and spotting vulnerabilities[6].
  • Host and Networking Auditing (25%)
    This section assesses your skill in enumerating system and user information, analyzing target file data, transferring files between systems, and collecting credential artifacts[6].
  • Web Application Penetration Testing (15%)
    Focused on web reconnaissance, this domain involves finding hidden files and directories, performing brute-force login attacks, and identifying common web vulnerabilities[6].

A strong grasp of pivoting techniques, such as adding routes and using port forwarding, is critical to accessing all targets during the exam[2].

How to Prepare for the eJPT Exam as a Cleared Professional

Prerequisites and Study Resources

The Penetration Testing Student (PTS) learning path from INE is your main resource for exam preparation. This comprehensive course includes 240 videos, 200 quizzes, and 108 labs, adding up to 153 hours of material[2].

"Everything you need to pass the eJPT exam is covered in the Penetration Testing Student (PTS) learning path on INE." – Lily Clark, Client Success Representative, INE[9]

For additional practice, TryHackMe provides a great platform for around $10/month. Rooms such as "Basic Pentesting", "RootMe", and "Simple CTF" are particularly useful for sharpening your skills with tools like Nmap, Burp Suite, and Metasploit[9]. To further enhance your learning, John Hammond’s YouTube channel offers practical demonstrations of Linux workflows and penetration testing techniques, making it an excellent complement to your formal studies.

Once you’ve gathered these resources, the next step is to create a structured and achievable study plan.

Creating a Study Plan

Given the 153 hours of course material and your professional obligations, a well-thought-out study schedule is key. Use SMART goals (Specific, Measurable, Achievable, Relevant, and Time-bound) to divide your study time into manageable chunks that fit around your work and clearance responsibilities[9]. Tools like Google Sheets can help you map out study sessions while keeping track of work deadlines and personal commitments, reducing the risk of burnout.

"For each lab you do, create a report for yourself that includes common commands for the tool or technique you are learning… Do this for every lab." – Lily Clark, Client Success Representative, INE[9]

Structure your study sessions around the exam’s core areas: Host and Network Penetration Testing (35%), Assessment Methodologies (25%), Host and Network Auditing (25%), and Web Application Penetration Testing (15%)[5][6]. If you encounter a challenging concept, keep moving through the material – hands-on labs will help reinforce your understanding over time.

Once your study plan is in place, it’s time to focus on mastering the tools and techniques.

Tools and Practice Labs

Proficiency with the tools highlighted in the Host and Network Penetration Testing and Web Application Testing sections is essential. The exam’s browser-based lab environment eliminates the need for complex installations, but you should still focus on the "Big Three" tools: Nmap for reconnaissance, Metasploit for exploitation, and Burp Suite for web application testing[9]. Practice pivoting techniques, such as adding routes and port forwarding, to navigate scenarios effectively during the exam[2].

Document your lab work thoroughly. Use note-taking tools like CherryTree or Obsidian to organize key commands and screenshots by exam domains[4]. This documentation becomes an invaluable reference during the 48-hour exam period.

Using eJPT Skills in Cleared Cybersecurity Roles

Practical Applications in Penetration Testing

The skills covered in the eJPT certification are not just exam material – they translate directly into tasks you’ll encounter in cleared cybersecurity roles.

For example, the certification teaches network traversal and pivoting, essential techniques for navigating segmented networks in classified environments [1]. Many classified systems are divided into isolated enclaves, requiring you to add routes and use port forwarding to move laterally through these restricted zones.

Another critical area is vulnerability identification and exploitation. The eJPT validates your ability to pinpoint vulnerabilities in services and web applications, assess their severity, and exploit them using tools like Metasploit [1]. In cleared roles, this means you’ll be responsible for evaluating internal systems, identifying weaknesses, and creating detailed reports that meet government documentation standards [8].

The certification also emphasizes enumeration skills – gathering system information, user accounts, and network details – which is vital for internal security audits [1]. These audits ensure compliance with security protocols and help detect unauthorized access points within sensitive environments.

These technical capabilities don’t just make you more effective – they also build the confidence needed to tackle the challenges of cleared cybersecurity work.

Building Confidence in Cleared Workflows

The eJPT doesn’t just teach technical skills; it also helps you develop a workflow that mirrors real-world penetration testing scenarios.

The hands-on 48-hour lab environment of the exam is designed to simulate actual testing conditions. You’ll practice documenting technical findings with evidence [8], a skill directly applicable when preparing vulnerability reports for security officers or program managers in cleared operations.

"The eJPT is more than a certification – it’s a confidence builder. Whether you’re aiming for a career in ethical hacking or want to understand better how networks are attacked and defended, passing this exam will open doors." – Evan Isaac, Lead Technical Writer [2]

Through the eJPT, you’ll refine a methodical approach that starts with reconnaissance and progresses through exploitation to detailed reporting. This structured framework ensures you can systematically identify live endpoints, open ports, and services [1]. By reducing guesswork, it helps you focus on uncovering critical vulnerabilities without overlooking key details.

Using eJPT for Career Growth on Cleared Cyber Security Jobs

Highlighting Your Certification on Cybersecjobs.com

Cybersecjobs.com

The eJPT certification can significantly enhance your visibility on Cleared Cyber Security Jobs – especially when highlighted effectively. This 48-hour practical exam mirrors real-world scenarios [2][7], making it stand out compared to theory-heavy credentials.

To maximize its impact, emphasize the four key domains it covers: Host and Network Penetration Testing, Assessment Methodologies, Host and Network Auditing, and Web Application Penetration Testing. These terms are often used by recruiters searching for junior penetration testers, so including them in your profile can boost your chances of being noticed. Additionally, list tools like Metasploit, Nmap, and Hashcat in your skills section, and mention your expertise in pivoting (such as adding routes and port forwarding). This demonstrates your ability to navigate segmented networks – an essential skill for classified environments with complex internal infrastructures.

In your profile summary, describe the eJPT as a practical, hands-on certification. This phrasing appeals to hiring managers who prioritize technical skills over theoretical knowledge. Also, highlight your ability to produce detailed technical reports, which aligns with the workflow standards in cleared environments.

Once your certification is prominently displayed, ensure your technical skills align with employer expectations for cleared cybersecurity roles.

Matching eJPT Skills with Employer Requirements

Employers value candidates who showcase both certifications and real-world skills like OSINT, vulnerability identification, and exploitation. The eJPT aligns perfectly with these needs, making it a strong asset for cleared penetration testing roles. With penetration testing jobs expected to grow by nearly 35,000 positions by 2031 [3], and junior penetration testers earning an average salary of $87,105 [3], the certification positions you for a growing field with competitive pay.

When applying through Cleared Cyber Security Jobs, reference your eJPT skills in your resume and cover letter. Highlight its focus on the entire penetration testing lifecycle – from reconnaissance to exploitation and reporting. This shows that you not only understand technical methodologies but also possess the practical expertise required for government and defense sector roles.

The eJPT also serves as a gateway to more advanced certifications like the eCPPT or OSCP, which are often prerequisites for mid-to-senior-level cleared positions. By presenting the eJPT as a foundational step in your career journey, you demonstrate a commitment to professional development and readiness to tackle more complex security challenges in the future.

Conclusion

The eJPT certification offers a practical and respected credential for entry-level penetration testers, especially those pursuing opportunities in government or defense sectors. With demand increasing in this competitive field [3], earning this certification can help set you apart and pave the way for career growth.

The certification’s hands-on focus delivers clear career advantages. As Evan Isaac, Lead Technical Writer at MRE Security, explains:

"The eJPT is more than a certification – it’s a confidence builder. Whether you’re aiming for a career in ethical hacking or want to understand better how networks are attacked and defended, passing this exam will create career opportunities" [2].

Affordable and accessible, the eJPT also serves as a stepping stone toward more advanced certifications like the eCPPT or OSCP.

To make the most of this opportunity, craft a study plan targeting the four core areas – Host and Network Penetration Testing, Assessment Methodologies, Host and Network Auditing, and Web Application Penetration Testing. Practice essential techniques like pivoting and thoroughly document your work to highlight your skills on your professional profile.

The eJPT equips you with the practical abilities that matter most in this field, providing the perfect starting point for your journey as a penetration tester.

FAQs

How hard is the eJPT exam for beginners?

The eJPT exam is tailored for beginners, emphasizing hands-on, entry-level skills. With the right preparation – like completing the suggested coursework and practicing tools such as Nmap – many candidates find it approachable. Key areas to focus on include information gathering, vulnerability assessment, and basic exploitation techniques. While having some technical background can be helpful, the exam’s practical format and clear-cut questions make it a solid starting point for newcomers who are committed to consistent study.

What should I practice most before the eJPT?

To excel in penetration testing, it’s crucial to focus on applying core methodologies effectively. This includes mastering information gathering, vulnerability assessment, exploitation, and post-exploitation techniques. These steps form the backbone of any successful penetration test.

Key skills to develop include:

  • Using tools like Nmap: Learn to map networks, identify open ports, and gather essential details about target systems.
  • Web application testing: Understand how to uncover vulnerabilities in web applications, such as SQL injection or cross-site scripting (XSS).
  • Leveraging Metasploit: Gain expertise in using this powerful framework for exploit development and post-exploitation activities.

Beyond tools, practice is everything. Spend time identifying and modifying exploits, conducting host and network audits, and working through real-world scenarios. This hands-on experience helps bridge the gap between theory and application.

Don’t overlook the importance of hands-on labs. Familiarity with the exam’s practical environment can make a significant difference. These labs allow you to simulate realistic attack scenarios, giving you the confidence and skills needed for success.

How can eJPT help me get cleared pen test work?

The eJPT certification showcases your practical abilities and core understanding of offensive security, making it a strong credential for entry-level penetration testing positions. It focuses on key areas such as assessment techniques, host and network auditing, and testing web applications.

By earning this hands-on certification, you demonstrate to employers that you can effectively identify vulnerabilities and perform penetration tests. This is especially valuable for roles in sensitive cybersecurity environments, where proven skills are essential.

Related Blog Posts

  • GPEN Certification Career Guide for Cleared Penetration Testers
  • PenTest Plus Certification Career Guide for Cleared Pen Testers
  • LPT Certification Career Guide for Cleared Pen Test Leads
  • PNPT Certification Career Guide for Cleared Practical Pen Testers

Related Guides

  • CRTL Certification Career Guide for Cleared Red Team Leads
  • CRTO Certification Career Guide for Cleared Red Team Operators
  • CRTP Certification Career Guide for Cleared Red Team Professionals
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

PNPT Certification Career Guide for Cleared Practical Pen Testers

CyberSecJobs Editorial · February 21, 2026 ·

The PNPT certification from TCM Security is a hands-on credential tailored for penetration testers, especially those in security-cleared roles. It stands out by simulating a complete penetration test, including OSINT, Active Directory exploitation, and professional reporting. The exam spans seven days: five for testing and two for report writing, culminating in a live debrief. Recognized by organizations like the NSA and U.S. Air Force, the PNPT equips professionals with practical skills aligned with government and defense environments.

Key Highlights:

  • Exam Format: Seven days (5 days testing, 2 days report writing, 15-minute live debrief).
  • Focus Areas: OSINT, Active Directory exploitation, bypassing security defenses, professional-grade reporting.
  • Cost: $499 (includes training access and one retake); discounts for veterans, students, and military personnel.
  • Relevance: Widely recognized by federal agencies and contractors like Booz Allen Hamilton and Peraton.
  • Preparation: Includes 12 months of training materials and access to a supportive community.

This certification is ideal for those seeking to validate their penetration testing expertise in high-security environments while showcasing professional communication skills.

How to Pass Your PNPT in 22 Minutes (2025)

sbb-itb-bf7aa6b

What is the PNPT Certification?

PNPT Certification Exam Format: 7-Day Timeline and Requirements

PNPT Certification Exam Format: 7-Day Timeline and Requirements

The Practical Network Penetration Tester (PNPT) certification, offered by TCM Security, is a hands-on, vendor-neutral credential designed for professionals. Unlike traditional multiple-choice exams, this certification requires candidates to complete a practical penetration test, which includes tasks like network scanning, exploiting vulnerabilities, compromising Active Directory, and delivering a professional debrief.

PNPT Overview and Focus Areas

The PNPT stands out by prioritizing professional deliverables over gamified challenges. There are no "flags to capture" or CTF-style tasks. Instead, the focus is on creating a client-ready penetration testing report and presenting a live debrief. This debrief explains your findings, their impact on the business, and your remediation recommendations. As Josh Daniels from TCM Security puts it, “If your report does a poor job of conveying what you found, it’s as if those parts of the test never happened.” [3]

Given that nearly 90% of Fortune 1000 companies use Active Directory environments [3], this certification equips you to work in real-world enterprise settings. You’re free to use any professional tools during the process.

PNPT Exam Format and Requirements

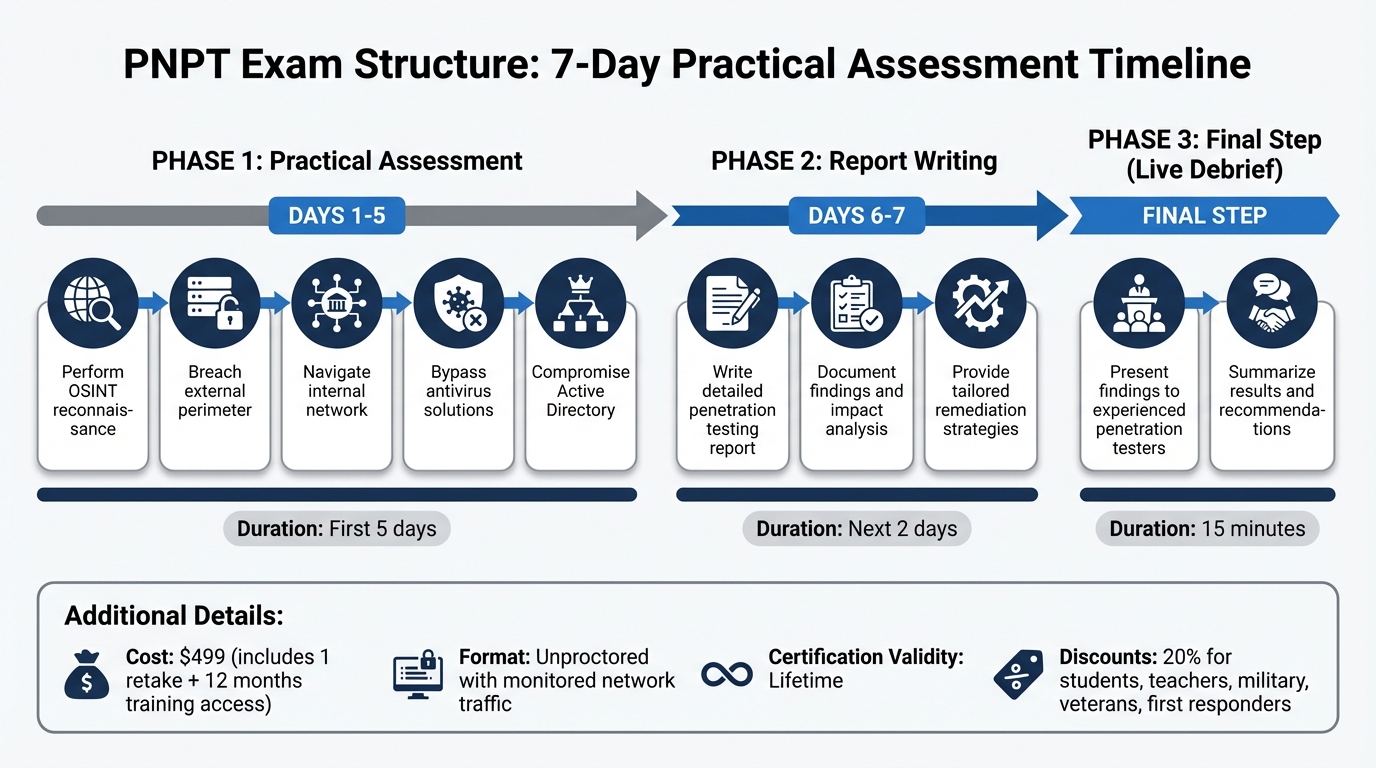
The exam spans seven days and is divided into three phases:

  • Phase 1 (First Five Days): Conduct the practical assessment. This involves performing OSINT, breaching the external perimeter, navigating the internal network, bypassing antivirus solutions, and compromising Active Directory.
  • Phase 2 (Next Two Days): Write a detailed penetration testing report. This report should include your findings, an analysis of their impact, and tailored remediation strategies.
  • Phase 3 (Final Step): Present a 15-minute live debrief to experienced penetration testers, summarizing your results and recommendations.

The exam is unproctored but uses monitored network traffic to maintain integrity, closely mimicking real-world scenarios.

For $499, the certification voucher includes one retake and 12 months of access to over 45 hours of training. This training covers topics like Practical Ethical Hacking, OSINT Fundamentals, Windows and Linux Privilege Escalation, and the External Pentest Playbook. Additionally, TCM Security offers a 20% discount for students, teachers, military personnel, veterans, and first responders. Once you earn the PNPT certification, it remains valid for life.

This hands-on approach not only evaluates your technical expertise but also prepares you for advanced roles in penetration testing, especially in environments requiring high-level clearance.

PNPT Skills for Cleared Penetration Testing Jobs

Core Skills Tested by PNPT

The PNPT certification evaluates a complete penetration testing process designed to reflect the challenges faced in government and defense contracts. It tests your ability to perform OSINT reconnaissance, allowing you to map out attack paths before interacting with the target network. From there, you’ll demonstrate how to breach external defenses and navigate internal systems. A major focus is placed on Active Directory exploitation techniques, including Kerberoasting, AS-REP roasting, BloodHound analysis, and pass-the-hash attacks. Since Active Directory is widely used in large enterprises [3], mastering these techniques is crucial for real-world scenarios.

Another critical component is proving your ability to bypass security defenses while maintaining domain persistence – skills that are indispensable when working in highly secured environments. What sets PNPT apart is its emphasis on professional deliverables, requiring candidates to produce a detailed report and conduct a 15-minute live debrief. As Daniel Pizarro from Black Hills Information Security highlights, "The PNPT certification sets itself apart from most offensive certifications by emphasizing the report quality and the post-engagement debrief" [8].

During the exam, you’ll have unrestricted access to professional tools like Nmap, Burp Suite, BloodHound, Impacket, and Metasploit [2]. These tools and techniques are directly applicable to the types of challenges you’ll face in cleared environments.

Applying PNPT Skills in Cleared Environments

The skills validated by the PNPT exam align perfectly with the demands of cleared penetration testing roles. Its five-day practical assessment mirrors the typical one-week timeline for penetration testing in government and corporate contracts [3][5]. You’ll gain experience in every stage of an engagement, from scope verification and establishing Rules of Engagement to delivering final reports and stakeholder communication. This end-to-end workflow ensures compliance with security protocols during active testing in sensitive defense networks [9].

The certification has gained traction among major organizations, appearing in job postings and being adopted by penetration testing teams at the National Security Agency, U.S. Air Force, Booz Allen Hamilton, and Peraton [2][3]. Josh Daniels from TCM Security explains, "The goal is for certified students to be trained, experienced, and ready on day one to take on the technical responsibilities of a penetration tester, giving PNPT holders and hiring managers confidence in their abilities" [3].

Skills like identifying leaked credentials through OSINT, evaluating endpoint security controls, and effectively communicating vulnerabilities to non-technical stakeholders are directly relevant to cleared environments. The live debrief component, in particular, prepares you to present findings to government clients and leadership – a critical skill for thriving in these roles.

Career Advantages of PNPT for Cleared Professionals

PNPT’s Impact on Cleared Job Prospects

The PNPT certification aligns perfectly with what cleared employers are looking for: proof that you can hit the ground running. Unlike certifications that rely on rote memorization or gamified simulations, the PNPT requires a five-day, real-world engagement that mirrors the challenges of working with actual clients. This practical experience helps close the gap in cleared penetration testing roles.

It’s not just theory – defense contractors and federal agencies have taken notice. Companies like Peraton, Booz Allen Hamilton, the National Security Agency, and even the U.S. Air Force have either included PNPT in their job requirements or provided it to their penetration testing teams [3].

Another key strength of PNPT is its focus on Active Directory (AD). With about 90% of Fortune 1000 companies using AD environments [3], and government networks leaning heavily on these systems, this expertise is a major asset. The certification validates your ability to perform tasks like lateral movement and domain compromise, backed by your exam report and live debrief. This hands-on validation directly meets the demands of cleared environments.

Why Employers Prefer PNPT-Certified Candidates

The PNPT certification offers employers something more than just a checkbox – it provides confidence in a candidate’s readiness. Cleared employers value the PNPT because it confirms a full range of skills necessary for government contracting roles. The certification’s emphasis on producing a professional-grade report and delivering a 15-minute live debrief sets it apart. Daniel Pizarro from Black Hills Information Security highlights this distinction:

"The PNPT certification sets itself apart from most offensive certifications by emphasizing the report quality and the post-engagement debrief" [8].

This requirement mirrors the high-pressure briefings professionals often deliver to government stakeholders and cleared officials.

Additionally, the tools you’ll use during the PNPT exam – Nmap, Metasploit, BloodHound, and Impacket – are the same ones used in real-world cleared environments. The certification allows unrestricted use of these tools, ensuring your skills are tested in realistic scenarios rather than artificial challenges [2].

For veterans and transitioning military personnel, the certification is especially accessible. TCM Security, a veteran-owned company, offers the PNPT certification bundle for $499, with a 20% discount for veterans and military-affiliated professionals [1] [4]. This makes it an appealing option for those looking to transition into cleared roles while gaining hands-on experience that directly aligns with operational needs.

How to Prepare for the PNPT Exam

PNPT Prerequisites and Eligibility

The PNPT exam is available globally – there are no restrictions based on citizenship or requirements for security clearance [1][4]. However, if you’re under 18, you’ll need to submit a Parental Consent Form before purchasing your exam voucher [1][2]. There are no mandatory prerequisites like certifications or degrees to register for the PNPT [1][4]. That said, TCM Security suggests beginners in professional hacking start with the Practical Junior Penetration Tester (PJPT) certification [1][3]. Successful candidates usually have a beginner-to-intermediate understanding of networking, scripting, Windows/Linux systems, and Active Directory [7].

To take the exam, your computer should meet these minimum requirements: 8GB of RAM, 256GB of storage, and a reliable internet connection to support the local lab environment [1]. Once you’ve confirmed your eligibility and system setup, focus on building your skills with the right training resources.

Training Resources and Study Materials

The $499 PNPT voucher comes with 12 months of access to five core courses: Practical Ethical Hacking, Windows and Linux Privilege Escalation, OSINT Fundamentals, and the External Pentest Playbook [1]. These courses offer over 50 hours of on-demand video content [10]. The Practical Ethical Hacking course is the centerpiece, covering networking, scripting, and methodology. It even includes instructions for manually building your own Active Directory lab, avoiding reliance on automated scripts [1][10]. To keep your studies organized, consider using tools like Notion, Obsidian, or CherryTree for note management [10].

For hands-on practice, many students turn to TryHackMe rooms such as "Attacktive Directory" for Active Directory enumeration and "Wreath" for network pivoting [10]. Alex Olsen from TCM Security emphasizes this approach:

"There are no tricks in the exam, everything you need is in the course material so prioritize understanding and learning over completion" [7].

The exam voucher includes one free retake [1][6], and you’ll gain access to TCM Security’s Discord community, which has over 60,000 members offering support 24/7 [1][6]. Additionally, discounts are available for veterans, military members, first responders, students, and teachers, reducing the cost to around $399 [1][6][4].

Using PNPT to Land Cleared Penetration Testing Jobs

Adding PNPT to Your Resume

When listing the PNPT certification on your resume, focus on what you achieved during the 5-day assessment rather than just mentioning the credential. Highlight specific, hands-on accomplishments like:

  • Conducting active/passive network enumeration and OSINT [3].
  • Navigating lateral and vertical network movement in a simulated corporate environment [3].
  • Bypassing antivirus (AV) and egress filters to maintain access [1].

Emphasize the unique aspects of the PNPT, such as its focus on reporting and communication skills. By showcasing the "Professional Reporting" and "Live Debrief" components, you demonstrate that you’re prepared for client-facing roles, not just technical tasks [2] [8]. To further stand out, consider transforming your redacted PNPT exam report into a portfolio piece. This can showcase your approach, the impact of your work, and your ability to propose clear remediation steps – qualities that hiring managers value [2].

Additionally, mention that well-known organizations like the NSA, U.S. Air Force, Booz Allen Hamilton, and Peraton recognize the PNPT certification. This adds credibility to your resume and highlights its relevance in the industry [2] [3].

"The PNPT has appeared in job postings or been purchased for pentesting teams in organizations such as: Microsoft, Nvidia, McDonalds, Twitch, Capital One, Arctic Wolf, Booz Allen, The National Security Agency, The Air Force, and more…" – Josh Daniels, TCM Security [3]

Finding PNPT-Relevant Cleared Jobs

Once you’ve updated your resume to reflect your PNPT accomplishments, use targeted job search tools to find roles that align with your skills. Platforms like Cleared Cyber Security Jobs cater specifically to security-cleared professionals. Upload your resume to their database, where employers actively seek candidates with penetration testing certifications. Use the platform’s filters to zero in on positions that value skills like Active Directory exploitation and professional reporting – areas where the PNPT shines.

Set up job alerts for roles mentioning terms like "Active Directory", "network exploitation", or "offensive security." Companies such as Peraton have already listed the PNPT in job postings for entry-level penetration tester positions, making it easier to identify employers who understand its value [2].

You can also broaden your search by attending job fairs hosted by Cleared Cyber Security Jobs. These events allow you to connect directly with hiring managers from cleared organizations, giving you a chance to discuss your PNPT experience in person. For additional networking, join the TCM Security Discord channel, which boasts over 60,000 members [3] [1]. This community includes professionals working in cleared environments, offering valuable insights and connections.

Discussing PNPT Experience in Interviews

Your PNPT experience can be a game-changer during interviews. Treat it as a real-world engagement and prepare a concise 15-minute narrative. Explain how you gained initial access, pivoted through the network to compromise a Domain Controller, and proposed effective remediation strategies [2].

"The PNPT certification sets itself apart from most offensive certifications by emphasizing the report quality and the post-engagement debrief" – Daniel Pizarro, Black Hills Information Security [8]

When discussing vulnerabilities, provide both offensive and defensive perspectives. This approach demonstrates your understanding of how security teams can counteract the simulated attacks you performed.

Bring a redacted version of your PNPT exam report as a portfolio piece. This serves as tangible proof of your ability to produce professional-grade documentation. The two days dedicated to report writing during the exam highlight your readiness to deliver client-facing deliverables, not just technical results [3] [1].

Conclusion

The PNPT certification offers a hands-on approach to validating penetration testing skills. It mirrors the full scope of a real-world engagement, from initial reconnaissance to delivering a final debrief [1][3].

For cybersecurity professionals with security clearances, this certification addresses a pressing challenge: gaining practical experience. The five-day practical assessment, combined with the requirement to produce a detailed report, showcases your ability to handle every phase of a penetration test. With its strong focus on Active Directory exploitation, the PNPT aligns perfectly with the technical requirements often encountered in government and defense roles, where these systems are common.

Experts have highlighted the program’s focus on readiness:

"The goal is for certified students to be trained, experienced, and ready on day one to take on the technical responsibilities of a penetration tester, giving PNPT holders and hiring managers confidence in their abilities." – Josh Daniels, Author, TCM Security [3]

Several major employers in the cleared space have already recognized or incorporated the PNPT for hiring and training purposes [2][3]. The certification is also a cost-effective option, especially for military veterans who can take advantage of available discounts [1][2].

FAQs

How hard is the PNPT exam?

The PNPT exam is a professional-level test that demands a solid grasp of network penetration testing concepts and hands-on skills. While challenging, it’s often rated around a 6.5 out of 10 in terms of difficulty. Those with prior hacking experience tend to find it more approachable, as the exam emphasizes practical knowledge and real-world penetration testing scenarios.

What should I include in my PNPT report and debrief?

Your PNPT report and debrief must deliver a clear and professional summary of your penetration testing process. This document should serve as a comprehensive yet concise record of your approach, findings, and technical expertise.

Focus on detailing your methodology step by step:

  • Reconnaissance: Explain how you gathered information about the target. Highlight the tools and techniques used to identify potential entry points.
  • Internal Network Exploitation: Document activities like compromising an Active Directory environment or any other internal systems. Be specific about the vulnerabilities exploited and how they were leveraged.
  • Post-Exploitation: Outline what actions were taken after gaining access, such as privilege escalation, lateral movement, or data exfiltration.

For each phase, include the following:

  • Steps Taken: Describe the exact process followed during the test.
  • Tools Used: Specify the tools and scripts employed, along with their purpose.
  • Vulnerabilities Identified: Clearly list the security flaws discovered, their severity, and how they were exploited.
  • Impacts: Explain the consequences of these vulnerabilities if left unaddressed, emphasizing risks to the organization.

Structure your report logically, ensuring it’s easy to follow. Use headings, bullet points, and visuals like screenshots or diagrams where appropriate. Remember, this report is not just a technical document – it’s a reflection of your skills and professionalism, which are key to passing the exam.

How can PNPT help me get a cleared pentesting job?

The PNPT certification boosts your prospects for securing a cleared penetration testing role by focusing on practical, job-focused skills such as reconnaissance, Active Directory compromise, and professional reporting. Its focus on real-world scenarios showcases your ability to tackle complex security assessments, making you stand out as a candidate. Employers appreciate this hands-on experience, as it directly matches the demands of cleared pentesting positions.

Related Blog Posts

  • OSCE Certification Career Guide for Advanced Cleared Pen Testers
  • GPEN Certification Career Guide for Cleared Penetration Testers
  • PenTest Plus Certification Career Guide for Cleared Pen Testers
  • LPT Certification Career Guide for Cleared Pen Test Leads

Related Guides

  • CRTL Certification Career Guide for Cleared Red Team Leads
  • CRTO Certification Career Guide for Cleared Red Team Operators
  • CRTP Certification Career Guide for Cleared Red Team Professionals
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

LPT Certification Career Guide for Cleared Pen Test Leads

CyberSecJobs Editorial · February 20, 2026 ·

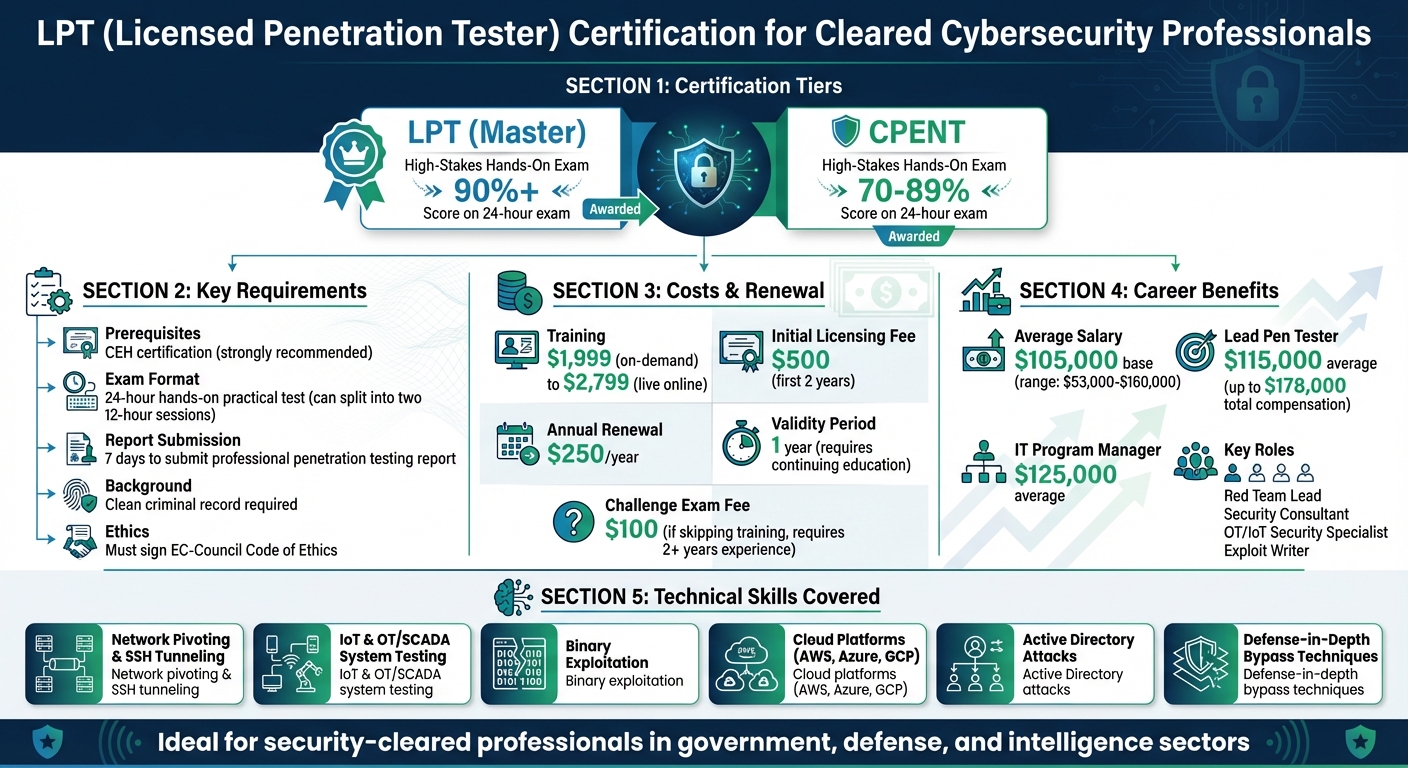
The Licensed Penetration Tester (LPT) certification is a premier credential for professionals in high-security roles, such as government, defense, and intelligence. It validates advanced penetration testing skills, including network pivoting, SSH tunneling, and overcoming layered defenses. Achieving this certification requires passing a rigorous 24-hour practical exam with a score of 90% or higher. Those scoring 70%-89% earn the Certified Penetration Testing Professional (CPENT) instead.

Key Highlights:

  • Target Audience: Professionals with security clearance in classified environments.
  • Prerequisites: Strongly recommended to have Certified Ethical Hacker (CEH) certification.
  • Cost: Over $2,000 for training and exams, plus a $250 annual renewal fee.
  • Exam Structure: Hands-on, live-proctored, 24-hour test with real-world scenarios.
  • Career Impact: Opens doors to roles like Red Team Lead and Security Consultant, with salaries often exceeding $120,000.

This certification is ideal for those seeking leadership roles in penetration testing, especially in cleared environments. It emphasizes technical expertise, structured methodologies, and professional reporting skills.

LPT Certification Requirements, Costs, and Career Benefits Overview

LPT Certification Requirements, Costs, and Career Benefits Overview

Eligibility and Prerequisites for the LPT Certification

Required Certifications and Experience

To earn the LPT (Master) certification, candidates must excel in the Certified Penetration Testing Professional (CPENT) exam. While not mandatory, the Certified Ethical Hacker (CEH) certification is highly recommended as it provides a strong foundation for the advanced skills required in penetration testing [2][7][8]. According to the EC-Council, there are no strict eligibility criteria to attempt the exam [6], but having a CEH background can significantly enhance preparedness.

Achieving the LPT (Master) designation requires scoring at least 90% on the 24-hour CPENT practical exam – a benchmark described by the EC-Council as exceptionally challenging [3]. Candidates who score between 70% and 89% receive the CPENT certification instead [3][6]. Additionally, you must submit a detailed penetration testing report that includes both technical insights for engineers and an executive summary tailored for stakeholders [2][10].

Applicants are also required to provide a resume, character references, and proof (or a declaration) of a clean criminal record. Signing the EC-Council Code of Ethics is mandatory. The licensing fee is $500 for the first two years, with an annual renewal fee of $250 thereafter [1][3][7][8].

How Security Clearance Affects Eligibility

While security clearance isn’t a direct requirement for the LPT certification, it plays a critical role in qualifying for certain cleared penetration testing roles. These roles, often within organizations like the CIA, FBI, or Department of Defense, demand an active security clearance as proof of trustworthiness and ethical conduct [9]. This aligns with the certification’s stringent ethical and documentation standards.

For professionals with an active security clearance, the required criminal background check can often be fulfilled using existing clearance documentation or a report from an investigative agency, simplifying the process [10]. However, keep in mind that security clearances remain valid only during employment in the designated role. If employment ends, the clearance can be reactivated within two years [9]. As of October 2015, approximately 4.2 million government and contractor employees were eligible for security clearances [9].

How to Earn the LPT Certification

Training and Preparation Resources

The EC-Council’s CPENT program is designed to push candidates into advanced technical areas, such as IoT and OT system attacks, binary exploitation, advanced Windows exploitation, and bypassing filtered networks. It’s a serious challenge meant for those ready to take their skills to the next level.

You can access official training through EC-Council’s iLearn online platform, Accredited Training Centers, or approved academic institutions. Before you sign up, make sure the training center is authorized by EC-Council to avoid issues with course materials or exam vouchers. Pricing starts at $1,999 for on-demand courses and $2,799 for live online sessions.

Before diving into CPENT, it’s crucial to have a solid grasp of CEH and ECSA concepts. Practicing in time-bound scenarios is equally important, as the CPENT program mirrors the high-pressure environment of the exam. The practice ranges include challenges like Active Directory, IoT systems, binary exploitation, and capture-the-flag scenarios. Pay special attention to multi-level pivoting techniques, such as single and double pivoting with SSH tunneling, since these are key for navigating hidden network segments. Additionally, refine your report-writing skills to produce both technical solutions and clear, concise executive summaries.

Once you’re confident in these areas, it’s time to focus on understanding the exam structure.

The 24-Hour Practical Exam Explained

The LPT exam is a fully hands-on, practical test conducted remotely and monitored live by EC-Council proctors. You’ll face a complex, multi-layered network equipped with defense-in-depth measures, and you’ll need to make quick, strategic decisions under tight time limits. The test is divided into three levels, each containing three challenges. You can choose to tackle the exam in one 24-hour session or split it into two 12-hour sessions.

One unique aspect of the exam is its "one exam, two certifications" structure. Your score determines whether you earn just the CPENT certification or progress to the LPT (Master) level. As EC-Council puts it:

"This exam has one purpose: To differentiate the experts from the novices in Penetration Testing!"

After completing your exam, you’ll have seven days to submit a professional penetration testing report. This report is a critical component of the certification process, as it must meet EC-Council’s standards to secure your certification. The CPENT exam is widely regarded as one of the most challenging practical tests in penetration testing, designed to validate top-tier expertise.

Once you pass, the next step is to complete the application and report submission process.

Application and Renewal Process

The rigorous training and exam requirements ensure that your certification reflects genuine expertise in penetration testing.

If you decide to skip official training and directly challenge the exam, you’ll need at least two years of verifiable experience in information security. Additionally, you’ll pay a $100 non-refundable eligibility application fee. The application review process typically takes 6 to 8 weeks. Once your report is approved and all conditions are met, you’ll receive your certification.

The LPT (Master) certification is valid for just one year, with annual renewal required under EC-Council’s Continuing Education policy. The renewal fee is $250, and you’ll need to meet specific continuing education requirements to maintain your certification. This short validity period reflects the fast-changing nature of penetration testing, ensuring that certified professionals stay up to date with new threats and techniques.

Career Benefits of LPT for Cleared Pen Test Leads

Access to Advanced Penetration Testing Roles

The LPT (Master) certification is crafted to highlight elite penetration testers[3][13]. Achieving this certification requires scoring 90% or higher on a rigorous practical exam, signaling to cleared employers that you excel in handling complex technical challenges found in advanced testing environments.

With this certification, professionals can transition from purely technical roles to strategic leadership positions like Red Team Lead or Security Consultant. These roles focus on designing testing methodologies rather than just executing scans[4]. The certification also validates expertise in specialized areas, such as IoT, OT/SCADA systems, and cloud platforms like AWS, Azure, and GCP – skills that are crucial for defense and government sectors[13].

Unlike beginner-level certifications that emphasize tools, the LPT showcases a comprehensive skill set. Candidates are required to produce professional-grade reports, demonstrating their ability to communicate risks effectively to both stakeholders and management. This communication skill is a defining trait of senior leads, setting them apart from junior testers[4][13]. Such advancements naturally lead to higher financial rewards and leadership opportunities for cleared penetration testers.

Salary Advantages for LPT-Certified Professionals

The financial upsides of earning the LPT certification are impressive for cleared pen test professionals. On average, LPT-certified individuals earn a base salary of $105,000, with the range stretching from $53,000 to $160,000 based on experience and the complexity of their role[12]. Lead Penetration Testers typically earn even more, with an average base salary of $115,000 and total compensation packages – including bonuses – reaching up to $178,000[14].

For those in managerial roles, such as IT Program Managers with the LPT certification, the average annual salary climbs to $125,000[12]. Pursuing senior or lead positions after certification is a proven way to maximize earning potential[14]. These financial incentives make the certification a gateway to roles that blend technical expertise with strategic decision-making.

Leadership and Specialized Roles

Earning the LPT (Master) certification unlocks opportunities for cleared penetration testers to take on roles that demand both technical depth and strategic insight. It positions professionals for leadership roles, such as Red Team Lead, or specialized positions like OT/IoT Security Specialist and Exploit Writer. Additionally, security consulting roles often require the ability to communicate high-level risks to executives – a skill honed through the LPT certification process[3][4][5].

For those with security clearance, the certification is particularly valuable in defense, intelligence, and government contracting organizations. Its emphasis on non-traditional environments, including IoT and operational technology, further enhances its appeal for critical infrastructure sectors[3][4].

sbb-itb-bf7aa6b

Using LPT Skills in Cleared Penetration Testing Roles

Testing in Classified and Hybrid Environments

The LPT certification equips professionals to tackle the complexities of classified networks and operational technology (OT) systems. These environments demand expertise that goes beyond standard IT testing. Specifically, the certification includes training on penetration testing for OT systems, a critical skill for cleared professionals working with industrial control systems or critical government infrastructure[3].

One key area of focus is the ability to test ICS/SCADA networks from the IT side. During the LPT exam, candidates encounter a dedicated zone for industrial control systems, where they must identify Programmable Logic Controllers (PLCs) and intercept Modbus communication protocols[13]. This mirrors challenges found at the intersection of IT and OT networks. The exam also evaluates advanced techniques like double-pivoting, SSH tunneling, and bypassing sophisticated defense mechanisms. These skills are essential for navigating classified networks while adhering to strict operational guidelines and legal boundaries[3][13][15].

Staying within the authorized scope of work is especially critical in cleared environments to prevent legal repercussions or security breaches.

Compliance and Reporting Requirements

LPT-certified professionals play a key role in meeting compliance mandates for cleared projects. The certification emphasizes professional reporting skills, directly supporting requirements like those outlined in NIST SP 800-53 (Control CA-8), which specifies:

"Penetration testing goes beyond automated vulnerability scanning and is conducted by agents and teams with demonstrable skills and experience that include technical expertise in network, operating system, and/or application level security."[16]

For contractors in the Defense Industrial Base, the CMMC 2.0 program, effective December 16, 2024, mandates certifications to protect Controlled Unclassified Information (CUI)[17]. LPT-certified professionals are well-equipped to conduct assessments aligned with NIST SP 800-171 R2 security requirements and submit results to the Enterprise Mission Assurance Support Service (eMASS) in compliance with specific data standards[17]. These reporting capabilities highlight the certification’s importance in high-security settings.

Additionally, dual-reporting – providing technical details for staff and executive summaries for leadership – is a must for cleared projects. Before any assessment begins, professionals must establish Rules of Engagement (RoE) that align with anticipated adversarial tools, techniques, and procedures[16].

Finding LPT Roles on Cleared Cyber Security Jobs

Cleared Cyber Security Jobs

With advanced technical and compliance skills in hand, LPT-certified professionals are well-positioned for specialized cleared roles. Cleared Cyber Security Jobs offers a platform to connect these professionals with opportunities tailored to their expertise. The platform’s job search filters help candidates zero in on positions requiring advanced penetration testing credentials. Employers on the site often seek LPT-certified professionals for roles such as Red Team Lead, OT/IoT Security Specialist, and Security Consultant.

Candidates can use the site’s resume database to showcase their LPT (Master) credential, 24-hour practical exam achievement, and specialized skills in areas like OT/SCADA testing, binary exploitation, and cloud compliance. Job alerts ensure candidates are notified when new roles requiring LPT certification become available.

The platform’s veteran-founded mission aligns with the LPT certification’s relevance to military occupational specialties, making it particularly appealing for veterans transitioning into cleared cybersecurity roles[11]. Notably, employers on Cleared Cyber Security Jobs are direct-hire organizations, offering candidates direct access to decision-makers who value advanced certifications in high-security environments.

EC-Council Advanced Penetration Testing Program

Conclusion

The LPT (Master) certification stands as a premier credential for professionals aiming to excel in cleared penetration testing. It’s not just a test of skills but also a challenge in meticulous documentation, ensuring only the most skilled individuals achieve this distinction.

To prepare effectively, focus on mastering the basics through certifications like CEH or CPENT. Practice creating clear, concise reports with strong executive summaries, and build endurance for extended testing scenarios [4] [13].

This certification can open doors to leadership roles in government and defense sectors [4] [13]. Its coverage of advanced areas – such as IoT, OT/SCADA networks, cloud penetration testing, and binary exploitation – meets the intricate demands of classified environments.

Maintaining the certification requires an annual renewal fee of $250 and continuing education credits [3]. This ensures your skills remain sharp in the ever-changing landscape of penetration testing. With the credential valid for one year, staying active in communities like Cleared Cyber Security Jobs can help you maximize its potential.

Though earning the LPT (Master) is challenging, it offers clear benefits: career growth, higher earning potential, and recognition within the defense and intelligence sectors.

FAQs

How hard is the LPT exam, really?

The LPT (Master) exam is notorious for its difficulty, thanks to its grueling 18-hour, hands-on structure. It immerses candidates in real-world penetration testing scenarios, pushing them to demonstrate advanced skills like multi-level pivoting, exploiting vulnerabilities, and executing web application attacks – all while racing against the clock. To succeed, you’ll need not just technical expertise but also practical experience and the composure to handle intense pressure. It’s a true test of mastery in penetration testing.

What should I practice most for CPENT/LPT?

To get ready for the CPENT/LPT exams, it’s crucial to dive deep into advanced penetration testing skills and practice handling practical, real-world challenges. Focus on areas like exploiting filtered networks, targeting IoT/OT systems, crafting custom exploits, bypassing security defenses, and mastering intricate pivoting techniques. Success in these exams hinges on plenty of hands-on practice in simulated environments and a solid grasp of advanced tools and methodologies.

Will LPT help me land cleared lead roles faster?

Earning the LPT (Master) certification can fast-track your journey to securing top-tier leadership roles in cybersecurity. This certification highlights your advanced knowledge, demonstrates hands-on expertise, and proves your ability to perform effectively in high-pressure penetration testing situations – traits that are highly sought after in cybersecurity leadership.

Related Blog Posts

  • OSCP Certification Career Guide for Cleared Offensive Security
  • OSCE Certification Career Guide for Advanced Cleared Pen Testers
  • PenTest Plus Certification Career Guide for Cleared Pen Testers
  • CTIA Certification Career Guide for Cleared Threat Intel Analysts

Related Guides

  • CRTL Certification Career Guide for Cleared Red Team Leads
  • CRTO Certification Career Guide for Cleared Red Team Operators
  • CRTP Certification Career Guide for Cleared Red Team Professionals
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

ECSA Certification Career Guide for Cleared Security Analysts

CyberSecJobs Editorial · February 20, 2026 ·

The EC-Council Certified Security Analyst (ECSA) is a certification designed for professionals skilled in advanced penetration testing and security analysis. It bridges the gap between entry-level ethical hacking and higher-level penetration testing roles, emphasizing structured methodologies, professional report writing, and compliance with federal standards like CNSS-4014. This makes it particularly relevant for individuals in government and defense roles requiring security clearances.

Key Highlights:

  • Who it’s for: Ethical hackers, penetration testers, and security analysts, especially those in cleared environments.
  • Eligibility: Requires either EC-Council training or two years of relevant experience (with a $100 application fee).
  • Process:
    1. Complete hands-on challenges in EC-Council’s iLabs and submit a penetration testing report.
    2. Pass a 150-question exam (4 hours, 70% passing score).
  • Cost: Training bundles range from $2,000–$3,500; exam fees are $650–$1,199.
  • Career Impact: Average salary is $94,000, with roles like Penetration Tester and Security Assessor earning up to $135,000.

The certification focuses on advanced methodologies, compliance with standards like NIST, and skills in vulnerability assessment, reporting, and security architecture testing. It’s a strong credential for cleared professionals aiming to advance in cybersecurity roles.

ECSA Certification Requirements and Process

What is ECSA Certification?

The ECSA certification builds upon the CEH by focusing on structured analytical techniques and professional penetration testing. It’s tailored for ethical hackers, penetration testers, security analysts, and network administrators responsible for conducting thorough security assessments and documenting their findings. This certification is especially relevant for those working in cleared environments and aligns with federal training standards[3].

Eligibility and Prerequisites

To qualify for the ECSA certification, candidates must be at least 18 years old. Those under 18 can still apply but must provide parental consent and a letter from their institution[1]. Eligibility can be achieved in two ways:

  • Training Path: Attend official EC-Council training, such as iLearn, instructor-led courses, or sessions at an Accredited Training Center.
  • Experience Path: Demonstrate two years of professional experience in information security. This route requires a $100 non-refundable application fee and verified documentation[1].

For military personnel or cleared professionals, it’s essential to confirm that their service experience meets the two-year requirement. Once eligibility is established, candidates can proceed to the hands-on certification process.

Certification Process

The ECSA certification involves two main stages. First, candidates must tackle hands-on challenges through EC-Council’s iLabs platform and create a detailed penetration testing report. This report should outline their findings and recommended countermeasures[1]. Only after the report is approved can candidates advance to the final exam.

The final exam consists of 150 multiple-choice questions, with a time limit of 4 hours and a required passing score of 70%[3]. Candidates are allowed up to five attempts per year. While the first retake can be done immediately, any additional attempts require a 14-day waiting period[3]. Exam vouchers are priced between $650 and $999, depending on the selected training bundle[1].

"Only candidates who can successfully complete the challenges and pass the report writing portion of the course will be allowed to take the EC-Council Certified Security Analyst (ECSA) certification exam." – EC-Council[5]

To maintain the ECSA credential, certified professionals must earn 120 continuing education credits over three years, with a minimum of 20 credits required each year[1].

sbb-itb-bf7aa6b

Skills Gained from ECSA Certification

Penetration Testing Methodologies

The ECSA certification focuses on advanced penetration testing techniques, emphasizing structured, step-by-step methodologies that align with established standards like NIST and the Penetration Testing Execution Standard (PTES). This structured approach is particularly valuable in high-security environments, where thorough documentation and compliance are just as important as technical precision.

Training covers a wide array of security assessment areas, including testing perimeter devices, performing vulnerability analysis, and maintaining network access. These methods are designed to simulate advanced persistent threats (APTs) often encountered by government agencies. Through EC-Council iLabs, participants gain hands-on experience, practicing tasks like network pivoting and assessing firewalls and IDS/IPS systems that protect classified systems. The certification also meets the National Training Standards for Information Systems Security Officers (CNSS-4014) and System Certifiers (NSTISSI-4015), making it especially relevant for roles in federal agencies and defense contracting. These practical skills form the foundation for advanced vulnerability analysis and reporting, which the program delves into further.

Vulnerability Assessment and Reporting

ECSA-certified professionals are trained to go beyond simply using security tools – they learn how to analyze and interpret the results to identify real security gaps. The program emphasizes prioritizing exploitable vulnerabilities in critical systems and translating technical findings into actionable risk summaries.

A key component of the training is Module 12: Report Writing and Post Testing Actions, which focuses on documenting findings clearly and recommending specific countermeasures. The certification ensures that participants can produce professional-grade reports that meet the standards expected in enterprise and government audits. These skills are critical for communicating risks effectively to both technical teams and decision-makers in high-security settings.

Security Architecture Testing

Building on the foundation of analysis and reporting, the ECSA certification also prepares professionals to evaluate modern security architectures. The curriculum addresses both traditional infrastructures and emerging platforms like AWS, Azure, and hybrid cloud environments, which are increasingly common in government and defense operations.

Training includes assessing domain controllers, internal network segmentation, and web server security. These skills are essential for determining whether security architectures meet federal compliance requirements and effectively mitigate risks in classified settings. Participants learn how to evaluate internal segmentation controls designed to prevent lateral movement between classified and unclassified networks – an essential aspect of maintaining compliance in cleared facilities. By covering both legacy systems and modern cloud-based platforms, the ECSA ensures that professionals are equipped to handle the diverse range of systems present in today’s cybersecurity landscape.

EC-Council Certified Security Analyst (ECSA)

How to Obtain the ECSA Certification

ECSA Certification Process: 3-Step Path to Becoming a Certified Security Analyst

ECSA Certification Process: 3-Step Path to Becoming a Certified Security Analyst

Step 1: Training or Eligibility Application

The ECSA certification offers two distinct paths, depending on your experience level. If you’re new to the field, you can enroll in EC-Council training through options like iLearn, Live Online sessions, or Client-Site classes. These training bootcamps typically cost between $2,000 and $3,500 and include exam fees and lab access [5][9].

For seasoned professionals, there’s an alternative route. You can apply by providing proof of at least two years of relevant experience, along with a $100 non-refundable fee [6][10]. To avoid delays of 5–10 business days, make sure your references respond promptly [6][8].

Additionally, experienced candidates with three or more years in at least three core domains can explore the Grandfathering Program. This program has two options: Competence-Verification for $200 or Skills-Validation for $250, the latter including courseware and an exam voucher [8].

While the Certified Ethical Hacker (CEH) certification isn’t a strict requirement, it is highly recommended – especially for cleared professionals. CEH is explicitly listed under DoD 8570.1 compliance for roles like CND Analyst and Incident Responder, making it a valuable stepping stone before pursuing the ECSA [7][9].

Once you’ve chosen your eligibility path, the next step is to develop hands-on skills through iLabs challenges.

Step 2: Completing iLabs and Report Submission

You’ll need to complete iLabs challenges and submit a detailed penetration testing report [1][5]. Access to iLabs typically lasts between 6–12 months, with optional 5-day extensions available for $200 each [5][3].

Your report serves as the primary evidence of your testing skills, so professional documentation is critical [10]. Treat this process seriously – strong documentation skills are highly valued in the job market, particularly for cleared positions. Focus on creating a thorough and professional report as part of your preparation.

Once your report is reviewed and approved, you’ll be ready to move on to the exam.

Step 3: Passing the Certification Exam

After your report is validated, you can take the ECSA certification exam. The test consists of 150 questions, must be completed within 4 hours, and requires a 70% passing score [9][10]. You have two options for taking the exam: through the ECC Exam Portal for $950 or via Pearson VUE for $1,199 [6].

If you don’t pass the exam on your first attempt, you can retake it immediately. However, subsequent attempts require a 14-day waiting period, and you’re limited to five attempts per year [3].

To maintain your certification, you’ll need to earn 120 continuing education credits over three years, with a minimum of 20 credits per year [1].

Career Paths for ECSA-Certified Cleared Professionals

Cleared Job Roles That Require ECSA

For security-cleared professionals, earning an ECSA certification goes beyond just adding another credential to their resume. It validates advanced skills and opens doors to specialized, high-paying roles in cybersecurity. These roles often focus on structured penetration testing and include positions like Penetration Tester, Vulnerability Analyst, Security Assessor, Red Team Member, and Security Auditor [2][4]. These jobs align with the NICE Framework’s categories of "Protect and Defend", "Operate and Collect", and "Analyze" [3].

The ECSA certification prioritizes a methodical approach to penetration testing rather than simply relying on tools. It aligns with federal standards such as CNSS–4014 and NSTISSI–4015, which are critical in environments requiring assessments of hybrid setups that combine on-premise systems with cloud platforms [2][3].

"The ECSA is not a certification for entry-level learners; it is designed for professionals with a baseline understanding of cybersecurity who are ready to conduct methodical, structured penetration tests and document their findings with the same rigor and professionalism required in enterprise environments." – Examsnap [2]

Earning this certification can also lead to competitive salaries. On average, ECSA-certified professionals make $94,000 annually, with roles like Penetration Tester earning around $110,715 and top-tier positions like CISO reaching approximately $130,000. Salaries typically fall between $75,000 and $120,000, reflecting the certification’s value in the cleared job market [1][4][11].

ECSA Certification Advantages in the Cleared Job Market

The benefits of ECSA certification go beyond qualifying for specific roles. Its value lies in the competitive edge it provides within high-security environments. Here’s a breakdown of its key advantages and considerations:

Advantages Considerations
Hands-On Validation: iLabs simulate complex enterprise networks with layered defenses, showcasing practical skills [2] Experience Requirement: Requires two years of relevant experience or completion of official training [1]
Professional Reporting: Mandatory report preparation trains analysts to meet strict documentation standards [2] Rigorous Assessment: Success hinges on the quality of the submitted report [2]
Career Progression: Bridges foundational credentials like CEH to advanced certifications like LPT Master [1][2] Continuing Education: Requires earning 120 credits over three years to maintain certification [1]
Market Growth: Cybersecurity market projected to grow from $172 billion in 2022 to over $345 billion by 2030 [4] Specialized Focus: Less recognized than CEH or OSCP in certain non-government sectors [3]

The ECSA’s focus on methodology-driven analysis – rather than tool-based testing – makes it particularly valuable in cleared environments. These settings demand structured assessment processes and professionals who can translate technical vulnerabilities into actionable insights for executives. This ability is essential for government agencies and defense contractors responsible for identifying system weaknesses and recommending improvements [2][4].

Using ECSA Certification on Cleared Cyber Security Jobs

Cleared Cyber Security Jobs

Using Job Search Tools and Filters

If you’ve honed your penetration testing and reporting skills through your ECSA certification, you can make this credential work for you in the job market. Cleared Cyber Security Jobs offers tools to help you find positions tailored to your qualifications. Start by entering keywords like "ECSA" or "EC-Council Certified Security Analyst" in the search bar to uncover roles where this certification is highly valued [12]. Since the ECSA is recognized as a baseline skill by the U.S. Department of Defense (DoD) for its cyber workforce, these searches often lead to government contractor roles [9].

Refine your search results by applying filters for specific agencies or departments. Focus on organizations like the Department of Homeland Security (DHS) or the DoD, which actively seek EC-Council-certified professionals for their Security Operations Centers (SOC) [9][12]. The ECSA certification aligns with federal hiring standards, increasing your visibility to recruiters working within these frameworks [3].

Highlighting ECSA on Your Resume

When uploading your resume to Cleared Cyber Security Jobs, make sure your ECSA certification stands out in both the certifications and skills sections. Highlight your expertise in structured methodologies like the Penetration Testing Execution Standard (PTES) and NIST frameworks, which are integral to the ECSA curriculum [2]. Use specific terms such as "Security Architecture Testing" and "Vulnerability Reporting" to align with the language used by federal recruiters [3][9].

If you’ve gained hands-on experience with EC-Council iLabs, emphasize that to demonstrate your practical testing abilities [2]. Position your ECSA certification as a stepping stone between the Certified Ethical Hacker (CEH) and the Licensed Penetration Tester (LPT) Master certification, showcasing your progression toward advanced offensive security expertise [1][2]. For those who qualified through the two-year experience route instead of formal training, ensure your profile includes verifiable details of your professional background in information security [1].

Consider linking your EC-Council ASPEN digital badge directly to your profile. This feature allows employers to instantly verify your certification status and can help you stand out from candidates who only list their credentials without proof. Coupled with these resume strategies, the platform’s career resources can help you streamline your job search.

Using Career Resources and Job Alerts

Pair your polished resume with the career resources available through Cleared Cyber Security Jobs. The platform offers free tools tailored for security-cleared professionals, including advice on certification pathways and professional growth. Setting up ECSA-specific job alerts can help you quickly spot relevant positions. With penetration testers holding an ECSA certification earning an average salary of $96,000 annually – and top earners exceeding $135,000 – these alerts can guide you toward lucrative opportunities [9].

Additionally, the platform provides insights into recertification requirements. Since ECSA certification is valid for three years, you’ll need to either retake the exam or earn Continuing Education Units (CEUs) to maintain your status [9]. Staying on top of these requirements ensures your certification remains valid and attractive to potential employers. If you’re a veteran, the platform also offers guidance on using the GI Bill for test fee reimbursement, as the Department of Veterans Affairs includes ECSA under its eligible programs [9].

Conclusion

The ECSA certification showcases your ability to conduct structured, standards-based penetration tests. By training in frameworks like PTES and NIST, you’ll be prepared to tackle challenges in modern infrastructures, including cloud, mobile, and virtual environments [2][3]. Acting as a bridge between the foundational CEH skills and the advanced LPT Master certification, ECSA is a strategic credential for professionals aiming to advance in cybersecurity [2]. Additionally, meeting federal standards like CNSS-4014 and NSTISSI-4015 highlights its importance in government and defense roles [3]. This recognition not only validates your technical expertise but also opens doors to rewarding career paths.

Earning potential is another compelling factor. ECSA-certified professionals typically make between $75,000 and $120,000 annually, with top positions exceeding $130,000 [1][4]. As John Terra from Simplilearn explains, "ECSA is one of the five proven certifications that can significantly boost your cybersecurity career and enhance your earning power" [1].

To make the most of your ECSA credential, platforms like Cleared Cyber Security Jobs provide tools to connect you with real opportunities. Utilize keyword searches, apply agency-specific filters, and set up job alerts to stay informed about new openings. When crafting your resume, highlight not only your technical abilities but also your proficiency in documenting findings – a key ECSA skill that sets you apart as a trusted security consultant [2].

FAQs

Is ECSA worth it if I already have CEH?

Yes, earning an ECSA is worth considering even if you already hold a CEH. While the CEH lays the groundwork by teaching ethical hacking tools and techniques, the ECSA takes it a step further. It emphasizes applying those skills in real-world settings, focusing on methodology-based penetration testing and crafting detailed reports. This hands-on approach sharpens your practical abilities, making it a great option for professionals aiming to excel in security-cleared roles or climb the ladder in cybersecurity.

Which cleared roles benefit most from ECSA?

Cleared roles that gain the most from the ECSA certification include Cyber Security Engineers, Security Analysts, and Information Systems Security Managers (ISSM). These positions typically demand advanced expertise in areas like penetration testing, vulnerability assessment, and creating detailed security reports. The ECSA’s emphasis on hands-on testing and practical application makes it particularly useful for professionals in government or defense sectors looking to deepen their technical skills.

How hard is the ECSA iLabs report?

The challenge level of the ECSA iLabs report largely hinges on your familiarity with penetration testing. The exam presents around a dozen tasks, each increasing in complexity, designed to assess your ability to exploit vulnerabilities and document your findings effectively. With a 12-hour window to tackle at least five of these challenges and produce a comprehensive report, the process can feel intense – especially for those who may not be well-versed in structured methods or working under tight deadlines.

Related Blog Posts

  • CEH Certified Ethical Hacker Career Guide for Cleared Pen Testers
  • GSEC Certification Career Guide for Cleared Security Essentials
  • CySA Plus Certification Career Guide for Cleared SOC Analysts
  • CTIA Certification Career Guide for Cleared Threat Intel Analysts

Related Guides

  • Splunk Certification Career Guide for Cleared SIEM Analysts
  • GICSP Certification Career Guide for Cleared ICS Security
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers
  • « Go to Previous Page
  • Go to page 1
  • Interim pages omitted …
  • Go to page 4
  • Go to page 5
  • Go to page 6
  • Go to page 7
  • Go to page 8
  • Interim pages omitted …
  • Go to page 14
  • Go to Next Page »
  • Facebook
  • Instagram
  • LinkedIn
  • Twitter
  • YouTube

Cleared Cyber Security Jobs | CyberSecJobs.com

  • Contact
  • About
  • Privacy Policy