• Skip to primary navigation
  • Skip to main content
Cleared Cyber Security Jobs | CyberSecJobs.com

Cleared Cyber Security Jobs | CyberSecJobs.com

Cleared Cyber Security Jobs

  • Home
  • Search Cleared Cyber Jobs
  • Job Fairs
  • Career Resources

CyberSecJobs Editorial

Incident Response Analyst Career Path for Cleared Professionals

CyberSecJobs Editorial · March 7, 2026 ·

When cyberattacks hit government or defense networks, Incident Response Analysts are the first line of defense. These cybersecurity experts detect, investigate, and neutralize threats to protect sensitive systems. For cleared professionals, this role offers high demand, competitive pay ($80,000–$138,000 annually, with some earning $200,000), and career stability.

Key takeaways:

  • Role Overview: Analysts monitor systems, respond to alerts, perform forensic investigations, and secure classified data.
  • Career Path: Progression includes Tier 1 (entry-level), Tier 2 (intermediate), Tier 3 (advanced), and management roles, with salaries increasing at each level.
  • Skills & Certifications: Proficiency with tools like Splunk and EDR, strong communication skills, and certifications (e.g., CompTIA Security+, CISSP) are essential.
  • Security Clearance: Secret or Top Secret clearance is often required, with a rigorous background check process.
  • Job Market: The U.S. has over 663,000 cybersecurity job openings, with a projected 28% growth through 2026.

This career combines technical expertise, clearances, and certifications to protect critical systems while offering lucrative opportunities for growth.
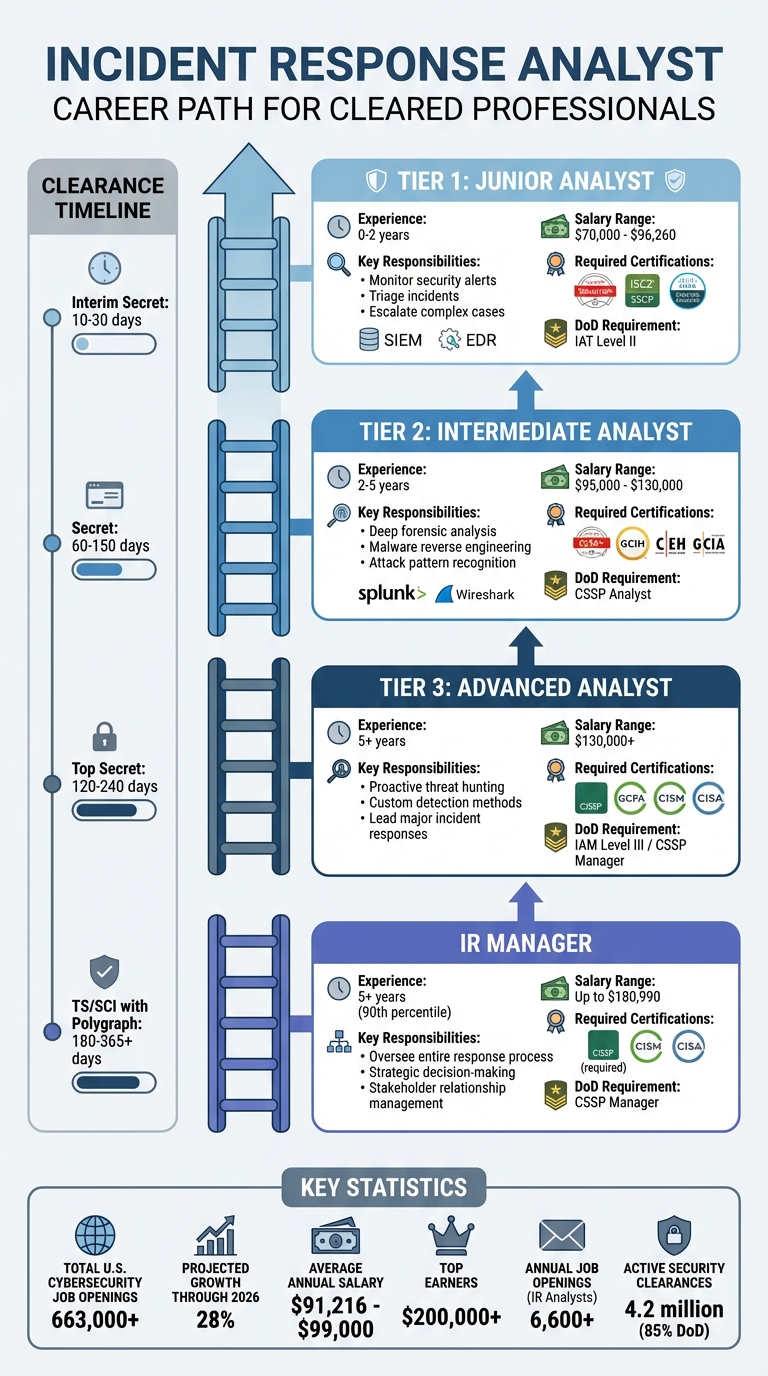
Incident Response Analyst Career Path: Tiers, Salaries, and Certifications

Incident Response Analyst Career Path: Tiers, Salaries, and Certifications

Main Duties of a Cleared Incident Response Analyst

Daily Tasks and Responsibilities

Cleared Incident Response Analysts are on the front line, monitoring classified networks with tools like Security Information and Event Management (SIEM) and Endpoint Detection and Response (EDR). Their goal? Spot unusual activity that might signal a breach [8, 10, 11]. When an alert pops up, they dig into its origins, pinpoint vulnerabilities, and act fast – whether that means isolating a compromised system or disabling an affected account [9, 11]. These steps are crucial for maintaining the integrity of classified environments.

Forensic analysis is another key part of the job. Analysts sift through system data, log files, and network traffic to piece together what happened during a breach and figure out what information was exposed [9, 10]. Collaboration is also essential. They work closely with IT teams, legal departments, and even law enforcement to ensure a coordinated response that meets regulatory standards [5]. In classified settings, every finding is meticulously documented to comply with frameworks like SOC 2 and ISO 27001 and to support post-incident reviews [8, 10]. The best Security Operations Centers aim to detect threats in under 15 minutes and respond to critical alerts within an hour [6].

Working With Classified Information

Handling classified data adds another layer of complexity. Analysts must follow strict Chain of Custody protocols, carefully documenting every step of evidence collection, transfer, and analysis to ensure it holds up in legal or governmental settings [8]. Tools like write-blockers are used to prevent accidental changes during data collection, and forensic images are verified with cryptographic hashes to maintain accuracy [8]. Organizations with advanced data classification systems report 68% fewer unauthorized data exposures, highlighting the importance of these processes [7].

Beyond technical work, analysts must communicate findings clearly to stakeholders. This involves translating complex technical details into straightforward explanations while adhering to notification rules based on the classification level of the data [14, 16]. As the field evolves, so do the skills and responsibilities required at different experience levels.

Job Levels in Cleared Incident Response

Careers in cleared incident response follow a structured path, with increasing responsibilities tied to technical expertise and the management of classified data.

  • Tier 1 (Junior) analysts: With 0–2 years of experience, these analysts handle initial tasks like monitoring alerts, triaging incidents, and escalating more complex cases. Salaries for this level range from $74,390 to $96,260 [10, 11].
  • Tier 2 (Intermediate) analysts: With 2–5 years under their belts, these professionals take on deeper forensic analysis, malware reverse engineering, and pattern recognition to identify attack methods [6].
  • Tier 3 (Advanced) analysts: With over 5 years of experience, these analysts focus on proactive threat hunting, crafting custom detection methods, and leading major incident responses [6].
  • IR Managers: At the senior level, managers oversee the entire response process, make strategic decisions, and maintain relationships with stakeholders. Those at the 90th percentile of experience can earn around $180,990 [8, 9, 10].

Each tier reflects a blend of technical skill and the ability to handle increasingly sensitive and complex responsibilities.

Required Skills, Education, and Certifications

Technical and Soft Skills

To excel as a cleared Incident Response Analyst, a blend of technical expertise and strong communication skills is essential. Analysts must have a solid grasp of network security and traffic analysis, including TCP/IP, networking ports, protocols, and the OSI model. Tools like Wireshark, Zeek (Bro), and Suricata are critical for identifying malicious traffic. Familiarity with SIEM platforms such as Splunk, IBM QRadar, ArcSight, and ELK Stack is also a must for real-time monitoring and correlating security events. Additionally, proficiency with endpoint detection and response tools strengthens analytical capabilities.

Digital forensics skills are another cornerstone of the role. Analysts rely on tools like Autopsy, FTK Imager, and Volatility to investigate compromised systems, recover evidence, and trace attacker activity. For advanced roles, knowledge of malware analysis becomes critical. This involves understanding malware behavior and reverse engineering it using tools like IDA Pro, Ghidra, or Cuckoo Sandbox. Command-line expertise in Unix/Linux and Windows system administration is also key for navigating large log files and connecting data points efficiently.

Beyond technical abilities, soft skills play a vital role. Critical thinking helps analysts break down complex attack scenarios, especially under classified conditions. Clear communication is equally important for creating reports that both technical and non-technical audiences can understand. These skills ensure that analysts can navigate the strict protocols tied to security clearances [9][2].

Education Options for Cleared Professionals

Most employers (70%) require a bachelor’s degree in Computer Science, Cybersecurity, or a related field [10]. Advanced degrees are often seen as an advantage. For cleared professionals, military service or federal government experience can provide an alternative pathway, offering both technical training and the necessary security clearances. This combination not only simplifies the clearance process but also builds a strong foundation in cybersecurity.

Practical, hands-on experience is equally important. Building a home lab to practice forensic techniques, participating in Capture the Flag (CTF) competitions on platforms like TryHackMe and Hack The Box, and contributing to open-source projects like TheHive, Wazuh, or Cortex are excellent ways to gain real-world skills. Many professionals begin their careers in entry-level roles such as Network Administrator or SOC Analyst (Tier 1), often spending 2–3 years in these positions before transitioning into Incident Response Analyst roles. With the cybersecurity field expected to grow by 28% through 2026 and an average annual salary for incident analysts around $99,000, the time and effort invested in education and training are well worth it [10].

Certifications for Each Career Stage

Certifications are a critical stepping stone, especially for those without traditional degrees. In fact, 70% of hiring managers prioritize certifications that validate job-specific skills [10][1].

  • Entry-level professionals (0–2 years, earning $70,000 to $95,000) should focus on certifications like CompTIA Security+, ISC2 SSCP, or Cisco CyberOps Associate, which align with IAT Level II under DoD 8570/8140 requirements.
  • Mid-level analysts (3–5 years, earning $95,000 to $130,000) benefit from certifications such as CySA+, GCIH, CEH, or GCIA, which emphasize incident detection and response. These map to CSSP Analyst roles.
  • Senior analysts (5+ years, earning $130,000 or more) are expected to pursue advanced certifications like CISSP, GCFA, GCFE, CISM, or CISA, which focus on forensic investigation and leadership. These certifications align with IAM Level III or CSSP Manager positions [9][10][1][2].

For Department of Defense (DoD) roles, candidates often start with a baseline certification but must achieve a CSSP-A level certification within 180 days of hire [2].

Additionally, scripting proficiency and familiarity with the NIST SP 800-61 guide are crucial for career advancement [11]. Combining certifications with practical experience and formal education creates a strong foundation for navigating the rigorous clearance process, which will be explored in the next section.

Getting and Maintaining Security Clearance

Clearance Levels and What They Mean

Security clearance isn’t just about access – it’s a cornerstone of many careers in government and defense. It’s required for roles that deal with classified networks and sensitive intelligence, and the level of clearance you hold dictates what systems you can use and which incidents you can investigate [13].

Here’s a breakdown of the main clearance levels:

  • Secret (Tier 3): Grants access to information that could cause serious harm to national security if disclosed. This level, common among Department of Defense (DoD) contractors, involves a National Agency Check with Law and Credit (NACLC) review.
  • Top Secret (Tier 5): Opens the door to information that could cause "exceptionally grave damage" to national security. It requires a Single Scope Background Investigation (SSBI), covering a detailed 10-year history.
  • Top Secret/Sensitive Compartmented Information (TS/SCI): The highest level, often required for intelligence and cyber threat roles. This clearance may include a polygraph and grants access to highly sensitive sources [13].

Currently, around 4.2 million government and contractor employees hold security clearances, with 85% of them working for the DoD [15][12]. Next, let’s dive into how these clearances are vetted and approved.

The Background Investigation Process

To get started, you’ll need a government agency or authorized contractor to sponsor your application after offering a conditional job based on a "need-to-know" basis [13][14]. Once sponsored, you’ll fill out the Standard Form 86 (SF-86) using the eApp platform, which replaced the older e-QIP system in 2026. This form requires extensive details about your last 10 years, including residences, jobs, foreign contacts, and financial history [13][18].

The Defense Counterintelligence and Security Agency (DCSA) handles the bulk – 95% – of federal background checks [13][16]. During the investigation, they’ll verify your employment, credit history, and criminal records, and they’ll interview references. For Top Secret clearances, the process goes deeper, with investigators speaking to neighbors, coworkers, and personal contacts.

Here’s how long it typically takes:

  • Interim Secret: 10 to 30 days
  • Secret: 60 to 150 days
  • Top Secret: 120 to 240 days
  • TS/SCI with polygraph: 180 to over 365 days [13]

"The SF-86 application process creates more problems when candidates hide information than the actual issues they try to conceal." – JOBSwithDOD [17]

Clearance denials happen most often due to financial issues (40%), followed by criminal conduct (24%) and dishonesty (15%) [17][18]. Certain factors will disqualify you outright, such as non-U.S. citizenship, illegal drug use (including marijuana, which remains federally illegal), dishonorable military discharge, or being declared mentally incapacitated [12][13].

This rigorous process directly ties into the career options available to you, as outlined below.

How Clearance Affects Your Career Options

Your clearance level doesn’t just define what you can access – it shapes your career path. High-level roles like Information Systems Security Officer (ISSO), Cyber Threat Intelligence Analyst, and Network Defense Forensics Analyst require active clearances [13]. If you leave a cleared position, your clearance becomes inactive after 24 months, but a new sponsor can reactivate it within that time [13].

Since 2026, the Trusted Workforce 2.0 (TW 2.0) framework has replaced periodic reinvestigations with Continuous Vetting (CV). This system keeps tabs on criminal records, credit issues, and foreign travel in real-time. It also requires you to self-report significant events like arrests, major debts, or financial changes. Not reporting such events is often seen as a bigger violation than the issue itself.

"A security clearance is a privilege, not a right. Mishandling classified documents can lead to criminal charges, job loss, and fines." – US Federal Contractor Registration (USFCR) [14]

Adjudicators also check publicly available information like social media, GitHub contributions, and other online activity to assess your judgment and operational security awareness [13][15]. Before applying, it’s wise to:

  • Pull your credit report and address any issues.
  • Review your social media privacy settings.
  • Compile a complete list of foreign contacts, including names and nationalities.

Honesty is critical on your SF-86. Disclosing past issues, like financial troubles or minor drug use, is often viewed more favorably under the "whole-person concept" than trying to hide them [13][15].

Clearance Level Investigation Tier Typical Scope 2026 Avg. Timeline
Secret Tier 3 5-10 year record verification; some interviews 60 – 150 Days
Top Secret Tier 5 10-year scope; in-person interviews 120 – 240 Days
TS/SCI Tier 5 + Polygraph Tier 5 scope plus specialized polygraph exam 180 – 365+ Days
Interim Secret N/A Initial fingerprint and database checks 10 – 30 Days

Finding Jobs and Building Your Network

Writing a Resume for Cleared Positions

When crafting a resume for cleared incident response roles, it’s crucial to balance showcasing your skills with maintaining operational security. Start with a clear and concise summary at the top. Highlight your years of experience, certifications, and specific incident response expertise. Skip the buzzwords and keep it factual – this isn’t the place for subjective self-praise [19][20].

Include a technical skills section that lists tools you’ve worked with, like SIEM platforms, intrusion detection systems, forensics software, and vulnerability scanners [21]. For your work history, use the STAR method (Situation, Task, Action, Result) to frame your accomplishments in measurable terms. For example, instead of saying "Handled security incidents", you could write, "Reduced detection time by 35% through automated SIEM correlation rules across 12 classified networks" [21].

Operational security is non-negotiable. Clearly state your clearance level and issuing agency at the top of your resume, but avoid mentioning classified project names, colleague identities, or sensitive budget details [19][20]. Also, be mindful of how much experience you highlight. Surprisingly, listing "30+ years of experience" can sometimes deter recruiters, who may interpret it as a sign of inflexibility or high salary expectations. Many cleared positions cap requirements at 10 years [19][20].

Keep your resume simple and streamlined – 1-2 pages max, with no graphics or shading that might confuse applicant tracking systems [19][20]. If you’re working toward certifications like CISSP or CEH, include them along with expected completion dates. This can sometimes satisfy a job requirement and prompt a recruiter to reach out [21].

"Your security-cleared resume is not a biography or a mere list of qualifications. It’s an ad designed to help you land that coveted cleared job interview…" – Ashley Jones, Editor, ClearedJobs.Net [19]

One more thing: don’t list your clearance on public LinkedIn profiles. While it’s essential for specialized job boards, displaying it publicly can be a red flag for some contractors [19][20]. Once your resume is polished, focus on connecting with recruiters through dedicated cleared job platforms.

Using Cleared Cyber Security Jobs for Your Search
Cleared Cyber Security Jobs

For those in the cleared community, using platforms tailored to your field can make job searching more efficient. Cleared Cyber Security Jobs is a veteran-founded job board designed exclusively for professionals like you. It connects incident response experts directly with employers offering cleared positions, cutting out staffing firms and third-party recruiters.

Upload your resume to the platform’s database so employers can find you directly. Set up job alerts to have relevant postings sent straight to your inbox. Use search filters to narrow results by clearance level (Secret, Top Secret, TS/SCI), location, and specific roles like "SOC analyst", "threat hunter", or "digital forensics."

Here’s a pro tip: stay active on the platform. Many cleared job boards prioritize the most recently active profiles in search results. Even if you’re not actively job hunting, logging in weekly keeps your profile visible to recruiters [23]. The platform also offers job fairs, providing a rare chance to meet employers face-to-face – a crucial advantage in the often discreet world of cleared hiring.

Networking in the Cleared Community

Building a network in the cleared world takes effort and strategy. Attending conferences like BSides, Black Hat, DEF CON, and RSA is a great way to meet peers and hiring managers. But the real magic often happens during "HallwayCon" – those informal chats between sessions [22]. If the cost of attending is a barrier, consider volunteering. Not only will you gain free access to sessions, but you’ll also build trust within the community and get valuable face time with industry leaders [22].

Another underused strategy is conducting informational interviews. Reach out to professionals whose careers you admire and ask for a brief conversation about their journey. These chats can lead to learning about job openings that never make it to public listings [22].

The secret to networking is staying engaged. It’s not a one-and-done activity. Keep in touch with your contacts, share articles they might find useful, and offer assistance when you can. An active approach to maintaining relationships ensures your network remains a valuable resource throughout your career. If your efforts seem to stall, it’s often because you’ve let those connections fade after the initial meeting [22].

"In the competitive field of cyber security, networking can be the key to unlocking new opportunities." – CyberSecJobs.com [22]

sbb-itb-bf7aa6b

Advancing Your Career in Cleared Incident Response

Choosing a Specialty Area

Once you’ve established a solid foundation in incident response, diving into a specialty can open doors to higher earnings and career growth. One intriguing path is malware analysis – breaking down malicious code to uncover its purpose, origin, and potential impact [26]. If you’re drawn to proactive measures, threat hunting lets you uncover hidden dangers before they escalate. Alternatively, incident readiness and resilience focuses on creating response plans, crafting playbooks, and running tabletop exercises to strengthen an organization’s defenses [25].

Your choice of specialty should align with your interests and long-term goals. For instance, if you enjoy unraveling complex technical puzzles, areas like malware analysis or digital forensics might be a great fit. On the other hand, if you’re inclined toward leadership, moving into incident response management could be the right move. This role involves overseeing teams, delivering threat assessments, and leading responses to major incidents [27]. For those who prefer staying hands-on, becoming a subject matter expert (SME) or engineer allows you to master advanced tools and techniques while avoiding management responsibilities [26].

Some specialized roles, such as Cyber Incident Response Analysts working in OT/ICS/SCADA environments, may involve travel – up to 25% in some cases [24]. Meanwhile, emerging fields like cloud incident response and AI security are gaining traction, supported by certifications like the AI Red Teamer (OSAI+) [26]. Companies like LevelBlue, which has handled over 9,000 incidents and conducted more than 1,000 tabletop exercises, are shifting focus from reactive responses to proactive readiness with offerings like "Resilience Retainers" [25].

Continuing Education and Skill Development

After narrowing down your specialty, staying ahead of the curve is crucial. The cybersecurity landscape evolves rapidly, so continuous learning is non-negotiable. Advanced certifications can help you maintain your edge. For example, the GIAC Certified Incident Handler (GCIH) is highly regarded for managing security events, while the Computer Hacking Forensic Investigator (CHFI) certifies expertise in evidence collection and maintaining a legal chain of custody [3][28]. For leadership roles, the CISSP is often a must-have for positions like Intrusion Detection Specialist or Incident Manager [27].

Certifications like the CHFI need to be renewed every three years, requiring EC-Council Continuing Education credits to stay valid [28]. But formal credentials are just one piece of the puzzle. Hands-on experience is equally important. Setting up a home lab with virtual environments lets you practice critical skills like monitoring, reverse engineering, and forensics without risking production systems [3]. You can also participate in Capture The Flag challenges or contribute to open-source projects to sharpen your abilities and build your professional reputation [3][26].

The field is expanding into areas like IoT forensics, cloud forensics, and mobile device encryption countermeasures [28]. With AI becoming integral to faster case triage and hybrid environments – spanning cloud, mobile, and operational technology – being the new norm [1][28], staying updated through webinars, industry publications, and community forums is essential.

Salary and Job Stability

Specializing and keeping your skills sharp naturally leads to better pay and job security. Cleared incident response roles are known for their strong financial rewards. As of September 21, 2023, the average annual salary for an Incident Responder in the U.S. was $91,216, with most professionals earning between $56,000 and $118,000 [26]. Top earners can take home over $136,000, while mid-level professionals with certifications like CHFI typically earn $70,000 to $120,000 [26][28]. Senior or highly specialized roles often command salaries ranging from $75,000 to over $130,000 [11].

Location plays a big role in compensation. For instance, jobs in the Washington, D.C. metro area often come with higher pay to offset the region’s higher cost of living. Transitioning from an entry-level role, such as Cybersecurity Specialist, to a mid-level role like Incident Response Analyst typically takes 2–3 years, with each step up bringing a noticeable salary bump [1].

Job stability in this field is exceptional. Cybersecurity threats are constant across industries like finance, healthcare, and government, ensuring that skilled professionals remain in demand [26]. Unlike some tech roles that can be outsourced or automated, incident response relies heavily on human expertise – especially when dealing with classified information. This makes it a reliable and resilient career path, highlighting the importance of specialization and lifelong learning for sustained success.

From NOC Analyst to Incident Response Analyst

Conclusion

Building a successful career as a cleared Incident Response Analyst requires a combination of technical expertise, strategic certifications, and effective networking. Mastering tools like SIEM and EDR is just the start – you also need the ability to explain complex findings clearly and calmly under pressure. As Hemant Patkar, CISSP, emphasizes:

Maintaining a calm demeanor is essential, ensuring clear and timely communication with all stakeholders who need to be informed [29].

Certifications play a crucial role in validating your skills and advancing your career. Start with beginner-level certifications like CompTIA Security+ or Cisco CyberOps Associate. As you gain experience, move on to intermediate options such as the Certified Ethical Hacker (CEH) and then pursue advanced credentials like GIAC GCIH or CISSP. These certifications not only demonstrate expertise but also pave the way to higher-paying roles [3][4].

With rapid changes in the cybersecurity landscape – highlighted by over 69% of professionals noting significant industry shifts [29] – staying ahead is critical. Hands-on practice through home labs, Capture the Flag challenges, and open-source projects can help sharpen your skills [3]. As Louis Eriakha from Techloy points out:

Incident response is one of the most in-demand roles in cybersecurity right now – and it’s only growing [4].

Networking is equally important. Platforms like Cleared Cyber Security Jobs connect you with employers who understand the unique requirements of cleared positions. With more than 6,600 incident analyst job openings annually and a projected 28% growth in cybersecurity roles [10], the field offers immense opportunities for those who continually invest in their skills and maintain their clearances.

Climbing the ladder from SOC Analyst to Senior Incident Response Lead demands dedication, but the rewards – both financial and professional – are well worth it. By staying curious, documenting your processes, and honing your ability to detect, contain, and recover from cyber threats, you position yourself as an indispensable asset in safeguarding national security.

FAQs

How do I move from SOC Tier 1 into incident response?

To move from a SOC Tier 1 position into incident response, you’ll need to strengthen your technical skills and expand your knowledge base. Start by earning certifications such as CySA+ or CISSP, which are highly regarded in the field. Focus on mastering areas like log analysis, threat detection, and digital forensics – these are core components of incident response work.

Practical experience is equally important. Get hands-on with tools like SIEM and EDR platforms, as these are essential for monitoring and responding to security incidents. Networking within your organization can also open doors; connect with colleagues in the incident response team to learn from their expertise. Finally, seek out specialized training programs to further hone your skills and prepare for the more advanced challenges of incident response.

What clearance issues most often delay or derail hiring?

Lengthy processing times are one of the biggest hurdles in hiring for security-cleared roles, with investigations often stretching out for 6–12 months or even longer. Backlogs in cases add to the delays, particularly when the investigations are more complex. Issues like drug use or financial concerns can make the process even slower, creating significant challenges for meeting hiring timelines.

Which certification should I get next for my tier?

The next certification that’s right for you depends on your career path and goals. If you’re aiming to grow in incident response or cybersecurity, the CISSP is a strong choice, especially for senior-level roles. For those looking to sharpen technical skills in threat detection, CySA+ is a great option. If you want to dive deeper, certifications like Security+ or CISSP can help you access higher-level opportunities. Choose certifications that align closely with your professional aspirations and current expertise.
Related Blog Posts

  • CIO-SP3 Cybersecurity Positions vs DISA Encore III – Which Vehicle Drives Your Career?
  • GRID Certification Career Guide for Cleared Incident Response
  • CySA Plus Certification Career Guide for Cleared SOC Analysts
  • SOC Analyst Career Path for Cleared Professionals Tier 1 to Lead

Related Guides

  • Endpoint Security Engineer Career Path for Cleared Professionals
  • Application Security Engineer Career Path for Cleared Professionals
  • Cloud Security Engineer Career Path for Cleared Professionals
  • TS/SCI Salary Premium: Real 2026 Numbers
  • Security Clearance Interview: What to Expect

SOC Analyst Career Path for Cleared Professionals Tier 1 to Lead

CyberSecJobs Editorial · March 7, 2026 ·

SOC analysts are the frontline defenders in cybersecurity, especially in U.S. government and defense sectors. Their work involves monitoring networks, analyzing threats, and responding to incidents in real-time. For professionals with security clearances, SOC roles offer structured career growth and substantial salary boosts – up to $50,000 more for those with a TS/SCI clearance and polygraph.

SOC teams are organized into tiers:

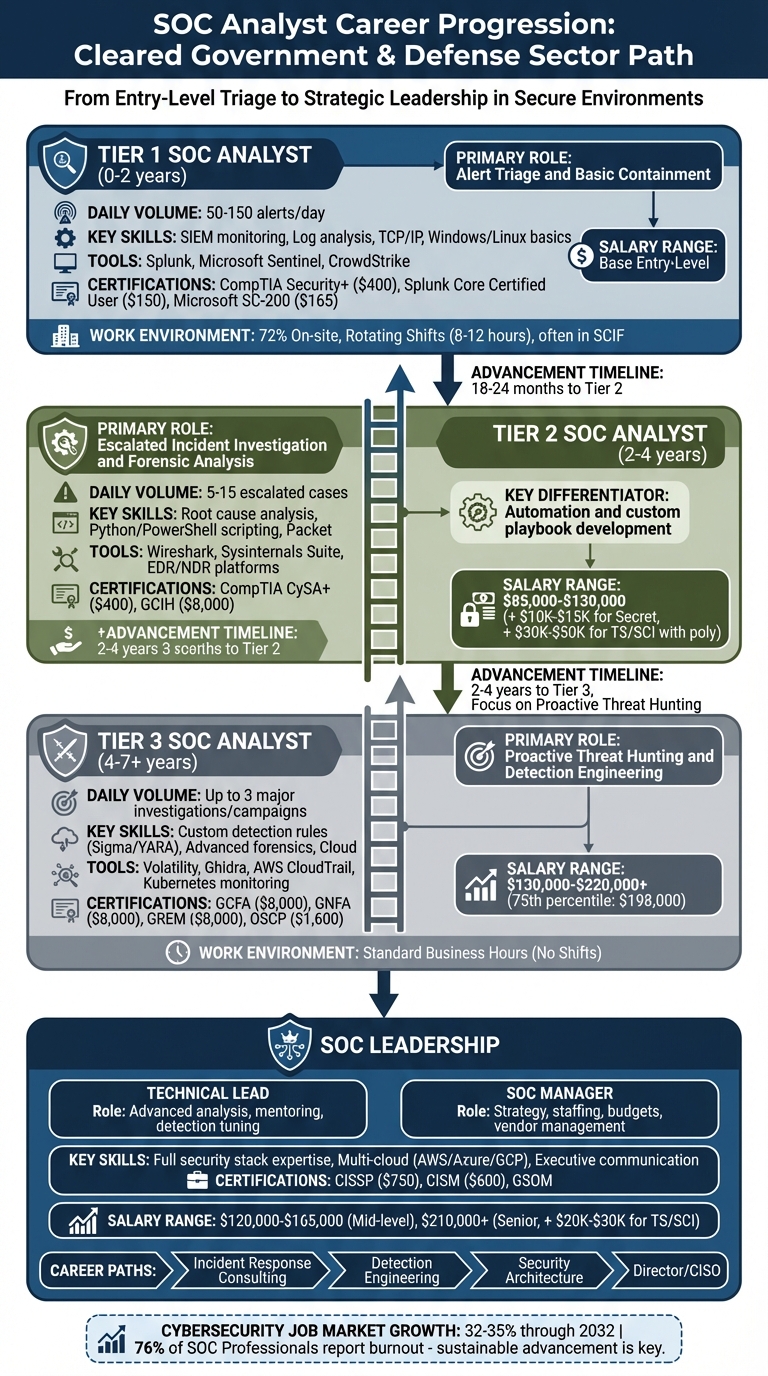
  • Tier 1 (0–2 years): Handles alert triage and basic containment.
  • Tier 2 (2–4 years): Investigates escalated incidents and performs forensic analysis.
  • Tier 3 (4–7+ years): Focuses on threat hunting and detection engineering.
  • Leadership roles: Oversee team operations and strategy.

Certifications like CompTIA Security+ (Tier 1), CySA+ (Tier 2), and CISSP (leadership) are critical for career progression. Analysts also benefit from technical skills like scripting (Python, PowerShell) and expertise in tools like Splunk and Microsoft Sentinel.

Key tips for advancing:

  • Automate repetitive tasks to showcase initiative.
  • Gain hands-on experience with SIEM tools and cloud security.
  • Build a portfolio of projects to highlight technical depth.

Cleared SOC roles are in high demand, with salaries ranging from $85,000 for Tier 2 analysts to over $200,000 for Tier 3 and leadership positions. High-performing SOCs aim for rapid detection and response times, making skilled analysts indispensable.

SOC Analyst Career Progression Path from Tier 1 to Leadership

SOC Analyst Career Progression Path from Tier 1 to Leadership

From Beginner to LEVEL 3 SOC Analyst in Cybersecurity

Required Skills and Certifications for Cleared SOC Analysts

To succeed in a cleared SOC (Security Operations Center) role, a combination of security clearance, technical expertise, and specific certifications is essential. Here’s a breakdown of what it takes to thrive in this field.

Understanding Security Clearance Levels

Security clearances are divided into three main categories, each granting access to different levels of sensitive information:

  • Confidential: Grants access to information that could harm national security if disclosed improperly[10].
  • Secret: Covers information that could cause serious harm and is commonly required for SOC analysts dealing with secure government networks[10][11].
  • Top Secret (TS): Protects information that could cause grave damage, requiring a Single Scope Background Investigation (SSBI)[10][11].

For those handling highly classified intelligence, a TS/SCI (Top Secret/Sensitive Compartmented Information) clearance is necessary. This level includes access to compartmented intelligence methods and sources[10].

The clearance process evaluates 13 factors, such as financial stability, foreign influence, and personal conduct[10][11]. In 2026, processing times for clearances varied:

  • Secret clearances: 60–150 days
  • Top Secret clearances: 120–240 days
  • TS/SCI with polygraph: 180–365+ days[11]

Under the Trusted Workforce 2.0 framework, periodic reinvestigations have been replaced by Continuous Vetting. This system monitors criminal records, credit reports, and foreign travel in real time. Applicants must self-report events like arrests, significant debts, or foreign contacts. Before applying through the eApp platform, it’s wise to:

  • Conduct a self-audit of financial records.
  • Resolve any credit issues.
  • Gather documentation for a 10-year history of residences, employment, and foreign contacts for the SF-86 form[11].

Once clearance requirements are met, the focus shifts to acquiring the technical skills needed for SOC roles.

Technical Skills Needed for Entry-Level SOC Work

At the Tier 1 level, analysts handle tasks like triaging alerts, monitoring SIEM (Security Information and Event Management) and EDR (Endpoint Detection and Response) platforms, and following playbooks for incidents like phishing or malware attacks[1][8]. Key skills include:

  • Networking basics (e.g., TCP/IP, DNS).
  • Familiarity with operating systems like Windows and Linux.
  • Log analysis using tools like Splunk, Microsoft Sentinel, and CrowdStrike[1].

Tier 2 analysts take on advanced investigations, such as root cause analysis, and use scripting languages like Python or PowerShell to automate tasks. Scripting expertise is often a stepping stone to higher roles[1][5].

At the Tier 3 level, responsibilities include proactive threat hunting, detection engineering (e.g., writing Sigma and YARA rules), and applying the MITRE ATT&CK framework[1][9].

For hands-on practice, platforms like TryHackMe, LetsDefend, and Security Onion offer simulations of real-world scenarios. Documenting these projects in a professional portfolio can help showcase your skills[6][9]. Additionally, specializing in a major SIEM tool – such as Splunk or Microsoft Sentinel – can boost your expertise and earning potential[1].

Entry-Level Certifications for Cleared SOC Careers

Certifications play a pivotal role in meeting job requirements and advancing your career. Here are some key certifications to consider:

  • CompTIA Security+: A must-have for entry-level roles, this certification is required for about 70% of SOC analyst positions and satisfies the DoD 8140/8570 IAT Level II requirement. Cost: approximately $400[1][6][7].
  • CompTIA CySA+: Ideal for Tier 2 roles, this certification focuses on behavioral analytics and threat detection. It also fulfills the DoD 8140 CSSP Analyst requirement. Cost: approximately $400[1][7].
  • Microsoft SC-200 (Security Operations Analyst): While not DoD 8140-compliant, this certification is highly regarded in organizations using Azure-based security tools, particularly for those working with Microsoft Sentinel. Cost: approximately $165[1].
Certification Career Level DoD 8140/8570 Relevance Approximate Cost
CompTIA Security+ Tier 1 / Entry IAT Level II $400
CompTIA CySA+ Tier 2 / Mid CSSP Analyst $400
Microsoft SC-200 Tier 1–2 / Specialist No (Vendor-Specific) $165

These certifications, combined with technical skills and clearances, form the foundation for a successful career in cleared SOC environments.

Tier 1 SOC Analyst: Entry-Level Cleared SOC Positions

Daily Tasks and Work Environment

As a Tier 1 SOC analyst, you’re the first responder in the world of cybersecurity, acting as the initial line of defense in a SOC (Security Operations Center). Your main job? Monitoring SIEM (Security Information and Event Management) dashboards – tools like Splunk, Microsoft Sentinel, or IBM QRadar – to sift through anywhere from 50 to 150 alerts a day[12]. The tricky part is separating true positives (real threats) from false positives (noise), all while working within tight timelines. High-severity alerts often require action within 15 to 30 minutes.

Every alert you handle gets logged in a ticketing system like ServiceNow or Jira. Your tasks include assessing the "blast radius" of an incident – figuring out which endpoints, user accounts, or networks are affected. Depending on the situation, you might resolve the issue yourself or escalate it to Tier 2. Basic containment steps, like blocking a malicious IP or isolating a compromised device, are carried out using pre-written playbooks.

If you’re working in a cleared environment, expect to be on-site in a SCIF (Sensitive Compartmented Information Facility), where personal devices are strictly off-limits. Shifts usually rotate in 8- or 12-hour blocks and often include nights, weekends, and holidays. Fully remote SOC positions are rare – only 6% of roles offer this flexibility, and for cleared positions, on-site work is even more common at 72%[1]. A typical shift involves a handover from the previous team, continuous alert monitoring, and thorough documentation.

"Tier 1 analysts are the triage nurses who assess every patient walking through the door and determine severity." – Nora Grace, Training Camp[13]

This demanding role sets the foundation for the skills and certifications essential to succeed as a Tier 1 analyst.

Skills and Certifications for Tier 1 Analysts

The CompTIA Security+ certification is often the starting point for Tier 1 analysts, but vendor-specific certifications can make you stand out. For example, the Splunk Core Certified User (costing around $150) highlights your ability to navigate one of the most popular SIEM platforms. Similarly, the Microsoft SC-200 certification (costing $165–$200) demonstrates expertise in Microsoft Sentinel environments[12][1].

Your day-to-day work will involve analyzing logs from firewalls, proxies, and endpoints to detect unusual activity. You’ll need to understand how SIEM correlation rules work, recognize what triggers alerts, and communicate your findings effectively – whether it’s to technical teams or non-technical stakeholders. Writing clear, concise incident summaries (usually five sentences) is just as critical as your technical skills[8].

Modern SOC environments are increasingly focused on cloud-native signals like AWS CloudTrail logs, Azure Activity Logs, and identity-based anomalies such as MFA (multi-factor authentication) issues. Familiarity with the MITRE ATT&CK framework is also crucial for categorizing adversary tactics and techniques during escalations[12][7]. With organizations facing an average of 4,484 alerts daily and 67% of them going uninvestigated due to alert fatigue, your ability to prioritize and triage effectively becomes a key asset[1].

Mastering these skills and certifications lays the groundwork for advancing into more challenging roles, like Tier 2 analyst positions.

How to Move from Tier 1 to Tier 2

Most analysts spend 18 to 24 months in a Tier 1 role before moving up to Tier 2[1]. The key to advancing is shifting from simply following playbooks to building automation tools. Learning Python or PowerShell is a game-changer, enabling you to automate repetitive tasks like creating shift reports or parsing VirusTotal API data. This not only shows initiative but also reduces the manual workload for your team[1][3].

Volunteer to take on escalated incidents to demonstrate your investigative skills. Documenting your approach to root cause analysis can highlight your ability to work independently. Additionally, maintaining a log to fine-tune noisy detection rules showcases leadership potential and your commitment to improving SOC efficiency[8].

"The jump from Tier 1 to Tier 2 is where many analysts stall. It’s not enough to be good at triaging alerts. You need to demonstrate investigative ability and technical depth." – Safwan Azeem, Advanced Cybersecurity & Management Certification[3]

To strengthen your qualifications, consider earning the CompTIA CySA+ certification (around $400) or specializing in areas like network forensics or malware analysis. Participating in incident post-mortems and tracking action items can also help you gain visibility with senior management[5]. High-performing SOCs aim for a Mean Time to Detect (MTTD) of under 15 minutes and a Mean Time to Respond (MTTR) of under 1 hour for critical alerts. Consistently meeting these benchmarks can fast-track your career progression[4].

Tier 2 and Tier 3 SOC Analysts: Mid-Level and Senior Positions

Tier 2: Advanced Analysis and Incident Response

Tier 2 analysts take on escalated incidents, diving deeper into investigations and coordinating containment strategies[2][12]. These analysts typically handle 5–15 escalated cases daily, focusing on detailed analysis rather than sheer volume[12]. A significant part of the job involves working with tools like SIEM, EDR, and NDR to piece together attack timelines and uncover the root cause of incidents. This often means identifying how attackers initially gained access and which systems were affected.

Expect to rely heavily on tools like Wireshark for packet inspection and the Sysinternals Suite for Windows analysis. While malware analysis is part of the role, especially for identifying known threats, more complex samples are usually escalated to Tier 3.

"Tier 2 is the escape hatch. Most burnout concentrates at Tier 1… The 1-2 year push to Tier 2 dramatically improves quality of life." – Cybersecurity Jobs List[1]

In the U.S., Tier 2 analysts earn between $85,000 and $130,000 annually[12]. Holding a Secret clearance can add $10,000–$15,000 to your salary, while a TS/SCI with polygraph may increase it by $30,000–$50,000[1]. Companies like Booz Allen Hamilton and Leidos actively hire for these roles, with Booz Allen offering salaries ranging from $88,000 to $201,000 for senior positions[1].

Tier 2 work serves as a stepping stone to Tier 3, where the focus shifts from reactive incident response to proactive threat hunting and detection engineering.

Tier 3: Threat Hunting and Detection Engineering

Tier 3 analysts take their expertise to the next level, focusing on anticipating and uncovering hidden threats rather than responding to alerts. This role, the highest technical level in a SOC, involves proactive threat hunting. Analysts look for signs of lateral movement or persistence mechanisms that automated systems might miss. Typically, Tier 3 analysts manage up to three major investigations or proactive campaigns daily[12].

Detection engineering is a core responsibility at this level. Analysts create custom detection rules using tools like Sigma or YARA while conducting advanced forensics with platforms such as Volatility and Ghidra[1]. In cloud-native environments, you’ll monitor AWS CloudTrail logs, Kubernetes pod activity, and other cloud-specific signals[4].

Salaries for Tier 3 analysts range from $130,000 to $220,000+, with the 75th percentile reaching $198,000 in total compensation[12][1]. These roles, which are significantly more expensive for organizations than Tier 1 positions, reflect the advanced expertise required. Unlike lower-tier roles, Tier 3 analysts often work standard business hours instead of shifts[12].

Mid-Level and Advanced Certifications

To move into Tier 2 roles, certifications like the CompTIA CySA+ (around $400) focus on behavioral analytics and threat detection[1]. For analysts working with Microsoft Sentinel, the Microsoft SC-200 (approximately $165) is a cost-effective option[1][3]. Another valuable certification is the GCIH (GIAC Certified Incident Handler), priced at about $8,000, which is often employer-sponsored due to its comprehensive approach to incident response frameworks like NIST and SANS PICERL[12].

Tier 3 roles demand more specialized certifications. Options like the GCFA (GIAC Certified Forensic Analyst), GNFA (GIAC Certified Network Forensic Analyst), and GREM (GIAC Certified Reverse Engineering Malware), each costing roughly $8,000, are highly regarded[12]. The OSCP (Offensive Security Certified Professional), priced at around $1,600, is another strong choice for developing an adversary mindset and enhancing threat-hunting skills[12]. Additionally, expertise in specific SIEM tools such as Splunk (featured in 37% of SOC analyst job postings) or Microsoft Sentinel (26% of postings) can command a higher salary premium than being a generalist[1].

sbb-itb-bf7aa6b

SOC Leadership: Lead Analyst and Manager Positions

What SOC Leads and Managers Do

SOC leadership typically splits into two paths: technical leads and managers. Technical leads focus on day-to-day operations, such as managing alert queues, mentoring junior team members, and being the go-to person for high-severity incidents[14]. They stay heavily involved in hands-on investigations, often diving into process trees, logs, and other forensic details during active incidents.

On the other hand, managers concentrate on the bigger picture – strategy and administrative responsibilities. Their work includes hiring, managing budgets, negotiating with vendors, and briefing executives on the organization’s security posture[14]. While technical leads fine-tune the SOC’s response to threats, managers ensure the team has the workforce, tools, and funding needed to thrive.

Feature Technical Lead SOC Manager
Primary Focus Advanced analysis & threat hunting Strategy, people, and budget
Daily Task Tuning detection rules & hunting Staffing, reporting, & vendor management
Primary Metric Detection coverage & accuracy MTTA, MTTR, & team retention
Stakeholders Tier 1/2 analysts & engineers CISO, Legal, HR, & Finance

A challenge faced by SOC managers is the high burnout rate among analysts. According to Splunk’s 2025 Global State of Security report, 52% of SOC analysts have considered leaving their jobs due to the overwhelming volume of alerts and urgent incidents[14]. To combat this, managers must prioritize sustainable shift schedules and monitor team well-being.

These two leadership roles demand distinct skill sets, paving the way for certifications and expertise that define top-tier SOC leaders.

Leadership Skills and Required Certifications

To excel in SOC leadership, you need a strong grasp of the entire security stack. This includes expertise in SIEM platforms like Splunk or Sentinel, SOAR tools such as Cortex XSOAR, and EDR/XDR solutions like CrowdStrike[14]. As many SOCs now operate in multi-cloud environments, familiarity with AWS, Azure, or GCP is increasingly valuable[14].

But technical skills are only part of the equation. Communication is just as critical. SOC leaders must translate complex incidents into language that executives can understand, focusing on business risks rather than technical jargon[14]. During major breaches, they often act as coordinators, aligning responses across legal, HR, and PR teams – a task sometimes referred to as "escalation diplomacy."

Certifications play a key role in building credibility. The Certified Information Systems Security Professional (CISSP) remains a top credential, costing about $750 and appearing in 47% of security management job postings[1]. The Certified Information Security Manager (CISM), priced at around $600, is particularly valued in governance-heavy roles[1]. For SOC-specific leadership, the GIAC Security Operations Manager (GSOM) certification is another strong option[5].

"Holding CISSP doesn’t guarantee promotion – but not holding any cert often guarantees you’ll be overlooked."

  • Safwan Azeem[5]

These certifications also meet DoD 8140/8570 requirements for management roles[15]. In the U.S., mid-level SOC managers with 5–8 years of experience typically earn between $120,000 and $165,000, with senior managers in major metro areas earning upwards of $210,000[14]. A TS/SCI clearance can boost these figures by an additional $20,000–$30,000[1].

Career Options Beyond SOC Operations

SOC leadership is more than just a job – it’s a launching pad for broader opportunities in cybersecurity. Many professionals leverage their experience to transition into specialized roles.

One common option is Incident Response Consulting, where experts help organizations navigate major breaches as external advisors[14]. Others move into Detection Engineering, a growing field focused on creating detection logic rather than reacting to alerts[1].

Another path is Security Architecture, where you can apply your understanding of threats to design stronger defensive systems[14]. For those aiming to climb even higher, SOC leadership can lead to positions like Director of Security Operations or even Chief Information Security Officer (CISO)[14].

At the senior level, success hinges on your ability to link technical work to business outcomes – whether you stay in the SOC or branch out into enterprise security roles.

Planning Your Cleared SOC Career Path

Using Job Listings to Identify Required Skills

Job postings can be a goldmine for understanding the skills needed to climb the SOC career ladder. For instance, SIEM tools appear in a whopping 82% of SOC job listings, while Python shows up in 24% of mid-level roles – hinting that scripting skills are a must for moving from Tier 1 to Tier 2[1]. When browsing job descriptions on Cleared Cyber Security Jobs, don’t just skim the basics. If a Tier 2 role mentions "automation" or "custom playbooks", it’s a signal to focus on automation skills. Similarly, mentions of AWS CloudTrail or Azure Activity Logs highlight the growing importance of cloud security expertise[4].

On top of technical skills, holding a security clearance can significantly boost your earning potential. A Secret clearance might add $10,000–$15,000 to your salary, while a TS/SCI clearance could mean an extra $20,000–$30,000. Combine these advantages with in-demand technical skills, and you’re setting yourself up for success[1].

Developing Skills and Choosing a Specialty

Breaking out of Tier 1 often means shifting from reactive tasks to proactive problem-solving. One of the quickest ways to advance is by automating repetitive tasks like shift reports, VirusTotal lookups, or indicator enrichment. Tools like Python and PowerShell can help you streamline these processes[1]. To showcase your skills, document your automation projects on GitHub – this portfolio can be a game-changer during interviews[8][18].

When it comes to specialization, most SOC career paths branch into three main areas:

  • Detection Engineering: Focus on mastering query languages like KQL (for Microsoft Sentinel) or SPL (for Splunk). Learn how to deploy detection rules using APIs and adopt "Detection-as-Code" practices[17].
  • Cloud Security: Dive into monitoring Kubernetes, serverless environments, and cloud audit logs to address the growing demand for cloud expertise[4].
  • Threat Intelligence: Hone your skills in researching adversary tactics and integrating that knowledge into detection systems[3].

Certifications can also fast-track your progress. For example, CompTIA CySA+ (around $400) is a great investment for moving from Tier 1 to Tier 2[1]. If you’re working with Microsoft Sentinel, the Microsoft SC-200 certification (about $165) is a cost-effective way to deepen your expertise[1][3]. For those aspiring to leadership roles, the CISSP certification (approximately $750) is highly respected, though it requires five years of experience[1].

While building your technical skills is vital, maintaining balance and avoiding burnout is equally important for long-term growth.

Preventing Burnout in SOC Roles

SOC roles can be demanding, with 76% of security professionals reporting burnout in 2025[1]. Transitioning to Tier 2 can often provide relief from the high-pressure environment of Tier 1 work.

Start by looking into shift schedules during interviews. SOCs offering 4×10 schedules (four 10-hour days with three days off) or 3×12 shifts can be more manageable compared to traditional rotating 8-hour shifts[1]. Defense contractors often provide more predictable schedules compared to MSSPs, where burnout tends to be more common[1].

Automation isn’t just a career booster – it can also lighten your mental load by reducing repetitive, mundane tasks[3]. Set aside time for deep, uninterrupted work away from the constant barrage of alerts. Volunteering for tasks like incident retrospectives can also help you build leadership visibility while giving you a break from the alert queue. Seek out mentors who have successfully navigated their way to Tier 3 or management roles – they can offer invaluable guidance[5][16].

If you start feeling burned out, address it early. Open communication can help you manage the situation while maintaining your visibility and keeping your career progression on track[5].

Conclusion: Building a Successful Cleared SOC Career

Climbing the ladder from a Tier 1 SOC Analyst to a leadership role in the SOC world takes more than just time. It’s about consistently sharpening your skills, making smart certification decisions, and fully leveraging the advantages of your security clearance. The typical career path involves excelling at alert triage, moving into incident response, mastering threat hunting, and eventually stepping into leadership positions.

The jump between tiers often hinges on specific skills. For example, developing automation expertise can help you move to Tier 2, while honing threat hunting capabilities is crucial for Tier 3 [1]. Leadership, on the other hand, demands a shift in focus – from hands-on technical tasks to managing teams and overseeing strategic goals [5].

Your security clearance isn’t just a qualification – it’s a major asset that can significantly boost your career and salary. A Secret clearance can add $10,000–$15,000 to your annual pay, while a TS/SCI with polygraph might increase it by $30,000–$50,000 [1]. With the cybersecurity job market expected to grow by 32% to 35% through 2032 [4][19], cleared professionals are well-positioned to secure high-paying, stable roles, especially in government and defense sectors that remain steady even during economic uncertainty.

"Security leadership doesn’t wait for permission. It moves forward when you do." – Safwan Azeem [5]

To stand out, focus on hands-on experience, earn progressively advanced certifications (like Security+, CySA+, and CISSP), and build a strong portfolio [8]. And don’t underestimate the importance of a sustainable work environment – better schedules and reduced repetitive stress are key to thriving in the long run [1].

FAQs

Do I need an active clearance to get hired?

Yes, most SOC analyst positions that require security clearances, like Secret or Top Secret, typically demand an active clearance. This is often a crucial qualification for these roles.

Which certification should I get first for Tier 1?

The CompTIA Security+ certification is an excellent starting point for anyone aiming to become a Tier 1 SOC analyst. It covers the basics of cybersecurity and is widely acknowledged as a standard entry-level credential for many jobs in the industry.

How can I move from Tier 1 to Tier 2 faster?

To move from Tier 1 to Tier 2 more quickly, concentrate on developing essential skills such as understanding systems, automating repetitive tasks, and crafting detection rules that go beyond just handling alerts. Certifications like Security+ or CySA+ can help demonstrate your technical abilities. Alongside this, connect with mentors, build relationships within your organization, and stay informed about cloud-native threats and the latest security tools. These steps can help you stand out and speed up your career progression.

Related Blog Posts

  • Top 10 Cyber Security Jobs for Cleared Professionals
  • Cleared Cyber Management Transition – From Technical to Leadership Roles
  • Python Cleared SOC Analyst Skills – The $20K Programming Premium
  • CySA Plus Certification Career Guide for Cleared SOC Analysts


Related Guides

  • Endpoint Security Engineer Career Path for Cleared Professionals
  • Application Security Engineer Career Path for Cleared Professionals
  • Cloud Security Engineer Career Path for Cleared Professionals
  • TS/SCI Salary Premium: Real 2026 Numbers
  • Security Clearance Interview: What to Expect

Cisco CCIE Security Career Guide for Cleared Expert Engineers

CyberSecJobs Editorial · March 7, 2026 ·

The Cisco CCIE Security certification is a top-tier credential for network security professionals, especially those with active security clearance. It validates expertise in designing, deploying, and managing advanced security systems, making it highly valuable for federal cybersecurity roles. With only a 26% average pass rate, the certification is challenging but opens doors to six-figure salaries and leadership positions like Security Architect and CISO.

Key Takeaways:

  • Certification Requirements: Pass a 120-minute SCOR core exam ($400) and an 8-hour lab exam ($1,600).
  • Skills Covered: Network security (firewalls, VPNs, ISE), cloud security, automation with Python/APIs.
  • Career Impact: High demand for cleared CCIE-certified professionals in federal cybersecurity, with roles in architecture, engineering, and leadership.
  • Preparation Tips: Focus on Cisco’s exam blueprint, practice in virtual labs, and build automation skills.

Cleared professionals with CCIE Security can secure top positions with government contractors like CACI, Peraton, and Lockheed Martin. This certification is a stepping stone to advancing in the federal cybersecurity sector.

How To Pass The CCIE Security Exam (Tips & Advice)

Exam Requirements and Preparation for CCIE Security

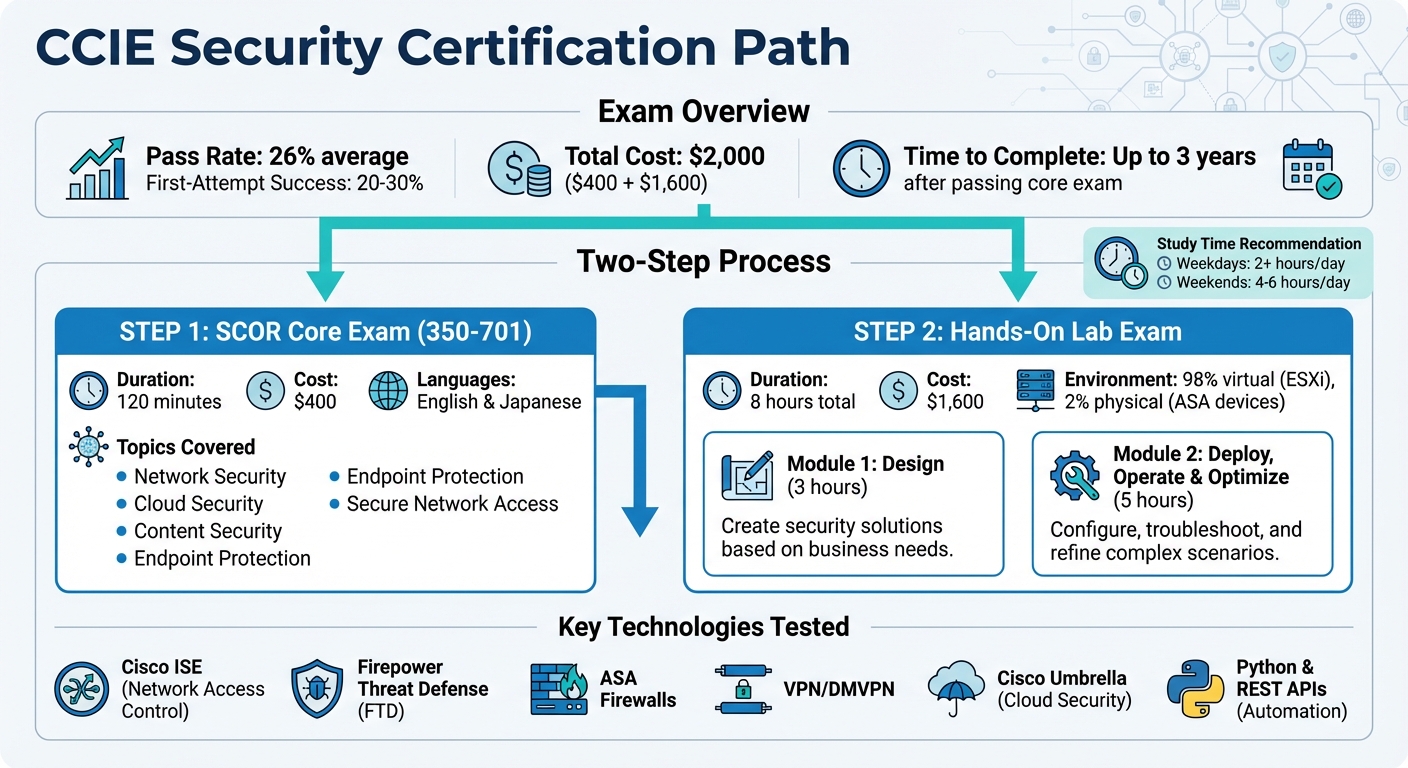
CCIE Security Certification Path and Exam Requirements

CCIE Security Certification Path and Exam Requirements

CCIE Security Exam Structure

Earning the CCIE Security certification requires passing two challenging exams: a 120-minute SCOR core exam and an 8-hour hands-on lab exam. The 350-701 SCOR core exam focuses on topics like network security, cloud security, content security, endpoint protection, and secure network access. Each attempt costs $400, and the exam is available in English and Japanese [2]. After passing the core exam, candidates have three years to complete the lab exam. The lab exam costs $1,600 and is split into two distinct modules [2].

  • Module 1: Design (3 hours) tests your ability to create security solutions based on specific business needs.
  • Module 2: Deploy, Operate, and Optimize (5 hours) evaluates your skills in configuring, troubleshooting, and refining complex security scenarios using both virtual and physical equipment [3].

The lab environment is predominantly virtual, with about 98% of tasks running on virtual machines in an ESXi setup. The remaining 2% involves physical ASA devices, which are used for clustering and failover scenarios [3]. Key technologies covered include Cisco Identity Services Engine (ISE) for network access control, Firepower Threat Defense (FTD) and ASA firewalls for perimeter security, VPN technologies like DMVPN, Cisco Umbrella for cloud security, and automation tools such as Python and REST APIs via Postman [1].

The CCIE Security exam is notoriously difficult, with an average pass rate of just 26%. First-attempt success rates hover between 20–30%, underscoring the need for thorough and strategic preparation [5].

Study Strategies for Cleared Engineers

For professionals in cleared roles aiming to excel in high-level federal cybersecurity positions, mastering the CCIE Security exam requires a disciplined and efficient approach. The demands of balancing a full-time job with limited study time make targeted strategies essential. Start by reviewing Cisco’s official exam blueprint to identify areas where you lack expertise. As Zia Hussain, Program Manager for the CCIE Security exam, advises:

"The exam blueprint should be the starting point of your journey. Identify the tasks from the blueprint that you are not an expert at. Then, build the lab modules for those tasks." [3]

Time management is key. Aim for at least two hours of study during weekdays and dedicate four to six hours on weekends [8]. Leverage virtual lab solutions like Cisco Modeling Labs (CML), EVE-NG, or GNS3 to simulate complex network setups without the need for costly physical hardware [7]. Cisco also provides CCIE Practice Labs for $50 per four-hour session, offering an environment similar to the actual exam setup [6].

To build the speed and decision-making skills required for the exam, practice full lab modules under timed conditions. Additionally, focus on developing Python scripting and Postman API skills, as these are integral to automation tasks. A crucial tip: save your configurations frequently during practice to prevent data loss during the exam [5].

These strategies can help cleared professionals effectively prepare for one of the most demanding certifications in the cybersecurity field.

Job Opportunities for CCIE Security Holders with Clearance

Top Jobs for Cleared CCIE Security Engineers

Earning a CCIE Security certification and holding clearance can open the door to high-level roles in network architecture and security engineering. These professionals are in demand for positions that involve designing and securing critical systems. For those focused on architecture, roles like Senior Network Architect, Enterprise Architect, and C2C Architect involve creating secure frameworks to support defense and intelligence operations. On the security engineering side, positions such as Senior Network Security Engineer and Senior Firewall Engineer focus on protecting network perimeters.

There are also specialized technical roles, like Cisco ISE Engineer, which center on managing network access and identity control. If you’re more interested in pre-sales, CCIE Security Certified Pre-Sales Engineers work on designing and presenting secure solutions tailored to government clients [9]. For those aiming for senior leadership, expert roles such as Principal Network Engineer and IT Network SME provide opportunities to lead critical projects. These roles span a variety of career paths, offering flexibility and growth potential in cleared environments.

Employers Hiring Cleared CCIE Security Professionals

A wide range of government contractors and specialized firms actively recruit CCIE Security professionals with clearance. For security engineering roles, companies like CACI, Crimson Phoenix, and TEKsystems frequently hire qualified candidates. If your focus is on network architecture, firms such as Zachary Piper Solutions, NTG, and Peraton value expertise in designing strategic security solutions.

For more senior positions, organizations including GuROO LLC, TENICA, and Mission Services LLC are on the lookout for Principal Network Engineers and IT Network SMEs. Those interested in operations can explore roles like Tier III Operations & Maintenance Network Engineer and Senior Network Administrator with contractors such as Dexian Signature Federal and Agensys. Meanwhile, specialized positions like Network Automation Engineer and Cisco ISE Engineer are in demand at employers like Zachary Piper Solutions and OMW Consulting. These employers offer a mix of opportunities, ensuring there’s something for every cleared CCIE Security professional.

sbb-itb-bf7aa6b

Career Growth Strategies with CCIE Security

Applying CCIE Skills to Emerging Technologies

Earning a CCIE Security certification positions you to tackle critical cybersecurity challenges by applying advanced skills to cutting-edge technologies that align with federal agencies’ priorities [4]. As Norman St. Laurent, Federal Product Marketing Manager at Cisco, puts it:

"To be successful in cybersecurity, it is crucial to remain committed to continuous learning and stay aware of industry developments." [10]

One area transforming Security Operations Centers (SOCs) is machine learning-based threat detection, which enables proactive threat hunting [10]. To stay ahead, focus on mastering cloud security across IaaS, PaaS, and SaaS platforms, and gain a solid understanding of API protocols to protect interconnected federal systems [10][11].

Regular recertification every two years keeps you updated on the latest advancements. Platforms like Cisco U. provide valuable resources, such as the course "Performing CyberOps Using Cisco Security Technologies", which dives into threat hunting, incident response, and malware forensics [10]. For hands-on experience, Cisco dCloud offers virtual labs designed to refine your technical expertise [10].

Acquiring expertise in emerging technologies not only sharpens your technical skillset but also increases your value to top employers in the cleared sector. These capabilities can open doors to new career opportunities and advancement.

Using Cleared Cyber Security Jobs for Career Advancement

With your growing technical expertise, you can use specialized platforms like Cleared Cyber Security Jobs to take your career to the next level. This platform caters specifically to security-cleared professionals, offering tools like job search filters that help you find roles based on clearance level, location, and CCIE-related qualifications. Upload your resume to attract employers actively seeking CCIE Security experts.

Set up job alerts for leadership roles such as Principal Network Engineer, Senior Network Architect, or CISO – positions that align with the advanced skills your CCIE Security certification provides [4]. The platform also offers career resources tailored to your needs, including advice on showcasing your CCIE credentials to appeal to government contractors. Additionally, their job fairs connect you directly with hiring managers from top companies like CACI, Peraton, and Lockheed Martin [11].

Since Cleared Cyber Security Jobs exclusively partners with direct-hire employers and requires U.S. citizenship with active clearance, you can trust that the opportunities are legitimate. This streamlined approach connects you with roles that can significantly advance your career in the cleared sector.

Conclusion

Earning the CCIE Security certification alongside a security clearance can significantly propel your career in the cleared cybersecurity sector. This combination addresses the federal sector’s growing need for secure, high-performing network solutions, opening doors to roles like Network Security Architect, Security Consultant, or even Chief Information Security Officer – positions that require both technical expertise and trusted access to sensitive government systems.

Zia Hussain, Cisco’s Program Manager for the CCIE Security exam, shares his perspective on the certification’s impact, reflecting on his 22-year journey from a TAC support engineer to senior leadership:

"Being CCIE certified hugely contributed towards my professional achievements and is key to career advancement."

This sentiment highlights the certification’s role in shaping successful careers.

The CCIE Security certification proves your ability to design, implement, and troubleshoot advanced security systems – skills essential for safeguarding defense and intelligence networks. Staying at the top of your field means committing to continuous learning and keeping up with new technologies [4].

To connect with opportunities in cleared cybersecurity, consider using Cleared Cyber Security Jobs. This platform is tailored for U.S. citizens with active security clearance, offering features like job alerts, resume uploads, and targeted job fairs to help you connect with government contractors looking for experts like you.

The cleared cybersecurity sector relies on professionals who can protect critical national security infrastructure. With your combined credentials, you are well-positioned to meet this demand and advance your career by connecting with leading employers in the industry.

FAQs

How long should I plan to prepare for CCIE Security?

You should allocate six to twelve months for dedicated preparation when working toward the CCIE Security certification. This period gives you enough time to dive deep into the material and develop the expertise required to excel in the exam.

What clearance levels get the most value from CCIE Security?

The CCIE Security certification holds exceptional value for professionals aiming for roles requiring higher clearance levels, such as TS/SCI. These positions often come with premium responsibilities and significantly higher salaries. Even at the Secret clearance level, this certification can open doors to numerous opportunities, along with notable salary enhancements. Its alignment with the skills and expertise sought in cleared cybersecurity roles makes it a powerful tool for advancing within the cleared job market.

Which CCIE Security topics matter most for federal roles?

For federal positions, expertise in CCIE Security revolves around protecting complex enterprise and government networks, especially within high-security settings. Key focus areas include secure network architecture, VPNs, firewalls, intrusion prevention systems, and threat mitigation techniques.

A thorough understanding of federal regulations – like FISMA, NIST guidelines, and DoD standards – is essential. Additionally, being adept at troubleshooting and optimizing security infrastructure is crucial for safeguarding national infrastructure and classified data.

Related Blog Posts

  • GSEC Certification Career Guide for Cleared Security Essentials
  • Security Plus Certification Career Guide for Cleared Entry Level
  • Cisco CCNA Security Career Guide for Cleared Network Professionals
  • Cisco CCNP Security Career Guide for Cleared Network Engineers

Related Guides

  • Cisco CCNP Security Career Guide for Cleared Network Engineers
  • Cisco CCNA Security Career Guide for Cleared Network Professionals
  • Fortinet NSE Certification Career Guide for Cleared Network Security
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

Cisco CCNP Security Career Guide for Cleared Network Engineers

CyberSecJobs Editorial · March 5, 2026 ·

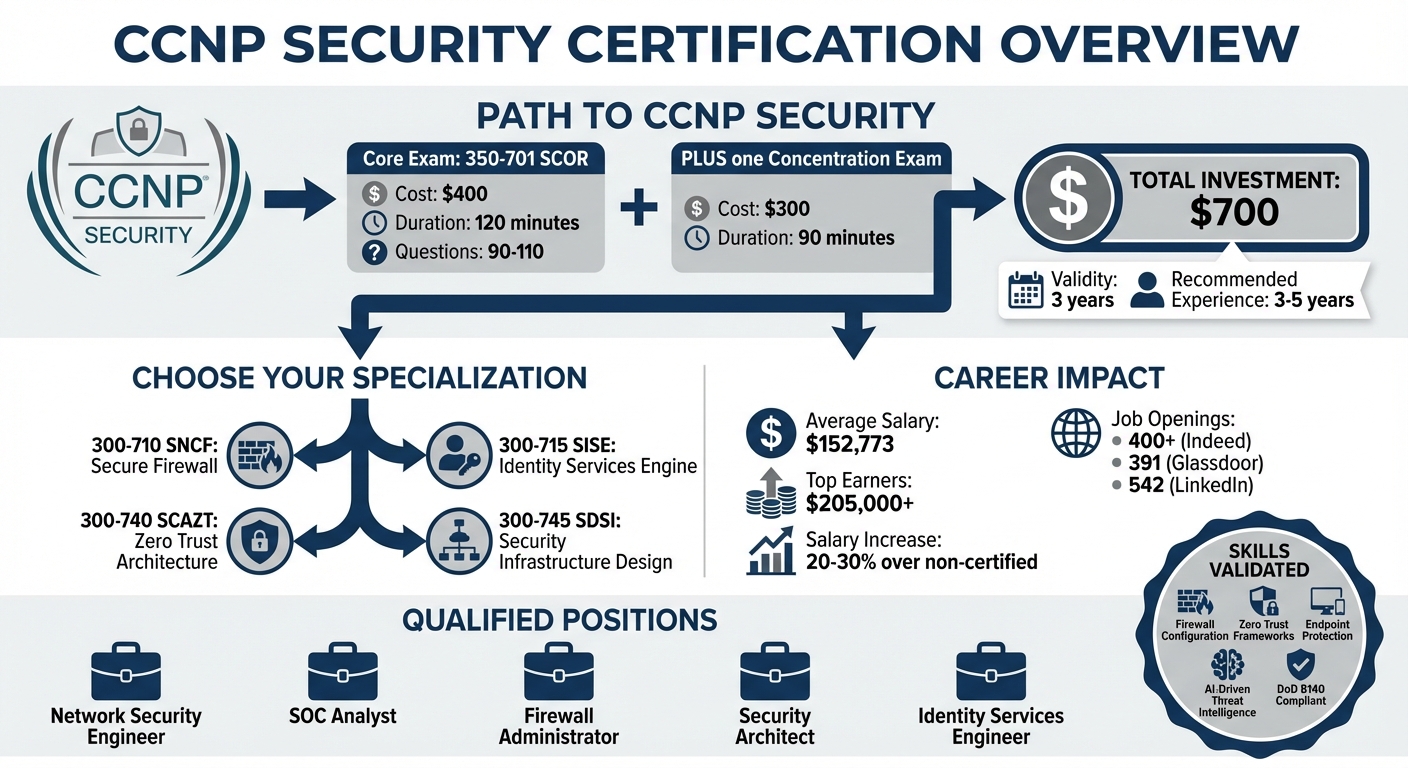
Looking to advance your career in government or defense cybersecurity? The Cisco CCNP Security certification is a top choice for security-cleared network engineers. It validates your expertise in securing Cisco infrastructures, aligns with DoD 8140 requirements, and opens doors to roles with salaries averaging $152,773 – with top earners exceeding $205,000.

Key Takeaways:

  • Certification Structure: Pass the 350-701 SCOR core exam ($400) and one concentration exam ($300). Total cost: $700.
  • Skills Gained: Firewall configuration, Zero Trust frameworks, endpoint protection, and AI-driven threat intelligence.
  • Updated Content: Includes quantum-safe security and NIST SP 800-37 frameworks (as of February 2026).
  • Career Opportunities: Qualifies you for jobs like Network Security Engineer, SOC Analyst, and Security Architect, often requiring Secret or Top Secret clearances.
  • Recertification: Valid for 3 years; renew via exams or 80 Continuing Education credits.

This certification not only boosts your technical skills but also positions you for high-demand roles in cybersecurity. Whether you’re starting your certification journey or aiming for senior positions, CCNP Security is a great investment for cleared professionals.

CCNP Security Certification Path: Exams, Costs, and Career Outcomes

CCNP Security Certification Path: Exams, Costs, and Career Outcomes

CCNP Security Certification: Structure and Skills

Required Core Exam and Optional Concentration Exams

To earn the CCNP Security certification, you’ll need to pass two exams: a mandatory core exam (350-701 SCOR) and one concentration exam of your choice. The core exam costs $400, while each concentration exam is priced at $300, bringing the total investment to around $700. While there are no official prerequisites, Cisco suggests having three to five years of hands-on experience with security solutions to prepare for these professional-level exams.

The 350-701 SCOR core exam is a 120-minute test with 90–110 questions. It focuses on a wide range of security technologies, including network security, cloud security, content security, endpoint protection, secure network access, and visibility enforcement. Successfully passing this exam not only earns you the CCNP Security core credential but also qualifies you to attempt the CCIE Security lab exam, which is ideal for those pursuing expert-level certification.

For the concentration exams, you can choose from several 90-minute options tailored to specific career paths:

  • 300-710 SNCF: Focuses on Cisco Secure Firewall, covering policy configurations, AI-driven threat intelligence, and cloud integration.
  • 300-715 SISE: Centers on Cisco Identity Services Engine (ISE), including BYOD policies, endpoint compliance, and network access control.
  • 300-740 SCAZT: Highlights Zero Trust architectures and Security Service Edge (SSE) for cloud environments.
  • 300-745 SDSI: Emphasizes designing complex security infrastructures and adopting emerging practices.

Important Note: Three older concentration exams – 300-720 SESA (Email Security), 300-725 SWSA (Web Security), and 300-730 SVPN (VPN Solutions) – will be retired on August 26, 2026. If you’re interested in these topics, you’ll need to complete the exams before this deadline. Additionally, the 300-735 SAUTO automation exam was retired on February 2, 2026.

With the exam structure outlined, let’s explore the specific skills this certification validates.

Skills Covered by CCNP Security

The CCNP Security certification equips you with the expertise needed to protect critical networks, including those in government and defense sectors. It validates your ability to tackle network security fundamentals, such as designing and managing firewalls, deploying intrusion prevention systems, and configuring secure remote access via VPNs. You’ll also gain skills in cloud security, including managing secure applications and implementing Zero Trust frameworks aligned with federal standards.

A major focus of the certification is endpoint protection and detection. You’ll learn how to secure devices, monitor for threats, and respond to incidents in distributed environments. Additionally, the certification covers identity services management through Cisco ISE, enabling you to control network access and enforce compliance policies for both employees and contractors. You’ll also gain proficiency in using visibility and enforcement tools to monitor network traffic, detect anomalies, and automate responses to security events.

Recent updates to the certification emphasize architectural design over just technical implementation. For instance, the 300-745 SDSI exam teaches you to design scalable security systems and integrate DevSecOps practices and SOAR (Security Orchestration, Automation, and Response) platforms into your architecture. These advanced skills prepare you for roles like Security Architect or Principal Engineer, where you’ll design entire security infrastructures rather than focusing on individual components.

Passing any concentration exam also earns you a Cisco Certified Specialist certification in that specific area, providing an additional credential to demonstrate your expertise. The CCNP Security certification remains valid for three years and can be renewed by completing any professional-level exam or earning 80 Continuing Education credits.

Getting Started with Cisco CCNP – Security

Cisco

Cleared Cybersecurity Jobs That Match CCNP Security Skills

This section highlights key cleared cybersecurity roles that align with the technical expertise validated by your CCNP Security certification. These roles are designed to meet strict federal standards and often require security clearances.

Top Cleared Roles for CCNP Security Professionals

Earning a CCNP Security certification qualifies you for several high-demand positions in the cleared cybersecurity space.

  • Network Security Engineers: These professionals design and implement secure architectures for government networks, configure VPN tunnels to enable secure communication between classified environments, and manage intrusion prevention systems. These roles typically require a Secret or Top Secret clearance.
  • Security Operations Center (SOC) Analysts: SOC analysts monitor network traffic, investigate potential security incidents, and respond to threats in real time. Defense contractors and intelligence agencies seek analysts skilled in Cisco network visibility tools.
  • Firewall Administrators: These roles involve managing access control policies, creating prefilter rules for classified networks, and ensuring compliance with federal security guidelines.

Other specialized positions include Identity Services Engineers, who deploy Cisco Identity Services Engine (ISE) for network access control, and Security Architects, who design infrastructures with integrated Zero Trust frameworks. These senior roles often require TS/SCI clearances and can offer salaries exceeding $150,000.

The following section breaks down how your CCNP Security skills align with these job responsibilities.

How CCNP Security Skills Match Job Requirements

The technical skills you developed through CCNP Security certification directly align with the responsibilities of these cleared roles. For example, if a job posting mentions expertise with next-generation firewalls, it refers to configuring access control policies and integrating threat intelligence – skills you’ve already mastered. Similarly, requirements for network visibility tools and secure remote access map directly to your experience with Cisco technologies like DMVPN and FlexVPN.

CCNP Security Skill Job Responsibility Relevant Technology
Firepower NGFW & IPS Configuring access control policies and prefilter rules for classified environments Cisco Firepower, FMC
Cisco Stealthwatch & Umbrella Providing network visibility and DNS-layer ransomware protection Stealthwatch, Umbrella
Identity Services (ISE) Managing secure access for end-user devices and enforcing compliance Cisco ISE, 802.1X
Email/Web Security Managing email policies and HTTPS decryption for government agencies ESA, WSA
Endpoint Protection Monitoring devices and responding to threats in distributed environments AMP for Endpoints, AnyConnect

As federal agencies shift toward Firepower Threat Defense, traditional ASA firewall roles are evolving, creating demand for professionals with next-generation firewall (NGFW) expertise – precisely what CCNP Security certification prepares you for. Additionally, the increasing emphasis on Zero Trust architectures aligns with the advanced training you’ve completed, especially in the related concentration exams.

sbb-itb-bf7aa6b

How to Prepare for and Earn CCNP Security Certification

To earn your CCNP Security certification, you need to pass the 350-701 SCOR core exam and one concentration exam. While there are no formal prerequisites, Cisco recommends having three to five years of hands-on experience with security solutions before attempting these professional-level exams. Keep in mind that recertification is required every three years.

Preparing for the Core Exam (350-701 SCOR)

The 350-701 SCOR exam is a 120-minute test with 90–110 questions covering six key areas: Security Concepts, Network Security, Securing the Cloud, Content Security, Endpoint Protection and Detection, and Secure Network Access/Visibility. This exam is not only essential for CCNP Security but also for CCIE Security, making it a smart choice for anyone planning long-term growth in the field.

To prepare effectively, combine structured study with practical lab work. Cisco U. offers learning paths with assessments to help you identify and address knowledge gaps. For hands-on practice, set up a virtual lab using tools like Cisco Modeling Labs (CML), GNS3, or Cisco Packet Tracer. Focus on tasks like configuring FlexVPN tunnels, creating Firepower policies, and deploying ISE solutions. Additionally, familiarize yourself with interpreting Python scripts for Cisco Security appliance APIs to tackle automation-related questions.

Plan for a 12–16 week study schedule, dedicating each week to a specific domain. Tools like Anki flashcards can help with memorizing cryptography and protocol details. Aim to consistently score 85% or higher on practice tests before scheduling your exam. During the test, manage your time wisely – spend no more than 60–75 seconds per multiple-choice question to leave time for simulation-based tasks. Results are typically available online within 48 hours, and passing the exam earns you the "Cisco Certified Specialist – Security Core" certification.

Mastering these study techniques not only prepares you for the exam but also builds the technical skills needed for critical security roles. Once you’ve completed the core exam, the next step is to select a concentration exam that aligns with your career goals.

Selecting Your Concentration Exam

Choosing the right concentration exam is crucial for aligning your certification with your career path. For example:

  • If you’re a Network Security Engineer focusing on threat detection and Cisco Secure Firewalls, the 300-710 SNCF exam is a great fit. This test now includes AI-driven threat intelligence and Cloud Control management as of the 2026 update.
  • For those managing Identity Services Engine (ISE), BYOD lifecycles, and network access policies, the 300-715 SISE exam is ideal.
  • Cloud Security Engineers working on Zero Trust and Secure Cloud Access should go for the 300-740 SCAZT exam.
  • If you’re aiming for a Senior Architect role, the 300-745 SDSI exam will prepare you with content on architectural design, AI threats, and quantum-safe concepts.

Keep in mind that some older exams have been retired, so always verify the latest exam offerings to ensure you’re focusing on relevant, in-demand skills.

Maintaining Your Certification

Once certified, keeping your CCNP Security credential active is essential to staying on top of evolving security technologies. The certification is valid for three years, and maintaining it ensures you’re prepared for new challenges and opportunities.

You have three options for recertification:

  • Pass any professional-level concentration exam.
  • Retake the 350-701 SCOR core exam.
  • Earn 80 Continuing Education (CE) credits. Activities like attending Cisco Live sessions, completing training courses, or publishing technical content can help you accumulate these credits.

The CE credit option is particularly helpful for busy professionals who may not have time for full exam preparation. Be sure to track your credits in your Cisco certification account to avoid lapses in your credential.

Staying certified not only keeps your skills sharp but also reinforces your value in the ever-changing world of security solutions.

Using CCNP Security to Advance Your Cleared Career

Earning a CCNP Security certification can significantly boost your career, especially in specialized cleared roles. On average, CCNP-certified professionals earn 20% to 30% more than their non-certified counterparts [4], with CCNP Security professionals bringing in an impressive annual salary of $152,773 [1]. But the benefits extend far beyond just financial gains – this certification opens doors to a range of exciting opportunities in the cybersecurity field.

Job Search Methods for Cleared Professionals

Landing the right cleared role requires a focused and strategic approach. Start by targeting job boards like Cleared Cyber Security Jobs, where you can search for positions requiring both your CCNP Security certification and your specific clearance level, such as TS/SCI. Setting up job alerts with keywords like "CCNP Security" and your clearance type ensures you’re among the first to respond to new opportunities. Unlike generic job boards, cleared roles come with strict requirements, so this tailored strategy saves time and effort.

In addition to job boards, aim for major federal contractors such as Booz Allen Hamilton, Leidos, and Lockheed Martin. Many of these companies offer referral bonuses, making networking with their employees a smart move. Attend hiring events and industry conferences geared toward cleared professionals – like INSA, NDIA, GEOINT, and AUSA – to connect directly with recruiters and program managers. Also, optimize your LinkedIn profile by including terms like "Security-Cleared Professional | TS Clearance | CCNP Security" in your headline, but avoid sharing sensitive details on unsecured platforms.

Location matters, too. Cleared roles are concentrated in areas like Northern Virginia, Maryland’s Fort Meade region, Colorado Springs, and Tampa/Orlando. Since many national security jobs require on-site work in secure facilities (SCIFs), you may need to consider relocating if you’re not already in one of these hubs.

Once you’ve secured a role leveraging your CCNP Security certification, you’ll find even more opportunities for growth and advancement.

Career Advancement Paths with CCNP Security

Your CCNP Security certification isn’t just a credential – it’s a launchpad for specialized and leadership positions. This certification qualifies you for roles like Network Security Engineer, Security Consultant, SOC Specialist, Information Security Analyst, Senior Network Architect, and IT Security Manager, among others [4]. It also serves as a stepping stone to the expert-level CCIE Security certification, as passing the 350-701 SCOR core exam fulfills the written exam requirement for CCIE [1][5].

"CCNP Security is not just another certification. It’s a globally recognized standard that proves an IT professional has the ability to secure networks, manage advanced security solutions, and protect data in today’s hostile cyber environment." – Troytec Exams [4]

To broaden your expertise, consider adding complementary certifications. For example, management-focused credentials like CISSP can prepare you for governance and strategy roles, while offensive security certifications such as CEH provide valuable insights into cyberattacks [2]. You can also expand your Cisco knowledge by pursuing concentration exams in areas like automation (300-735 SAUTO) or cloud security (300-740 SCAZT), aligning with the growing demand for automated security solutions and cloud-native technologies.

Career Examples from Cleared Network Engineers

The demand for CCNP Security professionals in the cleared job market is strong. As of early 2026, searches for "CCNP Security" on job platforms yielded over 400 results on Indeed, 391 on Glassdoor, and 542 on LinkedIn [1]. Some job postings even allow advanced certifications like CCNP Security to substitute for required work experience, giving you an edge early in your career [1].

The global cybersecurity talent shortage – estimated at over 3.4 million professionals as of 2024 – further amplifies your value [4]. With your CCNP Security certification and active clearance, you belong to an elite group of candidates that government contractors are eager to hire. This combination not only strengthens your job prospects but also enhances your ability to negotiate better salaries, benefits, and career opportunities.

Conclusion: CCNP Security for Cleared Cybersecurity Careers

CCNP Security can be a game-changer for cleared network engineers, offering an average salary of $152,773 [1] and paving the way to roles like Security Architect, Cloud Security Engineer, and SOC Analyst [3].

This certification aligns with DoD 8140 requirements and qualifies you for the CCIE Security lab exam [1], making it a key credential for cleared professionals aiming to advance their careers.

Industry voices highlight its value:

"The CCNP Security certification is still absolutely worth it if you are looking to advance in your cybersecurity career. The exam updates have made the certification even more future-proof by including AI threats and cloud-centered security concepts." – Graeme Messina, Author, CBT Nuggets [3]

With over 3.4 million cybersecurity jobs currently unfilled worldwide [4], the updated CCNP Security curriculum – featuring AI-driven threats, Zero Trust frameworks, and quantum-safe security [3] – keeps you ahead of the curve. When paired with an active security clearance, this certification sets you apart in a market where government contractors are actively searching for skilled professionals.

At just $700 for the core and concentration exams [1], this certification is a smart investment. Whether you’re transitioning from networking to security or aiming for leadership roles, CCNP Security equips you with the expertise needed to thrive in the ever-evolving cybersecurity landscape.

FAQs

Which CCNP Security concentration exam should I choose for my cleared role?

If you’re aiming for a CCNP Security certification, the best concentration exam depends on your specific role and expertise in cybersecurity. Begin with the 350-701 SCOR core exam, which lays the foundation by covering essential topics like network and cloud security.

From there, pick a concentration exam that matches your professional focus. For example:

  • 350-702 SECURE: Ideal for those concentrating on threat detection and protection.
  • 350-704 CLCON: A great choice if your work revolves around secure access solutions.

Choose the path that aligns best with your career aspirations and current skill set.

How do I build a CCNP Security lab at home without using classified systems?

To set up a CCNP Security lab at home without relying on classified systems, you can use physical devices like Cisco 3550 switches or 2600 routers. Alternatively, virtualization tools such as GNS3, Cisco VIRL, or EVE-NG are excellent options. These tools allow you to design and configure network topologies that include routers, switches, firewalls, and VPNs, providing hands-on experience with security policies and troubleshooting.

Make sure that all the equipment and software you use comply with legal standards and are non-classified. At the same time, ensure your setup aligns with the requirements of the CCNP Security exam to get the most relevant practice.

Does CCNP Security help me meet DoD 8140 requirements for cleared jobs?

The CCNP Security certification aligns with the DoD 8140 requirements and is officially recognized as a DoD-approved credential. This certification helps professionals meet qualification standards for roles requiring security clearance, making it an important asset for those looking to enter or advance in the cleared job market.

Related Blog Posts

  • Security Plus Certification Career Guide for Cleared Entry Level
  • CCSP Certification Career Guide for Cleared Cloud Security
  • Palo Alto PCNSE Career Guide for Cleared Firewall Engineers
  • Cisco CCNA Security Career Guide for Cleared Network Professionals

Related Guides

  • Cisco CCIE Security Career Guide for Cleared Expert Engineers
  • Cisco CCNA Security Career Guide for Cleared Network Professionals
  • Fortinet NSE Certification Career Guide for Cleared Network Security
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers

Cisco CCNA Security Career Guide for Cleared Network Professionals

CyberSecJobs Editorial · March 5, 2026 ·

Want to boost your career in cybersecurity? The Cisco CCNA Security certification is a powerful tool for cleared professionals aiming to secure high-demand roles in defense and federal sectors. With over 540,000 unfilled cybersecurity positions in North America and a global shortage of 4.7 million professionals, this certification can set you apart. Here’s what you need to know:

  • Why It Matters: Proves your ability to secure networks and manage vulnerabilities. Recognized by the Department of Defense and aligns with the latest technologies, including AI and machine learning.
  • Earnings Potential: CCNA-certified professionals earn 20–30% more, with salaries ranging from $60,000 to $120,000.
  • Accessibility: No prerequisites required. Military personnel can use programs like "COOL Bucks" or GI Bill reimbursement to cover the $300 exam fee.
  • Career Growth: Opens doors to roles like ISSO and Cyber Threat Intelligence Analyst, with paths to advanced certifications like CCNP Security.

Whether you’re transitioning into cybersecurity or aiming for leadership roles, this certification is a smart step forward.

CCNA Security Certification Career Benefits and Statistics for Cleared Professionals

CCNA Security Certification Career Benefits and Statistics for Cleared Professionals

Cisco Security Workbook and Lab Guide – Free [CCNA Security]

What Is the Cisco CCNA Security Certification?

The Cisco CCNA Security certification showcases your ability to secure network infrastructures and handle cybersecurity threats effectively. In 2020, Cisco merged its associate-level tracks into the CCNA (200-301), integrating key security principles with essential networking topics [4]. Although the standalone CCNA Security track is no longer available, security concepts remain crucial for professionals tasked with protecting government networks. This certification demonstrates skills like configuring firewalls, implementing VPNs, and managing secure access controls – key capabilities for safeguarding classified systems [3]. These foundational skills pave the way for diving into the exam’s specifics and requirements.

Certification Scope and Core Topics

The current CCNA dedicates 15% of its curriculum to security fundamentals, covering areas like VPN technologies, Access Control Lists (ACLs), wireless security, and secure access management [4]. For professionals aiming for specialized security roles, these topics are a stepping stone toward advanced certifications such as CCNP Security or CyberOps [4] [9]. Key technical competencies include configuring Cisco ASA firewalls, setting up site-to-site and remote access VPNs, and managing Authentication, Authorization, and Accounting (AAA) systems. These skills align with Department of Defense (DOD) requirements for protecting government infrastructure, focusing on threat mitigation and secure access [3].

The CCNA also addresses automation and programmability (10% of the exam), reflecting the growing importance of software-defined networking in secure environments [4]. This includes using tools like APIs, Python, and Ansible to automate security configurations – skills highly sought after in cleared cybersecurity roles [6] [9]. With Cisco commanding nearly 40% of the enterprise networking market share as of 2025, these vendor-specific skills remain indispensable for federal agencies and defense contractors [4].

Prerequisites and Requirements

The CCNA (200-301) has no formal prerequisites, making it accessible to those transitioning into network security roles [4]. Previously, candidates for the CCNA Security track needed certifications like CCENT, CCNA Routing and Switching, or CCIE [3] [8]. To earn the certification, you must pass the 200-301 exam and agree to Cisco’s Career Certifications Confidentiality Agreement and Candidate Conduct Policy [3]. Cleared professionals should also confirm that their certification satisfies the DOD 8140/8570 framework for their specific job roles [3].

Service members can take the exam at Pearson VUE centers on military bases and use "COOL Bucks" (Credentialing Opportunities On-Line) to cover exam fees [3]. Allocate around 10–12 hours per week for 3–4 months to prepare, and use tools like Cisco Packet Tracer, GNS3, or EVE-NG to practice real-world network configurations [4]. Kevin Brown, a Cybersecurity Analyst, highlights the importance of certifications:

"Certifications give you instant credibility. People always want to know who they’re talking to. They want to know if you’re qualified." [7]

Exam Cost and Format

The CCNA (200-301) exam costs approximately $300, and military personnel can often use programs like "COOL Bucks" to cover the fee [3] [4]. The exam lasts 120 minutes and features multiple-choice questions, drag-and-drop exercises, and hands-on lab simulations designed to test your ability to configure secure networks in practical scenarios [4]. Security-related topics make up 15% of the exam [4].

The certification is valid for three years, after which you can recertify by passing a new associate-level exam, a professional-level exam like CCNP Security (350-701 SCOR, $400), or by earning Continuing Education (CE) credits [3] [7] [9]. Keeping your certification up to date ensures you stay ahead of technological advancements and remain competitive for advanced cybersecurity roles. Cleared professionals should consult their Education Service Officer to confirm eligibility for voucher reimbursements or promotion points [3].

Cleared Jobs That Require CCNA Security

Common Cleared Job Roles

CCNA Security credentials play a key role in meeting the growing demands of today’s cleared cybersecurity positions. Professionals holding these certifications are essential for maintaining cybersecurity standards in government and defense sectors. For instance, a March 2026 posting for a Network Engineer in Orlando, FL, required candidates to have an active security clearance, a CCNA certification, and expertise in applying STIGs while supporting RMF/DIACAP processes [11].

Cleared positions are increasingly looking for candidates who can combine networking expertise with cybersecurity skills. Employers often prioritize familiarity with tools such as the Assured Compliance Assessment Solution (ACAS), Nessus, and the Host Based Security System (HBSS). Many of these roles also require knowledge of RMF processes, NIST regulations, and NIST SP 800-53 standards. Gaining experience in these areas can open doors to a variety of opportunities and help professionals advance their cleared careers.

Industries Hiring CCNA-Certified Cleared Professionals

Several industries actively seek professionals with CCNA Security credentials and security clearances. These include the U.S. Department of Defense, Intelligence Community, federal agencies, and defense contractors. The skills outlined earlier directly align with the needs of these sectors. For example, organizations like the Air Force, Navy, and the Defense Information Systems Agency (DISA) regularly hire for roles in network administration and security. These positions often require Secret or Top Secret clearances and focus on safeguarding the network infrastructures that support critical military operations.

In the Intelligence Community, cleared roles – often requiring TS/SCI clearance with a polygraph – demand network security expertise to protect highly sensitive information. Federal civilian agencies, such as the Department of Commerce, and defense contractors working on government programs also seek cleared network engineers. Highlighting your experience with compliance standards when applying for these roles can significantly strengthen your application.

How to Use CCNA Security in Your Cleared Job Search

Adding CCNA Security to Your Resume and Profile

Your CCNA Security certification can be a powerful asset in landing a cleared job. To make the most of it, ensure it’s prominently displayed in your resume header. Pair it with your clearance level for maximum impact – for instance, "John Doe, CCNA Security, Active Secret Clearance." This way, recruiters can immediately spot your qualifications.

"Your security-cleared resume is not a biography or a mere list of qualifications. It’s an ad designed to help you land that coveted cleared job interview." – Ashley Jones, Editor, ClearedJobs.Net [12]

At the top of your resume, include a professional summary that highlights both your certification and experience. For example: "Network Security Specialist with CCNA Security and 5+ years of experience securing DoD communications infrastructure." This summary sets the tone for your expertise. When detailing your work history, use the STAR method to quantify your accomplishments. For example: "Reduced network vulnerabilities by 35% through proactive Cisco ASA firewall monitoring" [12][13].

If you’re still working toward your CCNA Security certification, list it as "CCNA Security (In-Progress)" along with your expected completion date. According to CyberSecJobs.com, including certifications in progress can make a big difference, especially if they’re a hard requirement for the role [13]. Tailor your resume for each job by incorporating specific technical terms from the posting, such as "Cisco ASA", "VPN", "network security", or "NIST-compliant." This not only aligns your skills with the job but also helps you get through Applicant Tracking Systems (ATS) [13][14].

Once your resume is polished, the next step is to refine your job search strategy.

Finding CCNA Security Jobs on Cleared Cyber Security Jobs

When searching for jobs, use phrase searches on Cleared Cyber Security Jobs. For precise results, place "CCNA Security" in quotation marks. To broaden your search, try Boolean operators like "CCNA Security" OR "Network Security Engineer." You can then narrow the results using "AND" to filter by clearance level or location. This focused approach can help you navigate the competitive hiring landscape for cleared professionals [15].

After crafting an effective search query – such as "CCNA Security" AND "Secret" – save it as a Job Agent. This feature will send you email alerts whenever a matching position is posted. For location-based searches, use a Zip Code with a mileage radius instead of city names. This ensures you capture jobs at nearby military installations that might be listed under different suburbs [15]. Additionally, logging in weekly keeps your profile active and visible to recruiters, as employers often prioritize candidates with recent activity [15].

sbb-itb-bf7aa6b

Career Growth with CCNA Security in Cleared Cybersecurity

Moving to Advanced Cisco Certifications

Earning your CCNA Security is just the beginning – it sets you up for a clear path to advanced Cisco certifications. The next step? The CCNP Security, which costs $700 in total. This includes $400 for the core 350-701 SCOR exam and $300 for one concentration exam [18]. With this professional-level certification, you can specialize in high-demand areas like Cisco Firepower (SNCF), Identity Services Engine (SISE), or VPN technologies (SVPN) [6]. These specializations align perfectly with the requirements of many cleared contracts, making you a strong candidate for senior engineering roles.

On average, CCNP Security holders earn $107,000 annually, up from the $75,000–$87,000 range typical for CCNA-certified professionals [18]. This certification also shifts your role toward solving more strategic and complex problems. For those with even greater ambitions, the CCIE Security represents the pinnacle of technical certifications in the industry. Achieving it involves passing a $400 written exam and an intense eight-hour hands-on lab exam, which costs between $1,600 and $1,900 [18].

"Certifications give you instant credibility." – Kevin Brown, Cybersecurity Analyst [18]

Before advancing to professional or expert certifications, it’s crucial to have strong networking fundamentals [18]. Passing a CCNP exam not only renews your CCNA certification but also moves you closer to expert-level credentials [17]. Beyond the technical benefits, these certifications can also pave the way to leadership opportunities.

Advancing to Leadership Positions

As you climb the career ladder, your CCNA Security remains a key building block for success in cleared cybersecurity. While it validates your technical expertise, it also opens doors to leadership roles by demonstrating your ability to enforce security policies and oversee monitoring efforts [6]. Becoming the "go-to person" for security-related challenges in your organization enhances your visibility, which can lead to management opportunities [18]. Notably, 91% of employers consider IT certifications a reliable indicator of employee success [18].

With a CCNA Security as your foundation, you could advance into roles like Cybersecurity Architect (earning $96,383–$124,947), Information Security Manager ($139,577–$167,911), or even Chief Information Security Officer ($219,741–$276,993) [16]. To reach these high-level positions, you might want to pair your CCNA with management-focused certifications like CISM or CISSP, which costs about $749 [16]. This combination of technical expertise and strategic skills positions you to lead Security Operations Center (SOC) teams and shape enterprise-wide security strategies [16].

The cleared cybersecurity sector has seen explosive growth, with a 350% increase in jobs between 2013 and 2021 [18]. Despite this growth, 53% of organizations report a 10% gap in staffing, highlighting the demand for certified professionals. Your CCNA Security could be the springboard that transforms you from a technical expert into a strategic leader [18].

Keeping Your CCNA Security Certification Current

Recertification Requirements and Timeline

Your CCNA certification stays valid for three years, with no extensions allowed [19][20]. To renew it, you have a few options: retake the CCNA (200-301) exam for $300, pass a professional concentration exam ($300), complete a technology core exam like CCNP Security Core 350-701 ($400), or earn 30 Continuing Education (CE) credits within the three-year period [10][20]. Attending Cisco Live events can earn you 10–15 credits per event while also exposing you to trending technologies like automation and SD-WAN [19]. Combining exam prep with continuing education can even speed up career promotions by 40% [19].

To stay on top of your recertification, set quarterly reminders to check the Cisco Certification Tracking System for updates and credit opportunities [19]. While Cisco does send email reminders at key intervals – two years, one year, 90, 60, and 30 days before expiration – it’s smart to plan at least six months ahead to avoid a last-minute scramble [19]. Letting your certification expire means you’ll need to start over and retake the full exam process [20].

Keeping your certification active isn’t just about convenience – it’s about value. An active certification can boost your salary by 18%, while an expired one might reduce its relevance by 12%. Additionally, professionals with active certifications are 2.6 times more likely to receive recruiter messages on LinkedIn, especially during periods of technological change [19]. Staying updated with cybersecurity trends ensures your recertification efforts directly support your career growth.

Staying Updated with Cybersecurity Changes

Recertification is important, but keeping up with industry trends is equally essential to stay competitive. For instance, automation concepts now make up 20% of the current CCNA exam, and 67% of networking job postings highlight Python scripting as a key skill [19]. With automation and AI-driven networks becoming more prominent, credits related to automation topics are now 35% more in demand compared to traditional routing subjects [19].

To avoid burnout, aim to dedicate just 30 minutes a week to training modules or study groups to steadily earn your credits [19]. Cisco also offers training badges in specialized areas like zero-trust architecture, which can quickly demonstrate your expertise in emerging technologies [19]. These micro-credentials can help you stand out, especially since 82% of hiring managers prioritize candidates with valid certifications for senior-level roles [19].

"Your expertise is like a smartphone – regular updates keep it running smoothly in our fast-paced digital world." – Editorial Team, CCNA-Classes [19]

Engaging with professional communities like the Cisco Learning Network forums is another great way to stay informed about exam updates and troubleshoot complex challenges [19]. For professionals working in roles tied to DoD 8570/8140 standards, maintaining an active certification isn’t just helpful – it’s often a job requirement [21]. An active certification proves your skills are up-to-date, while letting it lapse could mean starting over from scratch [21].

Conclusion and Next Steps

Key Points to Remember

Earning this certification is a game-changer for security-cleared professionals aiming to advance in government and defense sectors. The CCNA certification confirms your expertise in securing Cisco networks, building robust security systems, and countering threats effectively [1][3]. It’s highly regarded by prominent agencies like the National Security Agency (NSA) and the Committee on National Security Systems (CNSS) [22], making it a valuable credential for federal roles in fields like Computer Engineering and Information Technology Management [3]. Given Cisco’s stronghold in the market [4], this certification opens doors to lucrative opportunities with competitive salaries.

But it doesn’t stop there. The CCNA is also a stepping stone to pursuing advanced certifications [4][5][6]. The current CCNA (200-301) exam, updated as of August 2024, now covers topics like AI, machine learning, and cloud management – skills that are increasingly critical. With networking roles tied to cybersecurity expected to grow by 20% annually through 2030 [4][2], and a global shortage of 4.7 million cybersecurity professionals [2], your certification places you in a prime position for success.

With these advantages in mind, you’re well-equipped to take the next step in your cybersecurity career.

What to Do Next

Here’s how to turn your certification into actionable career growth:

  • Search for Cleared Roles: Visit Cleared Cyber Security Jobs to explore positions tailored for security-cleared professionals. Upload your resume, set up job alerts, and use filters to find roles that specifically require or prefer CCNA certification. Highlight your credential prominently in your profile to stand out.
  • Schedule Your Exam: If you haven’t taken the CCNA (200-301) exam yet, book it through Pearson VUE for $300 [4]. Use practical simulation tools to prepare for the hands-on components [4][5].
  • Plan for Recertification: If you’re already certified, mark your calendar six months before your certification’s three-year expiration date. Decide whether to retake the exam or pursue a more advanced certification to maintain your edge.
  • Stay Current: Dedicate 30 minutes a day to learning about automation and AI-driven networking trends. This will ensure your skills remain relevant in a fast-changing industry.

FAQs

Is CCNA still worth it if CCNA Security was retired?

Yes, the CCNA certification is still highly relevant, even with the retirement of CCNA Security. The updated CCNA now includes a wider scope of networking fundamentals, which also integrates security concepts. This makes it an excellent choice for professionals aiming for roles like network engineers or cybersecurity specialists. Globally recognized, it confirms critical skills and ensures that individuals are equipped to handle modern networking and security challenges, especially within Cisco-based environments.

Which cleared roles does CCNA help me qualify for?

The CCNA certification opens doors to roles such as Network Security Specialist, Security Administrator, and Network Security Support Engineer. These positions are centered around creating secure network infrastructures, detecting potential threats, and resolving vulnerabilities effectively.

How do I make CCNA stand out on a cleared resume?

To help your CCNA certification shine on a cybersecurity resume, focus on emphasizing your technical skills, certifications, and accomplishments in a clear and organized way. Start by placing your certifications prominently near the top of your resume, ensuring they grab attention immediately. Include a brief, impactful summary of your professional experience, and customize your resume to match the specific job description by incorporating relevant keywords.

Make sure to highlight your expertise in network security, your proficiency with Cisco technologies, and how your CCNA aligns with your security clearance. This combination can effectively underscore your qualifications for roles requiring clearance and technical expertise.

Related Blog Posts

  • GSEC Certification Career Guide for Cleared Security Essentials
  • Security Plus Certification Career Guide for Cleared Entry Level
  • CySA Plus Certification Career Guide for Cleared SOC Analysts
  • CCSP Certification Career Guide for Cleared Cloud Security

Related Guides

  • Cisco CCIE Security Career Guide for Cleared Expert Engineers
  • Cisco CCNP Security Career Guide for Cleared Network Engineers
  • Fortinet NSE Certification Career Guide for Cleared Network Security
  • Cybersecurity Salary Guide 2026
  • TS/SCI Salary Premium: Real 2026 Numbers
  • « Go to Previous Page
  • Go to page 1
  • Interim pages omitted …
  • Go to page 39
  • Go to page 40
  • Go to page 41
  • Go to page 42
  • Go to page 43
  • Interim pages omitted …
  • Go to page 68
  • Go to Next Page »
  • Facebook
  • Instagram
  • LinkedIn
  • Twitter
  • YouTube

Cleared Cyber Security Jobs | CyberSecJobs.com

  • Contact
  • About
  • Privacy Policy